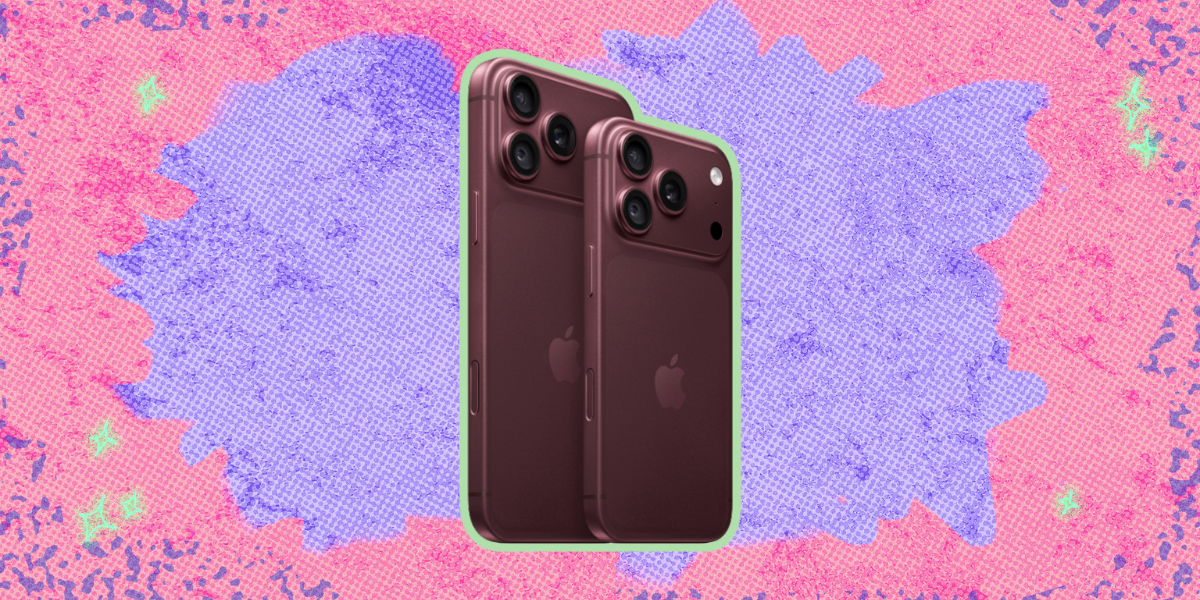
All the phones T-Mobile is giving away for free right now (including the iPhone 18 Pro)
T-Mobile's September free phone deals feature the new Apple iPhone 18 Pro, Samsung Galaxy Z Fold 8, and Google Pixel 11.
What's breaking now, across thousands of outlets.
T-Mobile's September free phone deals feature the new Apple iPhone 18 Pro, Samsung Galaxy Z Fold 8, and Google Pixel 11.
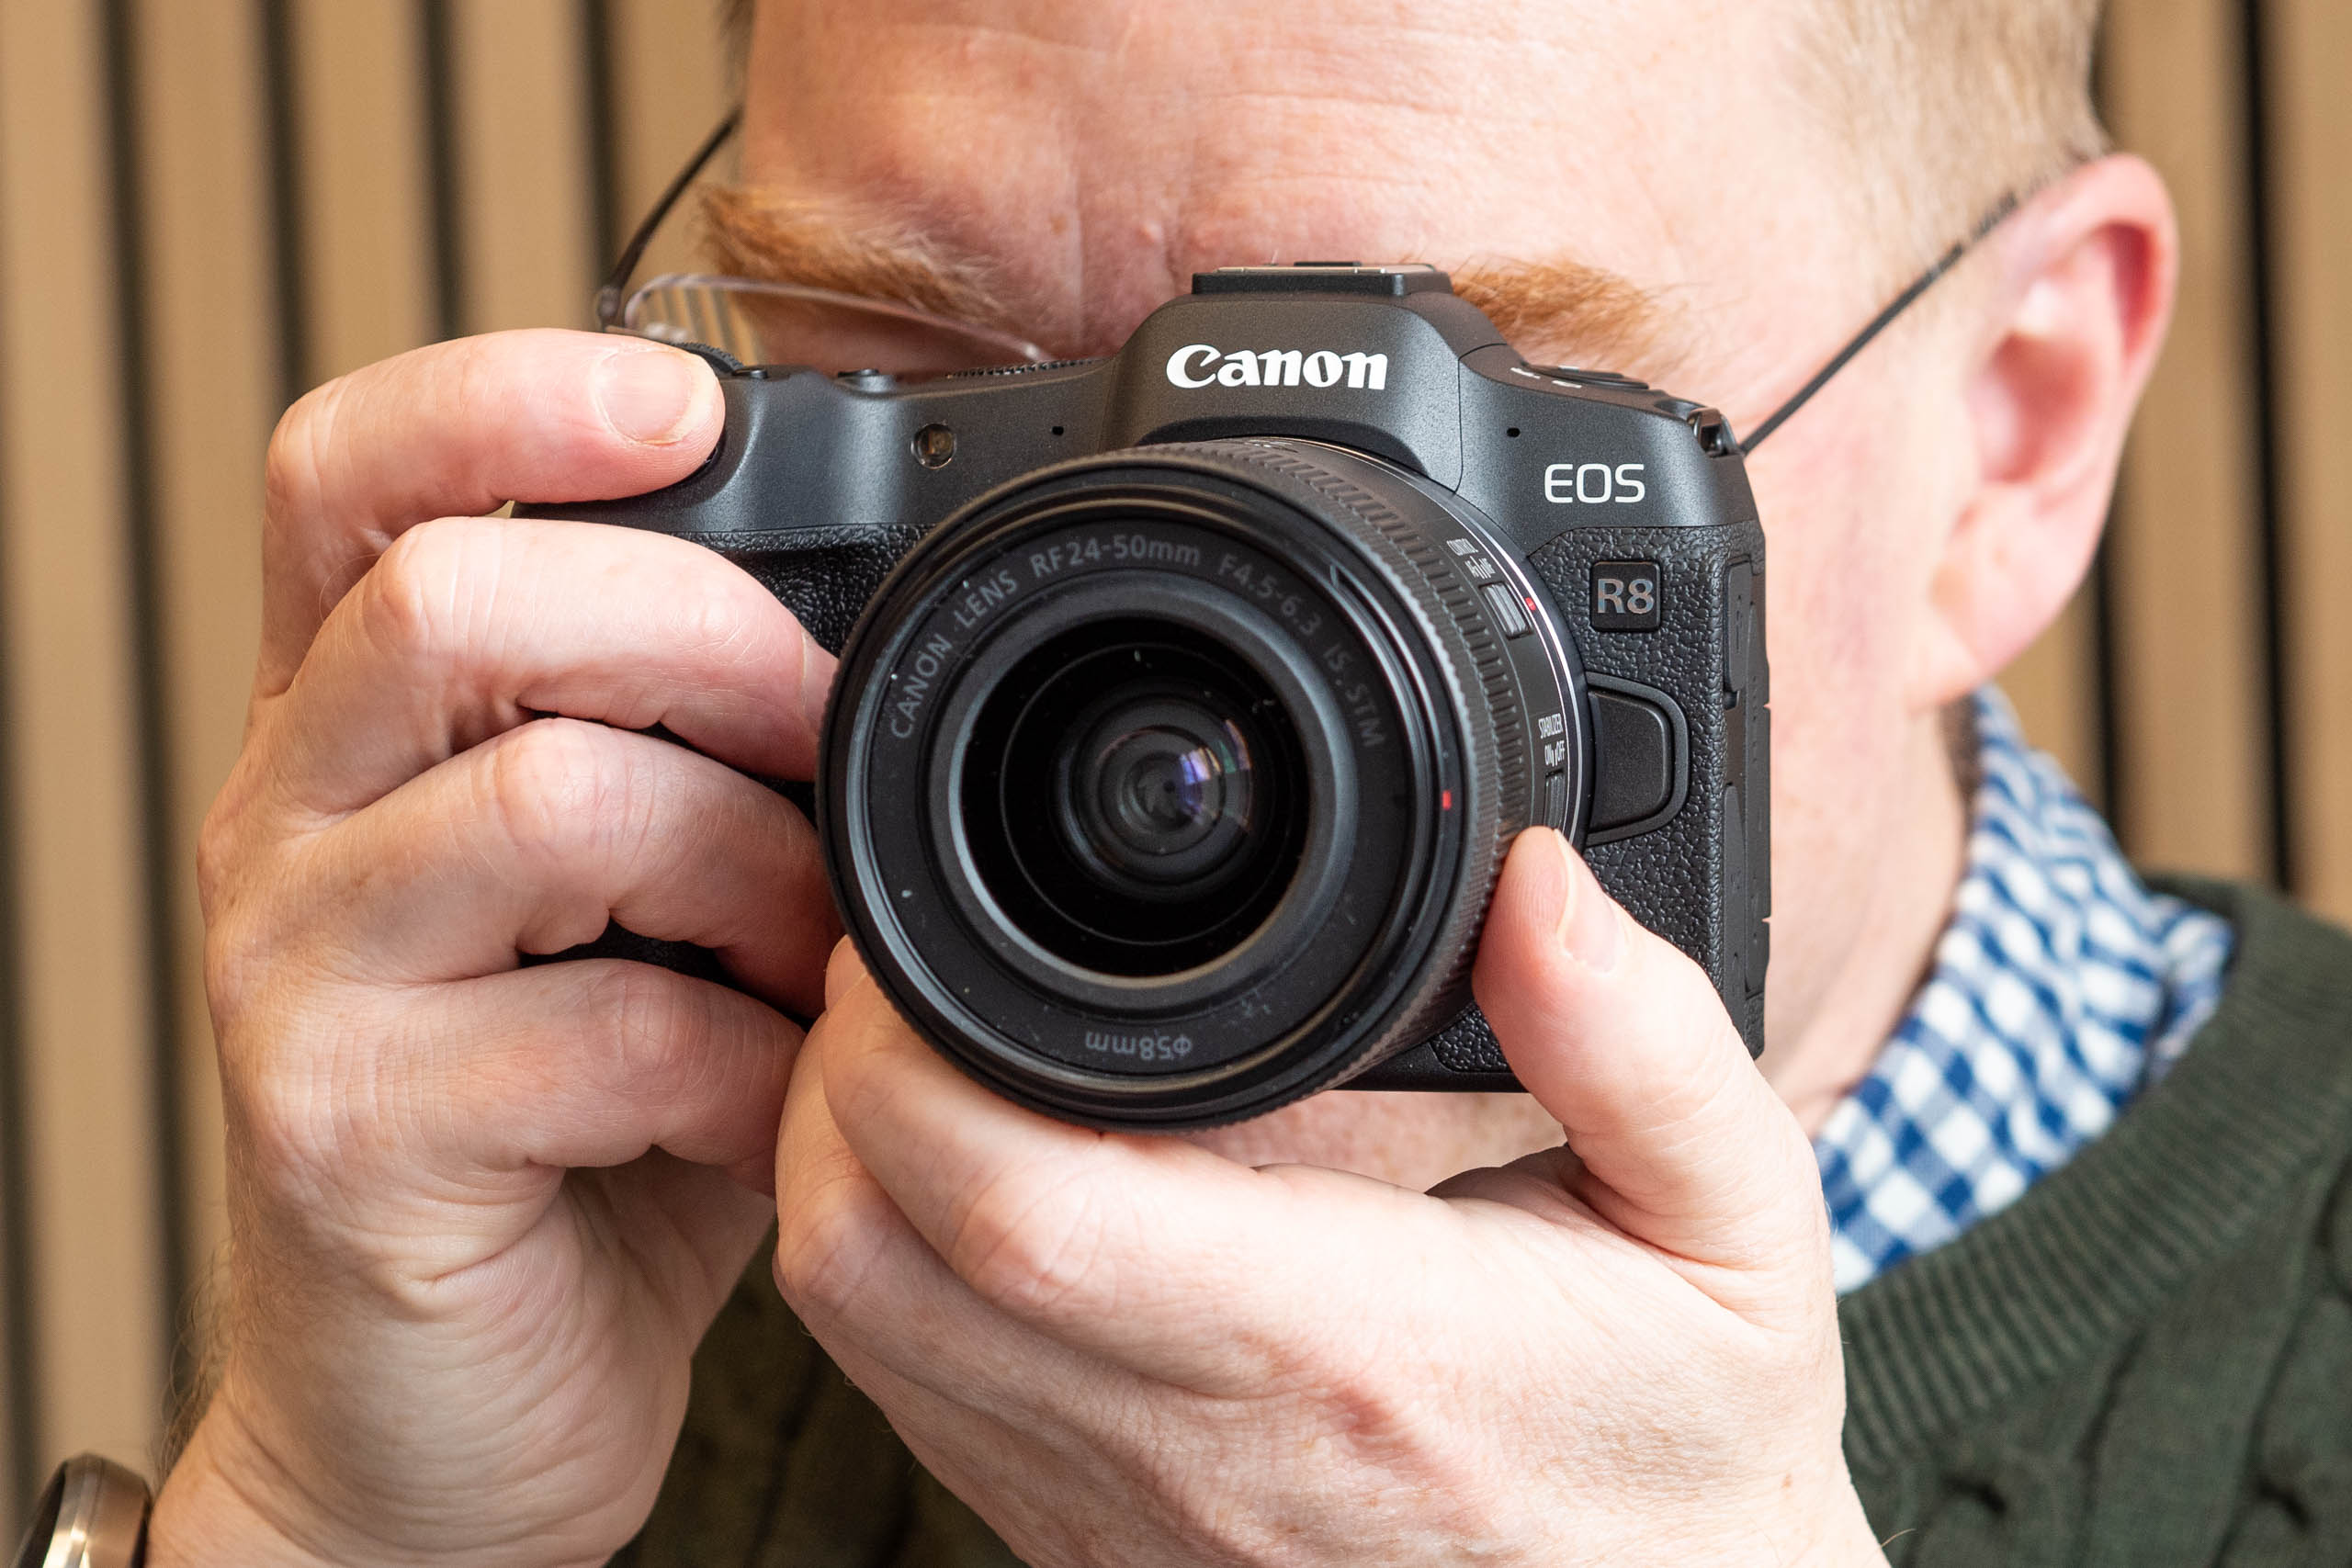
If you are in the market for a high-resolution, full-frame mirrorless camera check out these tempting deals from top maker, Canon The post Cash in with big Canon full-frame camera discounts this week!
Two articles ago I wrote that the Postgres role which runs your migrations bypasses every row-level security policy. Last week I wrote that with one tenant in the fixture, your isolation suite passes…
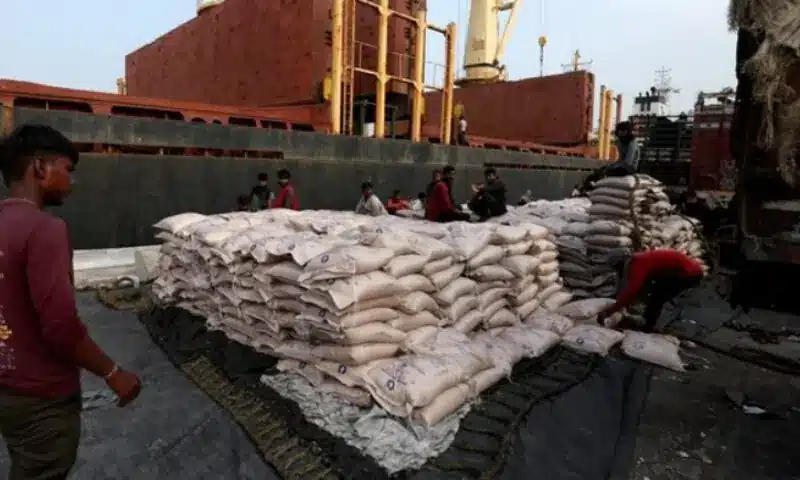
The Economic Coordination Committee (ECC) of the federal cabinet on Monday approved the export of 200,000 metric tons of surplus … Read More The post Cabinet Allows Export of 200,000 Tons Surplus…
Verifying every number in a draft against its source does not make the draft honest. I learned that on my own writing pipeline.
The rule is that every block of code stands under a declared owner, so that for any function you can ask which stated responsibility it serves and get one answer. The rule had existed for a while.
iMazing is a powerful tool for gaining pro-level control of your iPhone and iPad on your Mac or PC. A major new release is coming soon, and the popular utility is now offering a 20% discount for 9to5Mac readers . Here’s everything iMazing has been working on lately and a glimpse of what’s coming up. more…
Civil society groups say Equinix’s data centre was approved without considering its impact on nearby communities
As local models become more capable, AI agents can handle more work directly on a PC while keeping sensitive information on the device.
Between respectably powerful, cheap laptops, handhelds like the Steam Deck and the new generation of mini-PCs like the Steam Machine, it’s easier than ever to dip into the vast ocean of PC games.
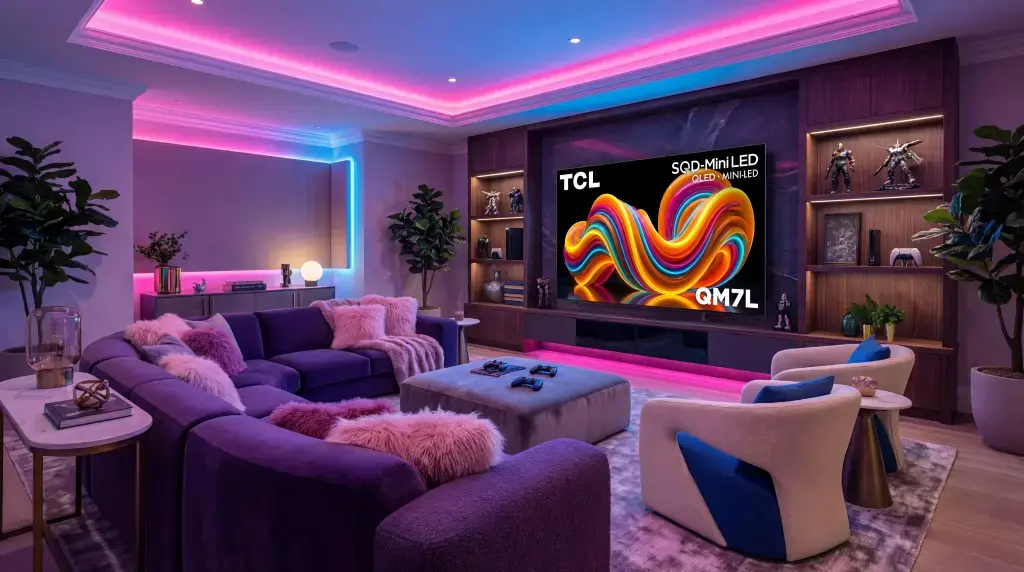
The TCL 65-inch QM7L SQD-Mini LED QLED 4K TV is on sale at Amazon for over $600 off its retail cost. That's its best price ever.
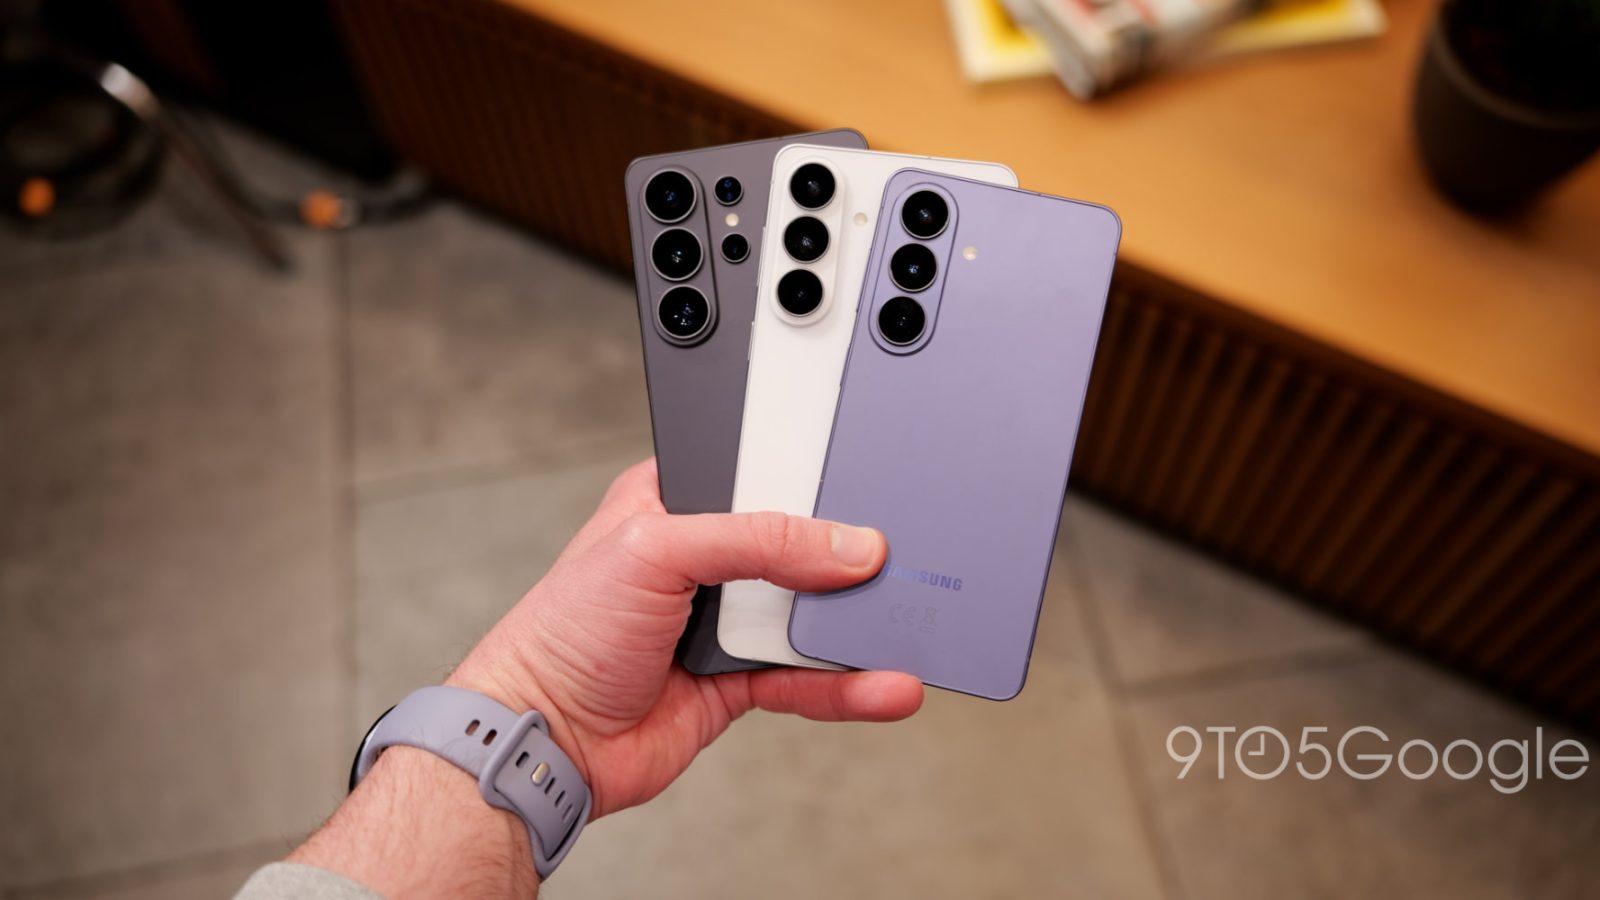
In the era of RAMageddon, the price hikes just keep coming. Samsung has left its Galaxy S26 untouched thus far, but a new report suggest prices hikes of around $100 could be on the way. more…
Kirinyaga youths are turning to technology to tackle unemployment and create new income opportunities through KiriMarket, a digital platform launched in Kagio on Monday, September 14, 2026.
Article URL: https://pop.rdi.sh/dario-please/ Comments URL: https://news.ycombinator.com/item?id=49697893 Points: 267 # Comments: 140
I've never been happier to be a support main.
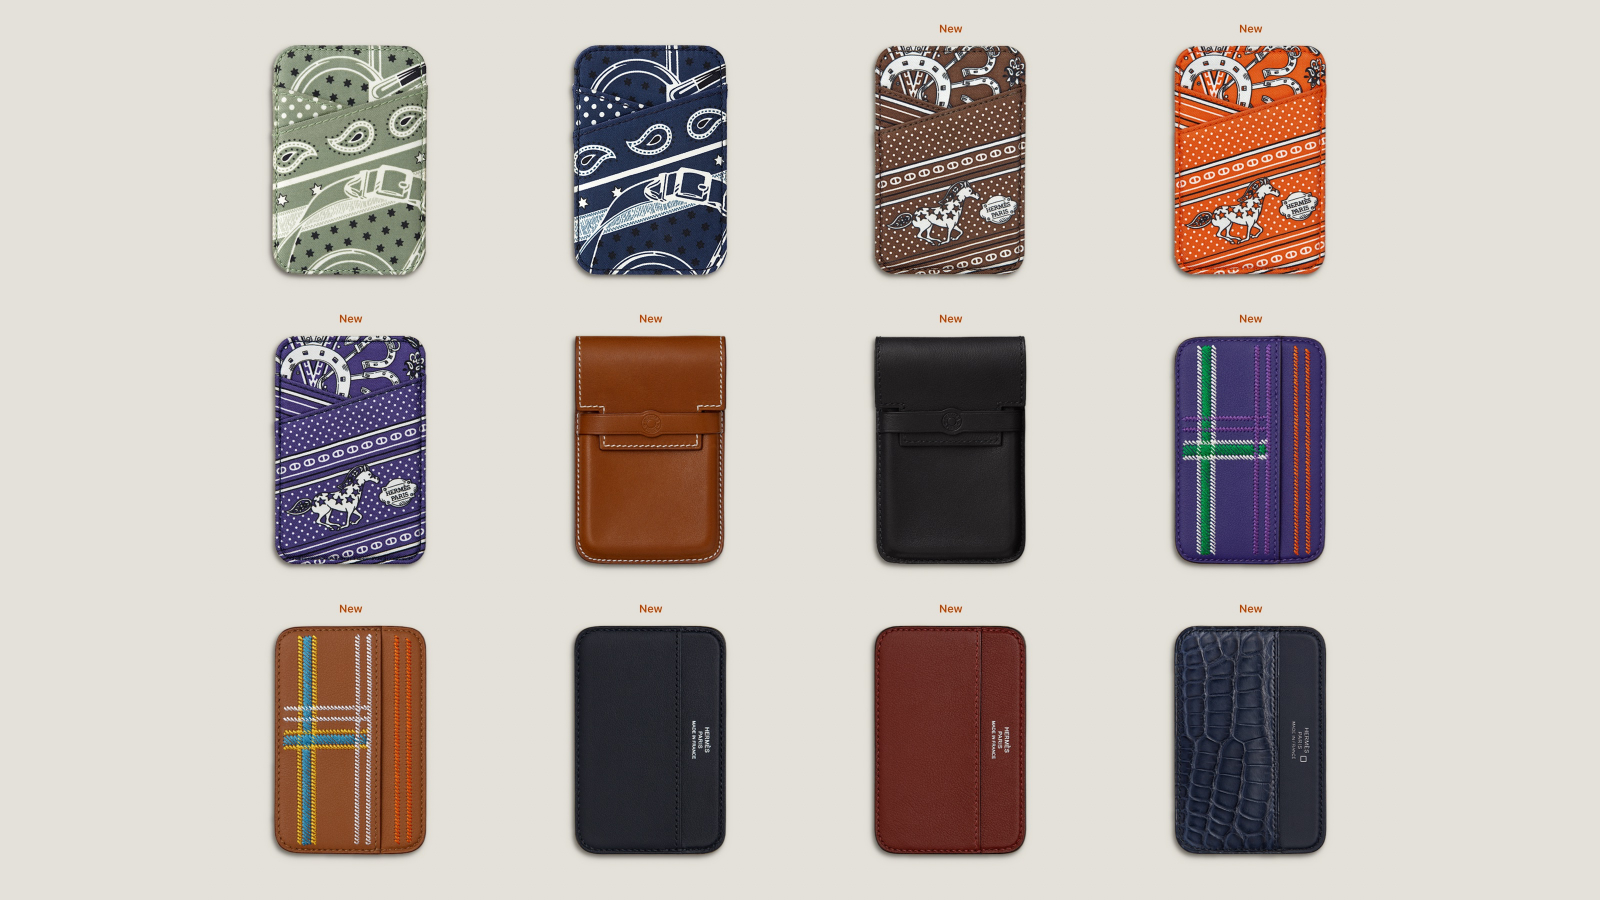
iOS 27 code reveals a wave of new Hermès MagSafe wallet designs featuring Find My support, alongside a dedicated attachment animation for the accessories.
The Economic Coordination Committee (ECC) of the federal cabinet on Monday approved Rs. 75 billion for the Prime Minister’s Fuel … Read More The post Govt Approves Rs.
SAPS is urging people to protect their personal information and take basic precautions before meeting someone they first encountered online.
The collection spans PlayStation support pages, store listings, and official blog posts, with live links, archived snapshots, and highlighted screenshots showing exactly where Sony uses ownership…
Linux 7.1 brought some performance improvements for Intel Core Ultra Series 3 "Panther Lake", Linux 7.2 enhanced the performance for the integrated Arc B390 Xe3 graphics, and now for the…
Revolut is now being asked to pay a humongous ransom demand to keep the data private.
A Texas judge found TikTok liable for misleading parents about child safety controls, shifting the case toward penalties and possible restrictions.
Save $120 on the 41mm Pixel Watch 4 LTE and get Wear OS, Fitbit tracking, and phone-free calling in one deal.
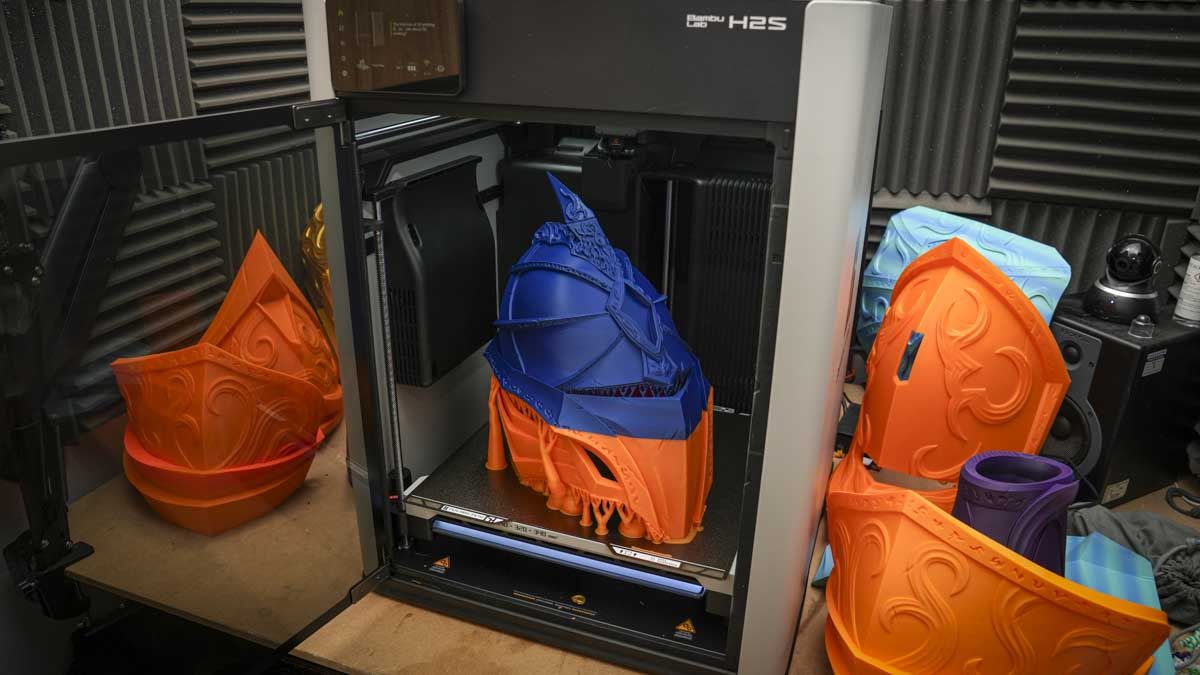
Scoring the Bambu Lab H2S 4.5 stars with a TechRadar Pro Recommends award, we found this large-scale 3D printer was fast, reliable, and impressively accurate.
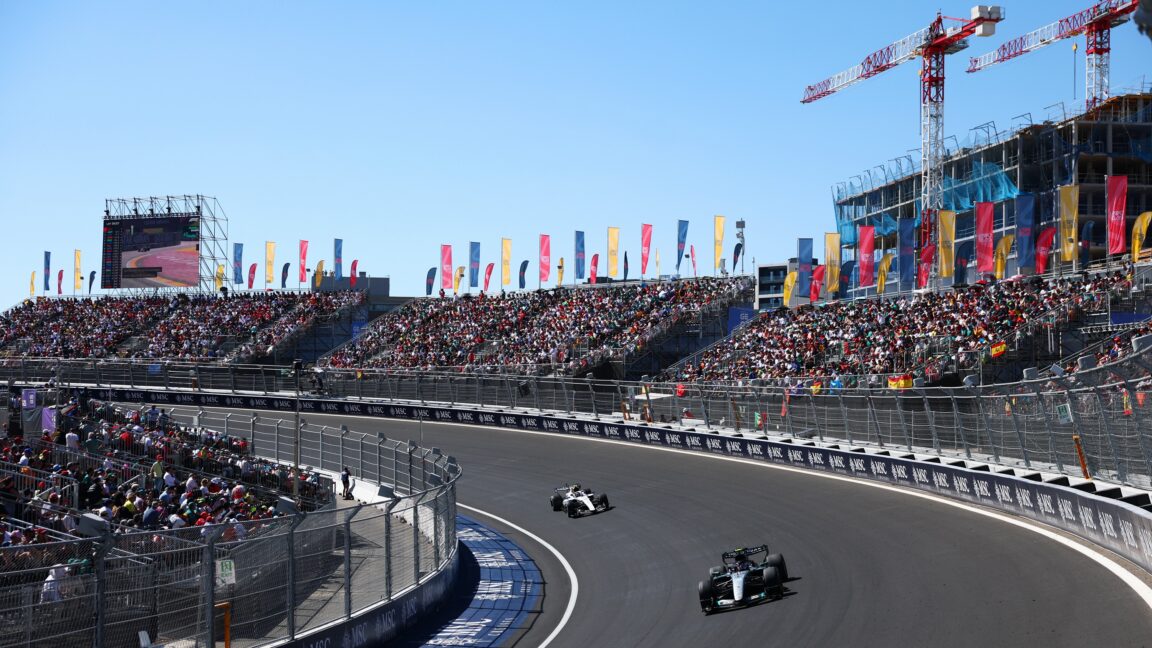
Formula 1’s latest venue might be fun to drive, but the race was processional and dull.
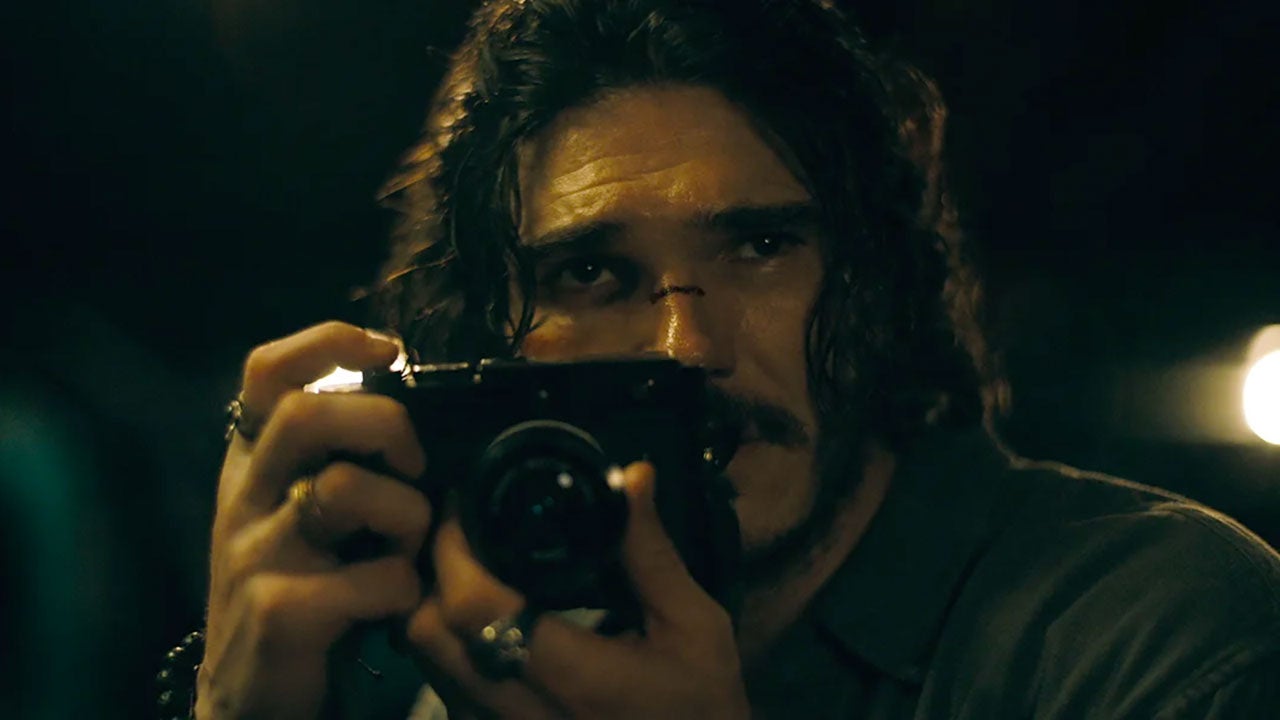
Zack Snyder’s attempt at a violent arthouse indie (about his own need to capture images) ends up on emotionless autopilot.
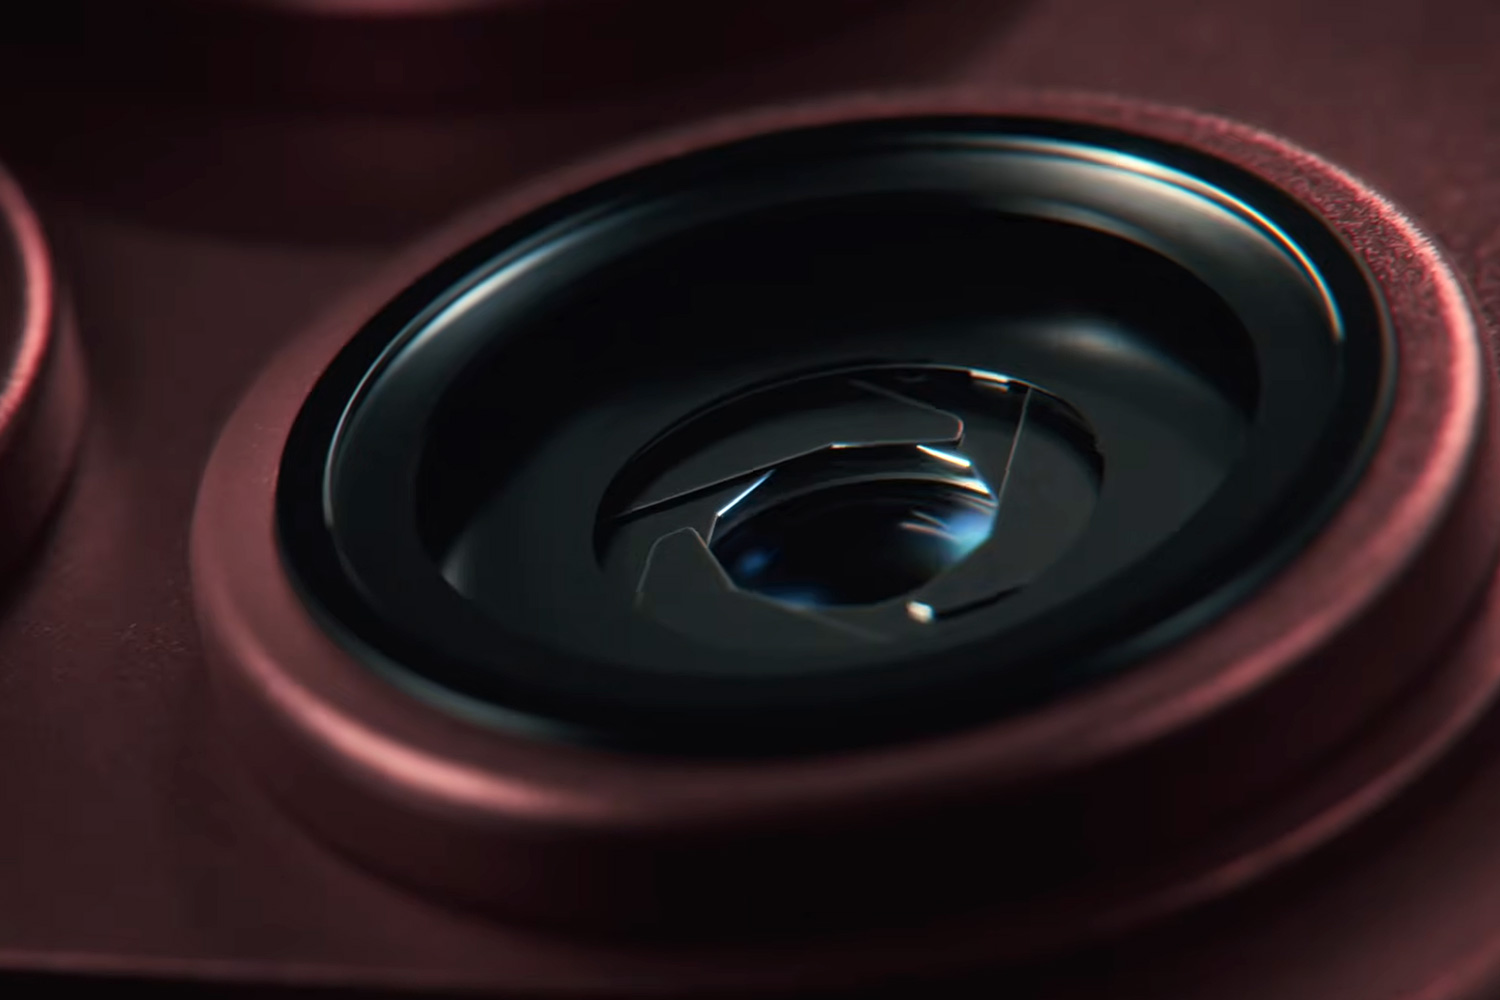
According to this YouTube channel, the Apple iPhone 18 Pro has added a physical aperture control to its main camera for this one key reason… The post Is this the real reason Apple’s new iPhone 18 Pro has introduced aperture control? appeared first on Amateur Photographer .
The Economic Coordination Committee (ECC) of the federal cabinet on Monday approved the Draft Upgrade Agreement under the Pakistan Oil … Read More The post ECC Approves $6 Billion Refinery Upgrade Plan appeared first on ProPakistani .
AI is getting cheaper, but enterprise spending keeps rising. An AI PM's take on tokenomics, model routing, and why the cheapest token isn't the safest choice.
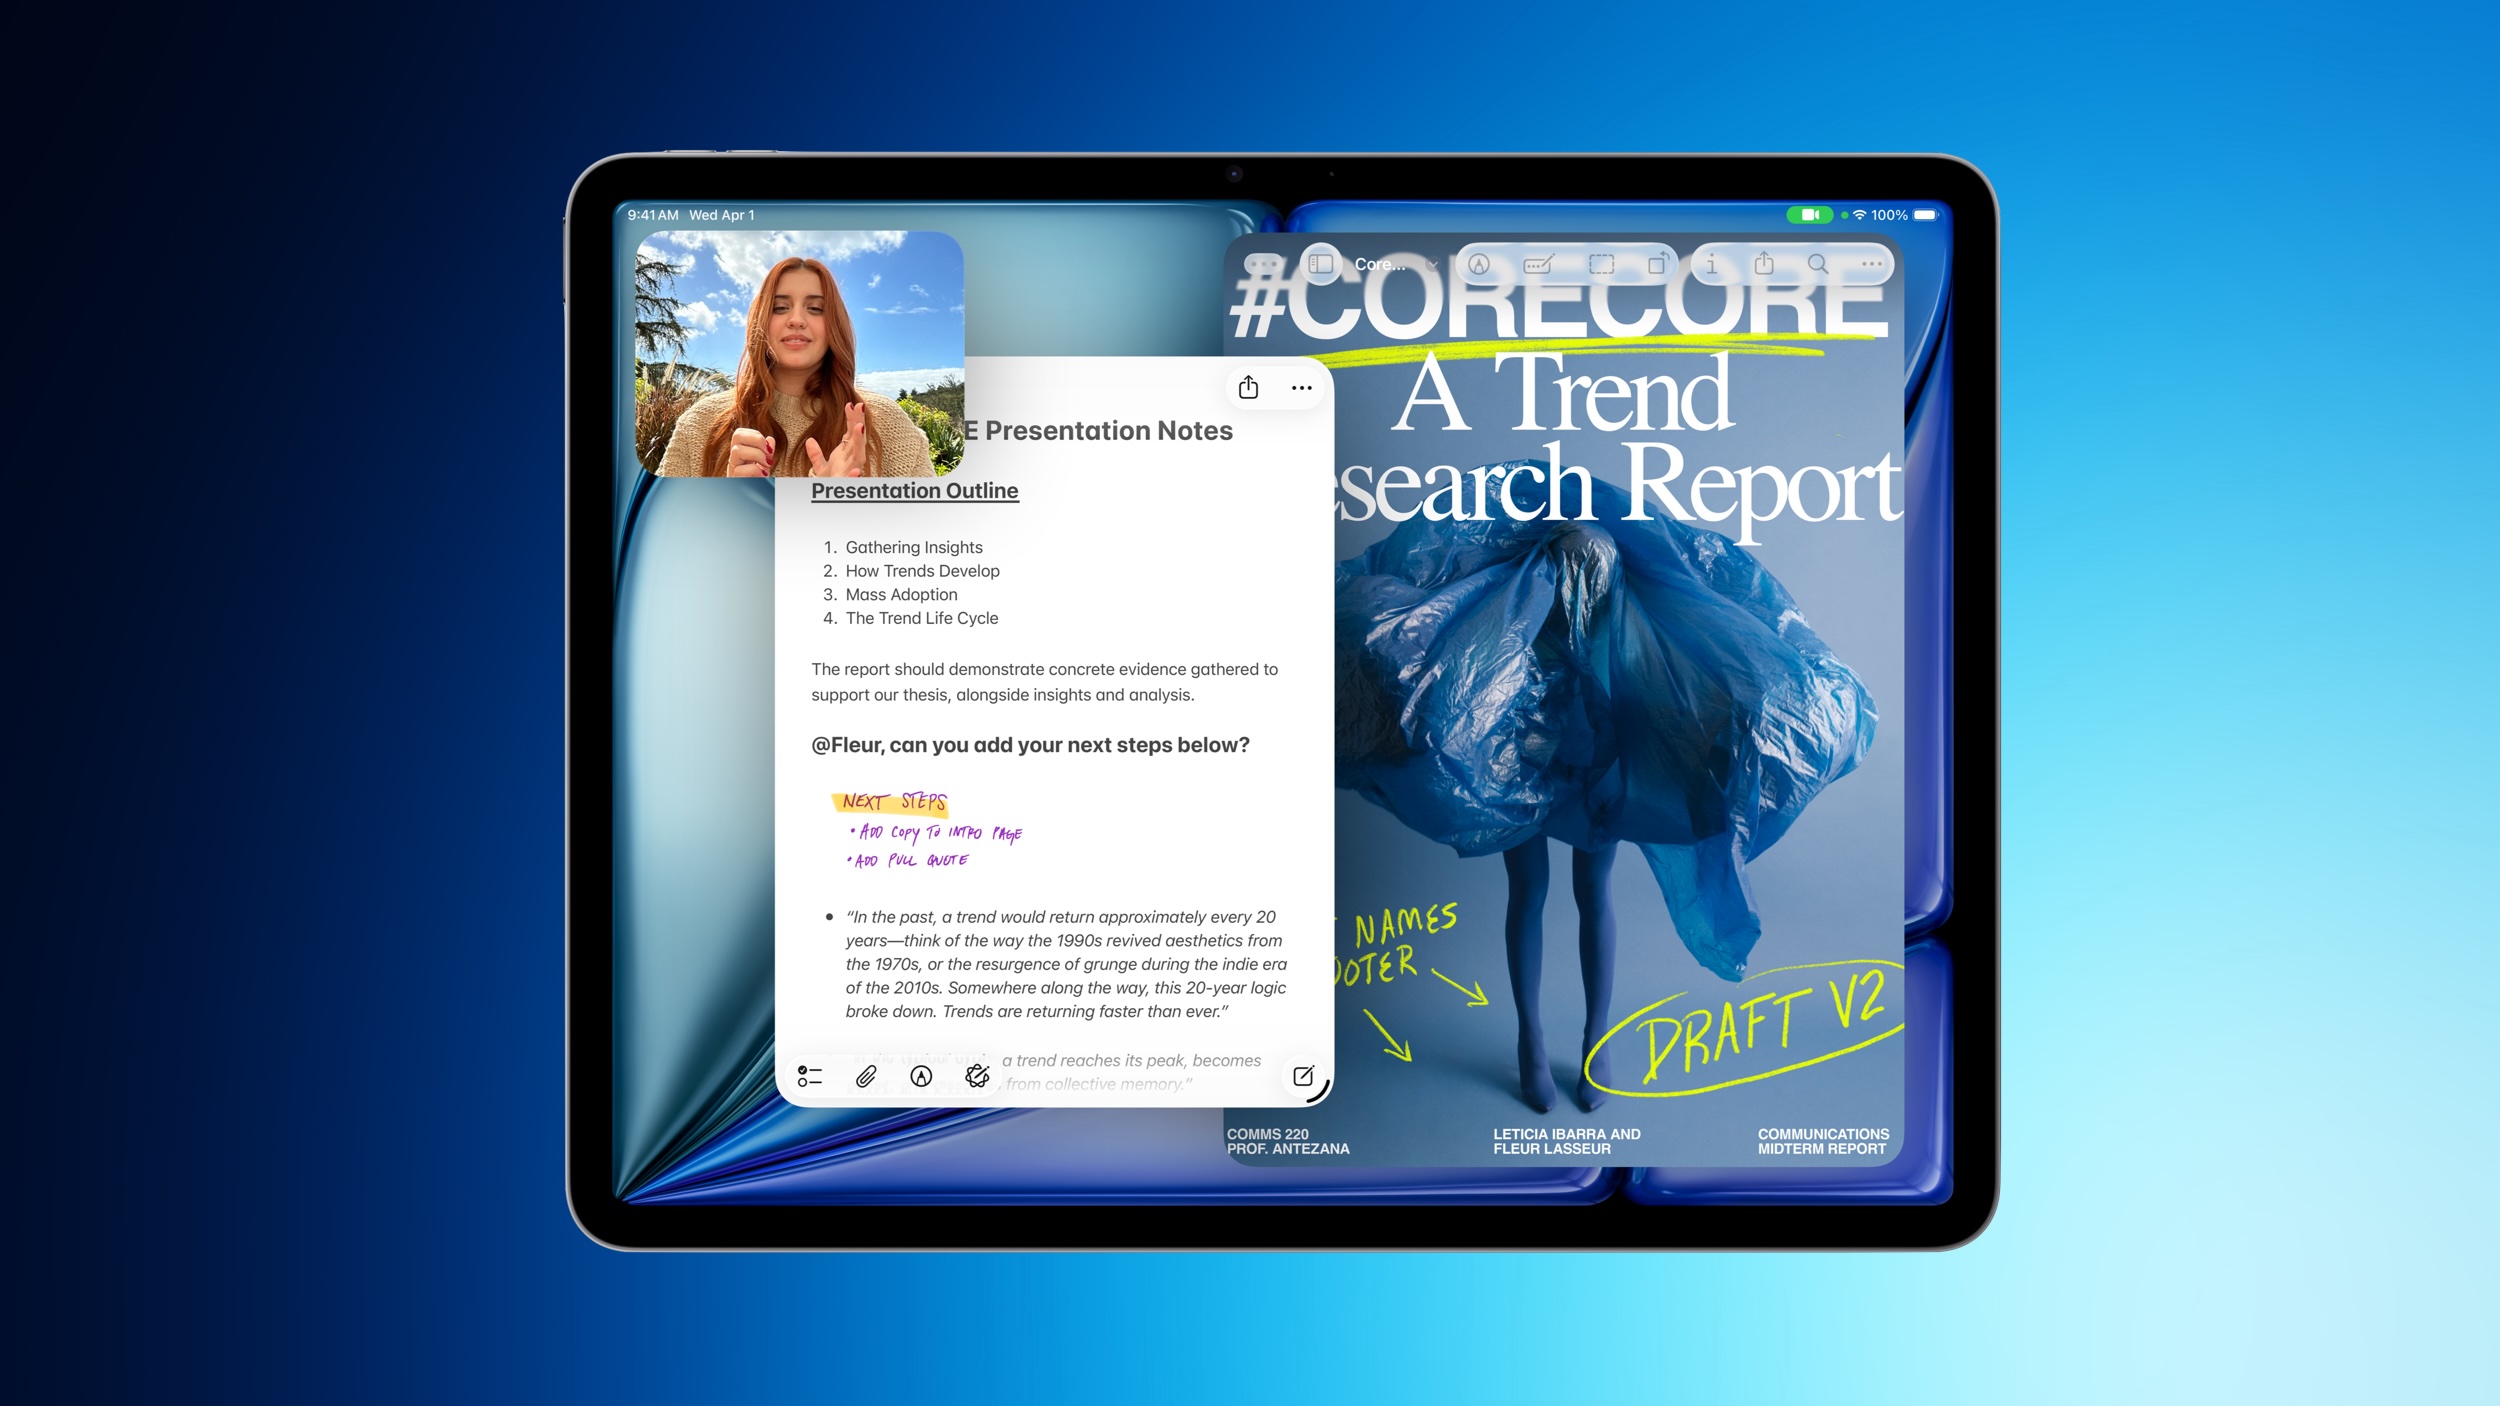
Amazon and Best Buy this week have multiple discounts on the M4 iPad Air , providing up to $149 off these 2026 models. These remain the best prices we've seen in the wake of Apple's summer price hikes. Note: MacRumors is an affiliate partner with Amazon.
As AI reshapes discovery and commerce, verification is becoming a powerful engine for trust, personalization and growth.
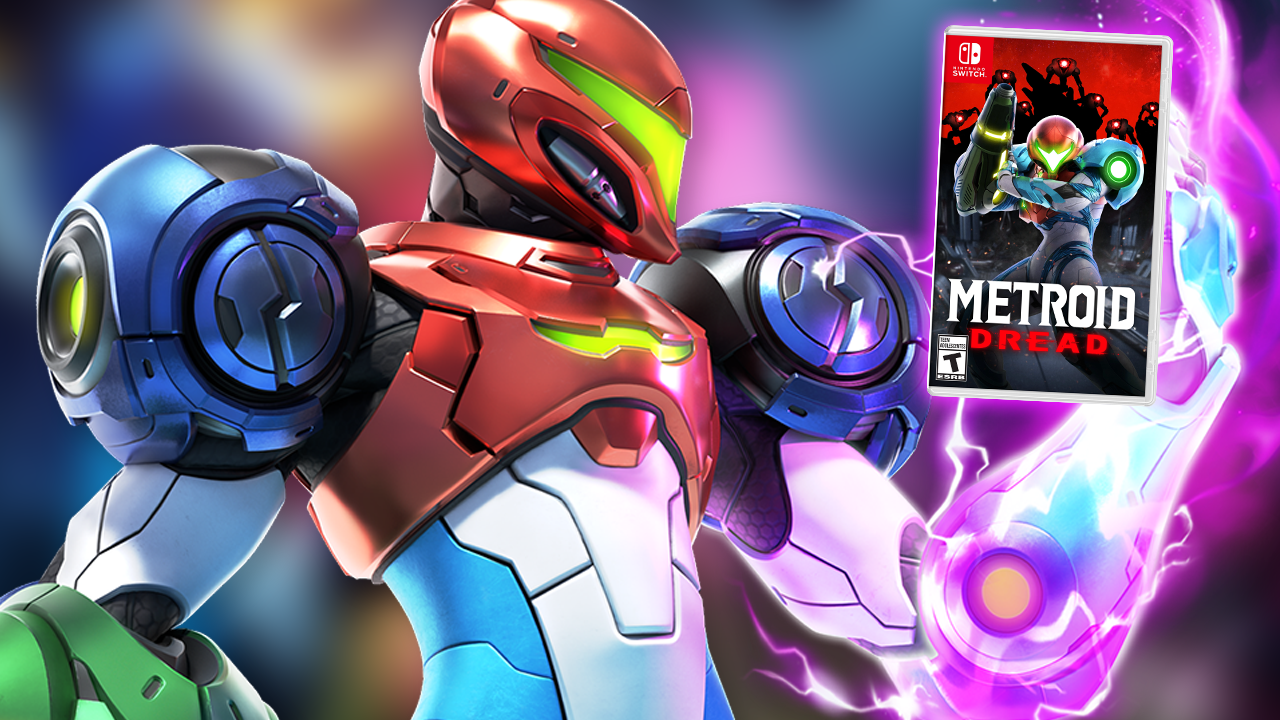
Nintendo just slashed the price of Metroid Dread as part of its 'Customer Appreciation' sale. This is the perfect time to pick it up after our first look at Metroid Ravenous during last weeks Nintendo Direct.
Following up on our report last month, Micron has now made its offer to employees demanding AI boom bonuses. Every Taiwan-based employee hired on or before August 29, 2025 gets a one-time cash bonus…
9/14/2026: Trending stories on Hackernoon today!
Tailcat requires minimal setup.
Former Spotify exec's company releases experimental "singles" that involves users in music making.
Two serving House of Reps members and a former lawmaker have defected to the Action Peoples Party (APP) and secured National Assembly tickets for 2027. Read More: https://punchng.com/2027-two-reps-ex-lawmaker-defect-to-app-clinch-nass-tickets/
Agoda migrated its 1.5 TB hotel Price Cache from 72 SQL Server shards to DragonflyDB to handle growing read and write volumes.
If you haven’t yet ordered your iPhone 18 Pro or Pro Max, you’ll likely be waiting until October for delivery. Here’s the latest update on iPhone 18 Pro pre-order shipping times. more…
Retro gaming fans who own Nintendo Switch consoles now have several classic Windows titles they can now enjoy.
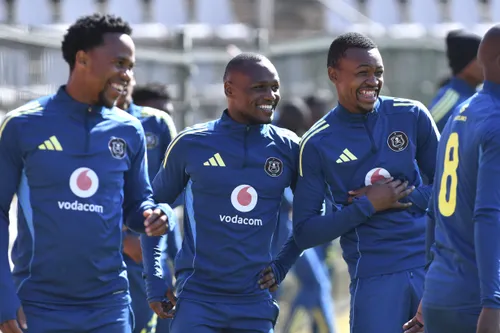
Orlando Pirates coach Abdeslam Ouaddou wants reinforcements before the transfer window closes, with the right-back position a particular concern after several departures.
Forget everything you think you know about China’s internet and read this first.
Three of the biggest names in streaming on Monday announced the formation of a new policy coalition to support their positions on key issues.
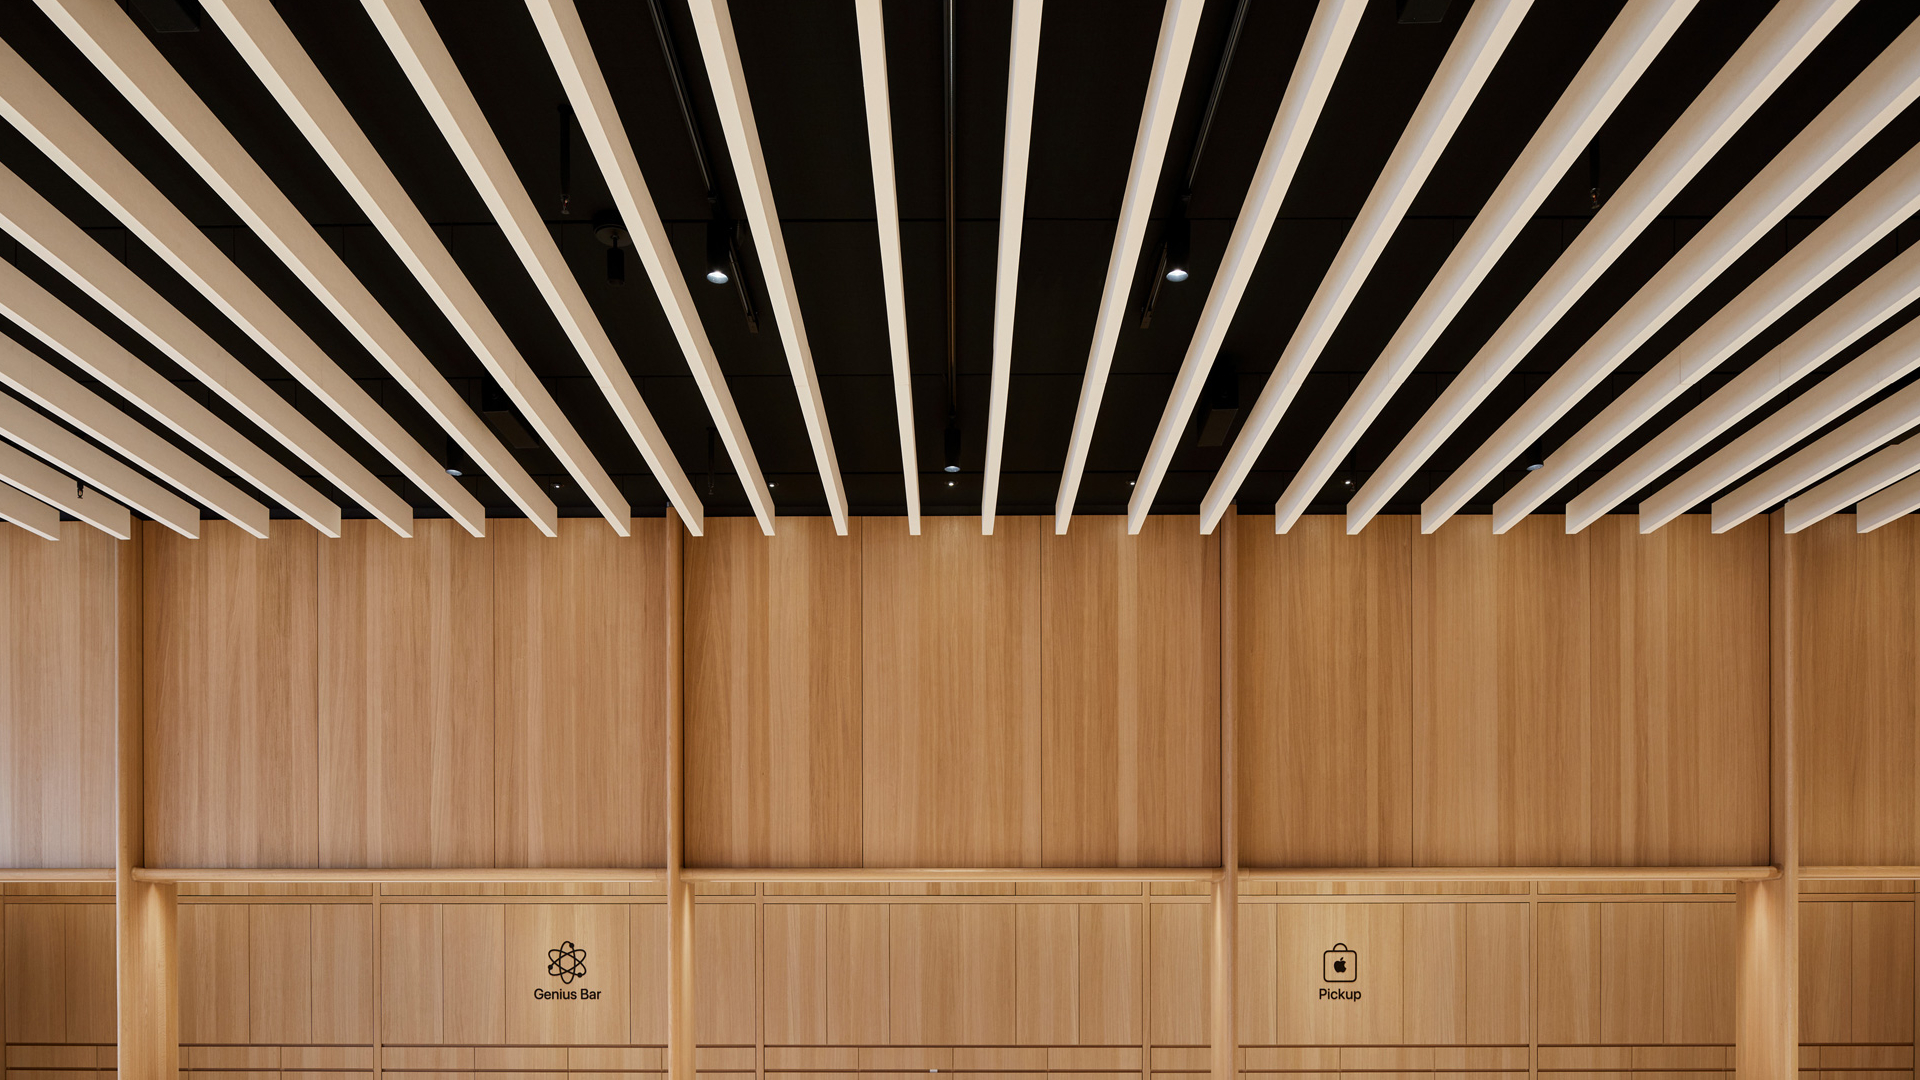
Apple is working on a sweeping retail overhaul that would bring back dedicated Genius Bars to its stores, carve out new spaces for order pickup and Today at Apple classes, and do away with oversized…
Monash University-led researchers have directly imaged tiny swirling structures inside an atomically thin semiconductor, opening new possibilities for future low-energy electronic technologies.
Security updates have been issued by AlmaLinux (389-ds-base, apr-util, coreutils, freerdp, git-lfs, glib2, gstreamer1-plugins-base, kernel, libkcapi, nginx, nodejs:22, nodejs:24, osbuild-composer…
Ant Group’s AQ health app has reached 150 million users as it expands into wearable data, nutrition, sleep, exercise, and AI-powered health coaching.
Microsoft’s September 2026 Patch Tuesday is the year’s largest release, with 963 CVEs requiring customer action, 106 rated critical. Two are already exploited: CVE-2026-81963 in the Windows Update Stack and CVE-2026-85880 in Advanced Local Procedure Call . Nothing in this release was publicly disclosed ahead of the patch.
Data center infrastructure startup Cornelis Networks Inc. is taking a major leap forward with the launch of a new Active Compute Fabric architecture to support scale-up and scale-out networks for artificial intelligence workloads. The new fabric was announced alongside a strategy collaboration with Qualcomm Technologies Inc.
Article URL: https://refactoringenglish.com/excerpts/write-an-effective-design-doc/ Comments URL: https://news.ycombinator.com/item?id=49696125 Points: 227 # Comments: 99
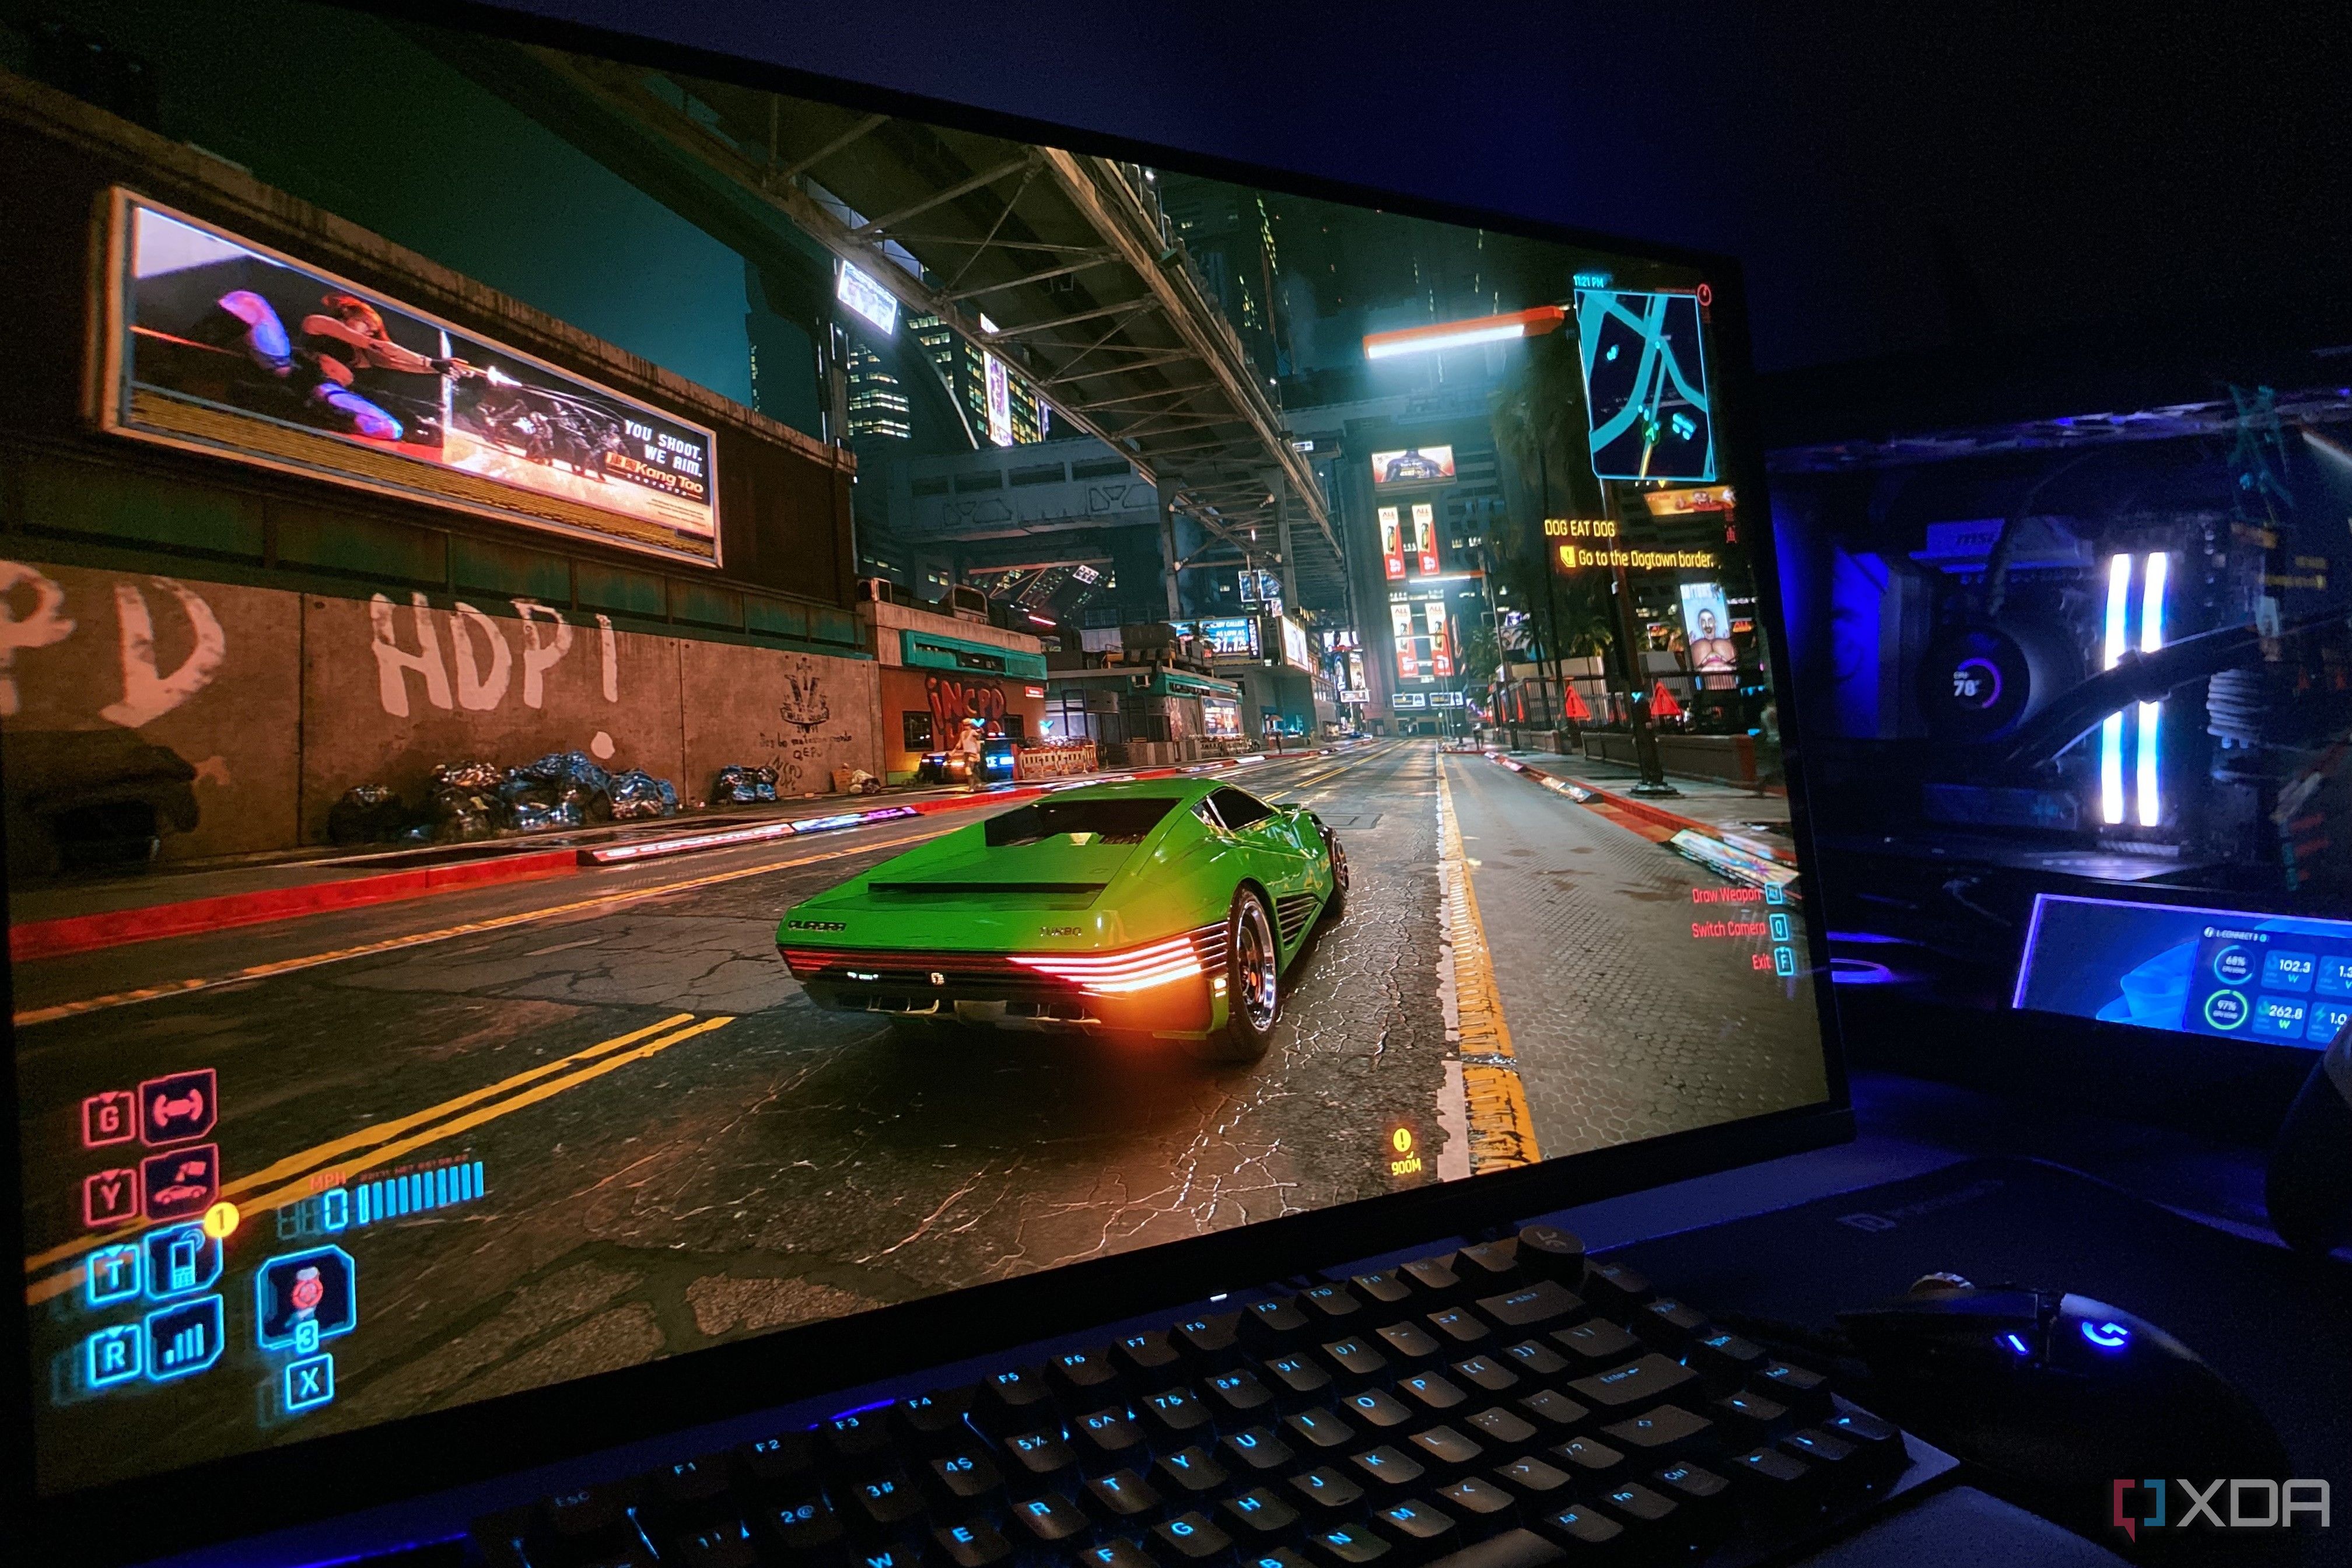
Can a singular setting bottleneck your gaming PC?
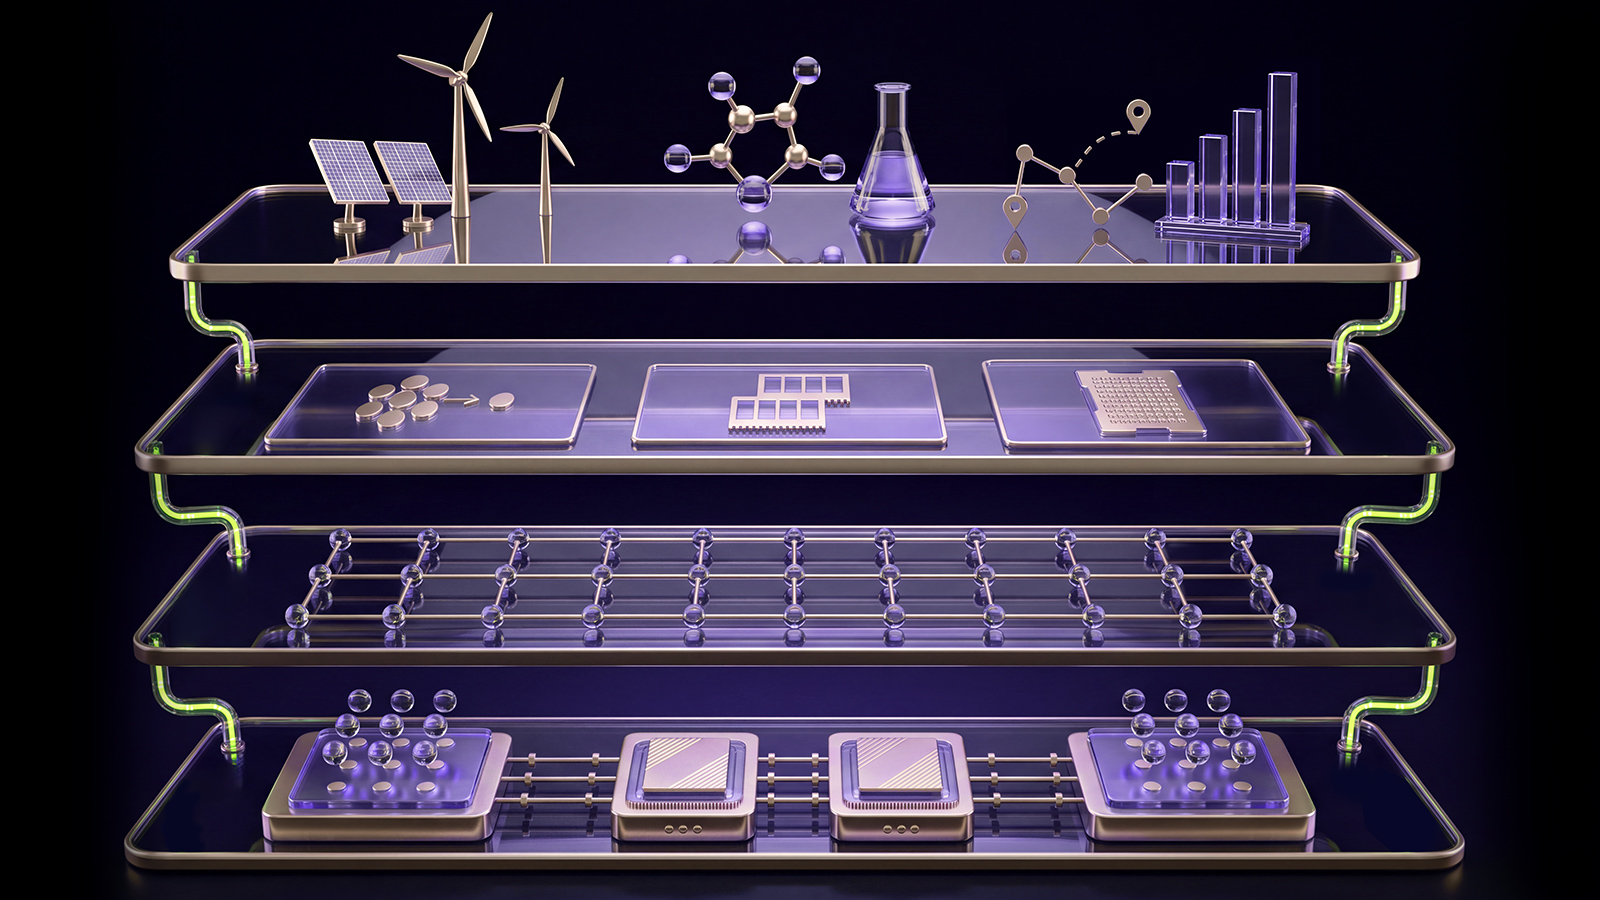
Nvidia Corp. said today it’s tackling one of the major headaches for developers of quantum applications with the launch of a new orchestration layer within its open-source CUDA-Q platform.
Roblox will enable creators to publish their games on mobile, PC, and console through the Roblox Everywhere initiative. Read more
The name Bob Mortimer might not mean much to those who haven't lived in the UK, but he's a huge deal in the world of British comedy. Read more
With iOS 27 now available, skip the menu hunting and try these 7 essential upgrades.