PHP Security Vulnerability: IT Experts Demand Comprehensive Measures Beyond Updates
An update has been installed - and yet hackers could have been in the system for a long time. Security experts recommend checking log data going back to a specific date. Why exactly then?
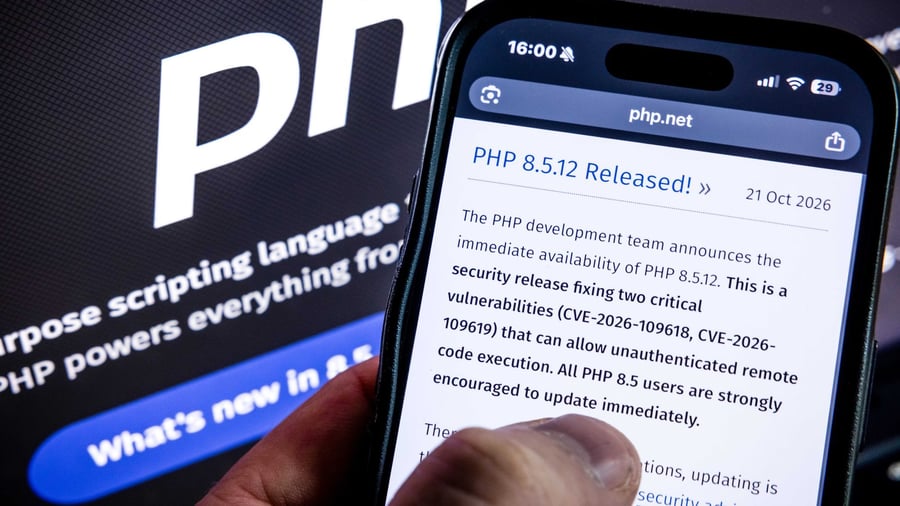
Security experts warn that simply installing software updates to fix a critical PHP vulnerability is not enough. Thomas Boele of Check Point advises system operators to take immediate action, including reviewing log data dating back to October 17, 2026, to detect potential compromises. He also recommends renewing API keys and updating Web Application Firewalls (WAF).
Additionally, experts from KPMG stress the importance of having a complete system inventory and automating security systems to mitigate the risk of the vulnerability, which can be used as an entry point for attacks on internal networks.
Written by urgent.news from Handelsblatt's report — not a translation of it. Machine-written — may contain errors; check the original before relying on it.