PHP-Sicherheitslücke: Experte: Ungeschützte Webseiten abschalten
Eine PHP-Schwachstelle kann Angreifern im Web die vollständige Kontrolle über Server geben. IT-Experten fordern Betreiber zu einem drastischen Schritt auf.
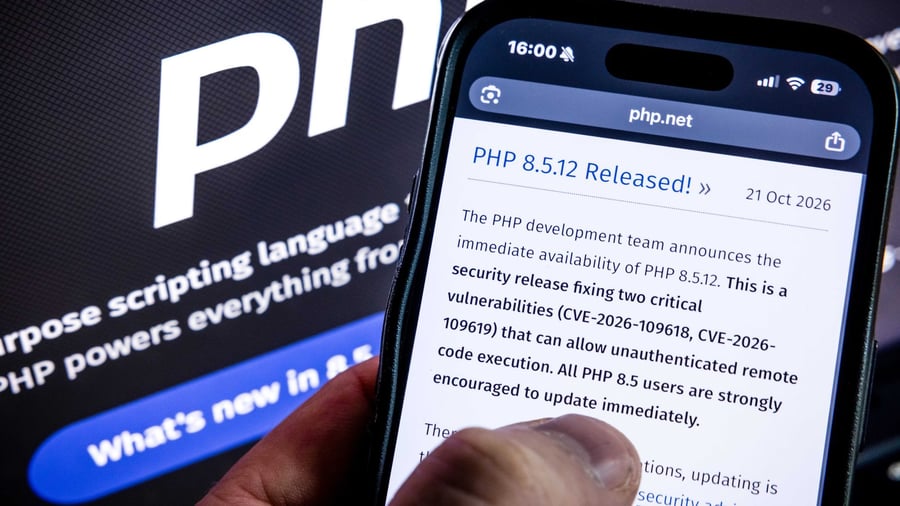
Berlin and Karlsruhe – In the fight against the serious PHP vulnerability, known as the "PHP-Shell", IT security experts are urging the immediate shutdown of unprotected websites, according to Christoph Fischer, an IT security expert based in Karlsruhe. With fears of automated attack waves, Fischer calls on operators to take drastic action, stating that "systems for which no security updates can currently be applied must not remain online under any circumstances."
He warns that "any unprotected PHP application is at this moment an open door for criminals." Fischer also highlights a crucial data protection problem: when a system is compromised by such a weakness, it is often difficult to determine exactly what has happened and what is missing. In accordance with the European General Data Protection Regulation (GDPR), this proof is, however, mandatory for affected organizations.
Fischer demands that all parties involved – from the PHP team to providers, website owners, and authorities – should have ready emergency plans in their files for such IT disasters. The German Federal Office for Information Security (BSI) had previously warned about the grave vulnerability, known as "PHP-Shell," on Wednesday. Public institutions, including state governments, municipalities, authorities, hospitals, universities, as well as private website operators, had preemptively taken their websites offline in response.
It remains to be seen if the broad mass of operators has complied and switched off unprotected systems in the coming hours. Fischer assumes that it will take months to clean up the millions of affected systems.
Written by urgent.news from Handelsblatt's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.