Eiliko robot maker Energize Lab left its entire fleet of 68,000 robots open to a remote takeover
An investigation by The Verge found that researcher Sammy Azdoufal could access 13 million conversations across what appeared to be Energize Lab's entire active fleet of 68,000 Eiliko robots. The US accounted for the largest share of the data, which included more than 31,000 profiles belonging to children. Read Entire Article
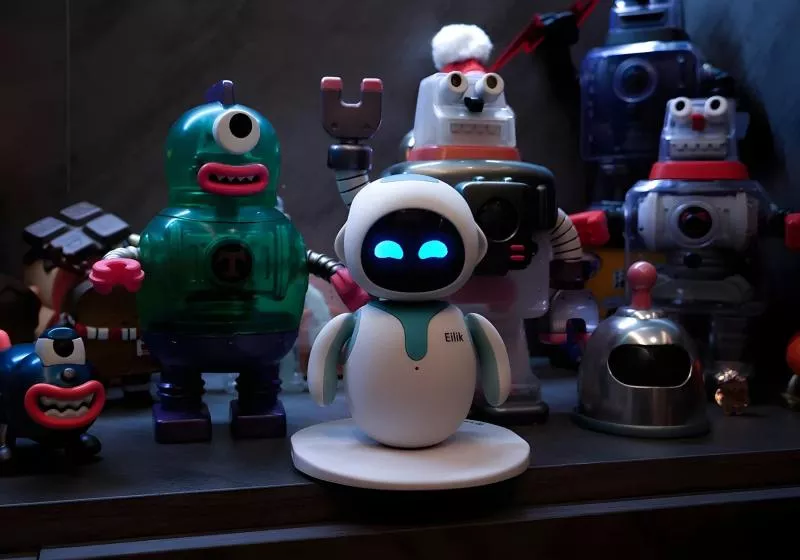
A security researcher discovered that the robot maker Energize Lab left its entire fleet of 68,000 Eiliko robots open to a remote takeover. The researcher, Sammy Azdoufal, accessed millions of private conversations collected by the robots and could alter their responses, access users' personal information, and rewrite the robot's memory.
The researcher found that the service analyzed conversations to build detailed user profiles, recording sensitive information such as names, ages, occupations, relationships, and personality traits. This information was stored alongside email addresses, IP addresses, and a searchable database of conversations. Azdoufal demonstrated that attackers could potentially use this data to manipulate and scam potential victims.
The researcher also found that the robot could store conversations on servers in China and that security weaknesses allowed him to access functions that could alter the robot's behavior. During tests, Azdoufal remotely modified the reporter's Eiliko's memory, changed its responses, and even made the robot deliver sexually explicit commands.
Despite some safeguards, such as warnings against dangerous actions, these protections were insufficient to prevent further manipulation. Additionally, the service stored photographs of children and audio recordings in publicly accessible web addresses, contradicting Energize Lab's privacy policy. The researcher found that many of the company's administrator passwords were common and easily guessable.
Despite multiple attempts to contact Energize Lab, the company did not provide any substantive answers or take any meaningful action to address the exposed records or the researcher's claims.
Written by urgent.news from TechSpot's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.