Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts
Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to build artificial intelligence (AI) applications and agentic workflows. In February 2025, DataStax, the parent company of Langflow, was acquired by IBM. The vulnerability in question is CVE-2026-105740 (CVSS score: 9.9), a case of
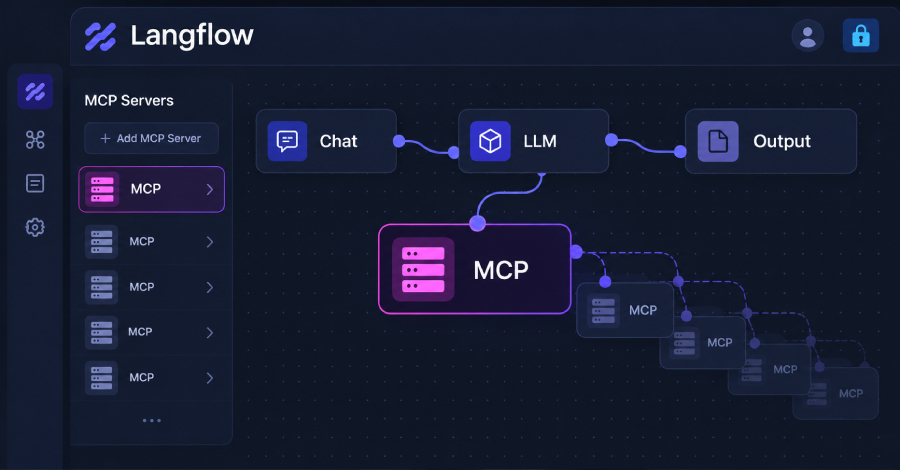
An authenticated remote code execution (RCE) flaw in the open-source AI platform Langflow has become a target for threat actors, according to security firm Previdian. The vulnerability, CVE-2026-105740 with a CVSS score of 9.9, impacts Langflow versions prior to 1.9.0. Any authenticated user can exploit the flaw to execute arbitrary operating system commands on the server with the privileges of the Langflow process.
Unlike custom component code, malicious MCP server configurations are stored in project settings, making them less visible during normal flow review. Previdian reports 1,423 exploitation attempts against its honeypot sensors since September 19, 2026, originating from 27 unique IP addresses across several countries. The majority of attempts involve brute-force attacks and exploiting other Langflow vulnerabilities.
Experts recommend upgrading to a patched version, disabling auto-login, using strong unique passwords, and monitoring authentication logs for suspicious activity.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.