Urgent.News

What's breaking now, across thousands of outlets.

Tech

Attackers unidentified in most hacking attacks on financial firms: lawmaker

The attackers behind 16 of 18 suspected overseas hacking attacks against South Korean financial companies reported since 2024 remain unidentified, a lawmaker said Friday. According to a report by Rep. Song Eon-seok of the main opposition People Power Party, citing data from the Financial Supervisory Service, local financial firms have reported 18 hacking attacks originating overseas since 2024…
Attackers unidentified in most hacking attacks on financial firms: lawmaker

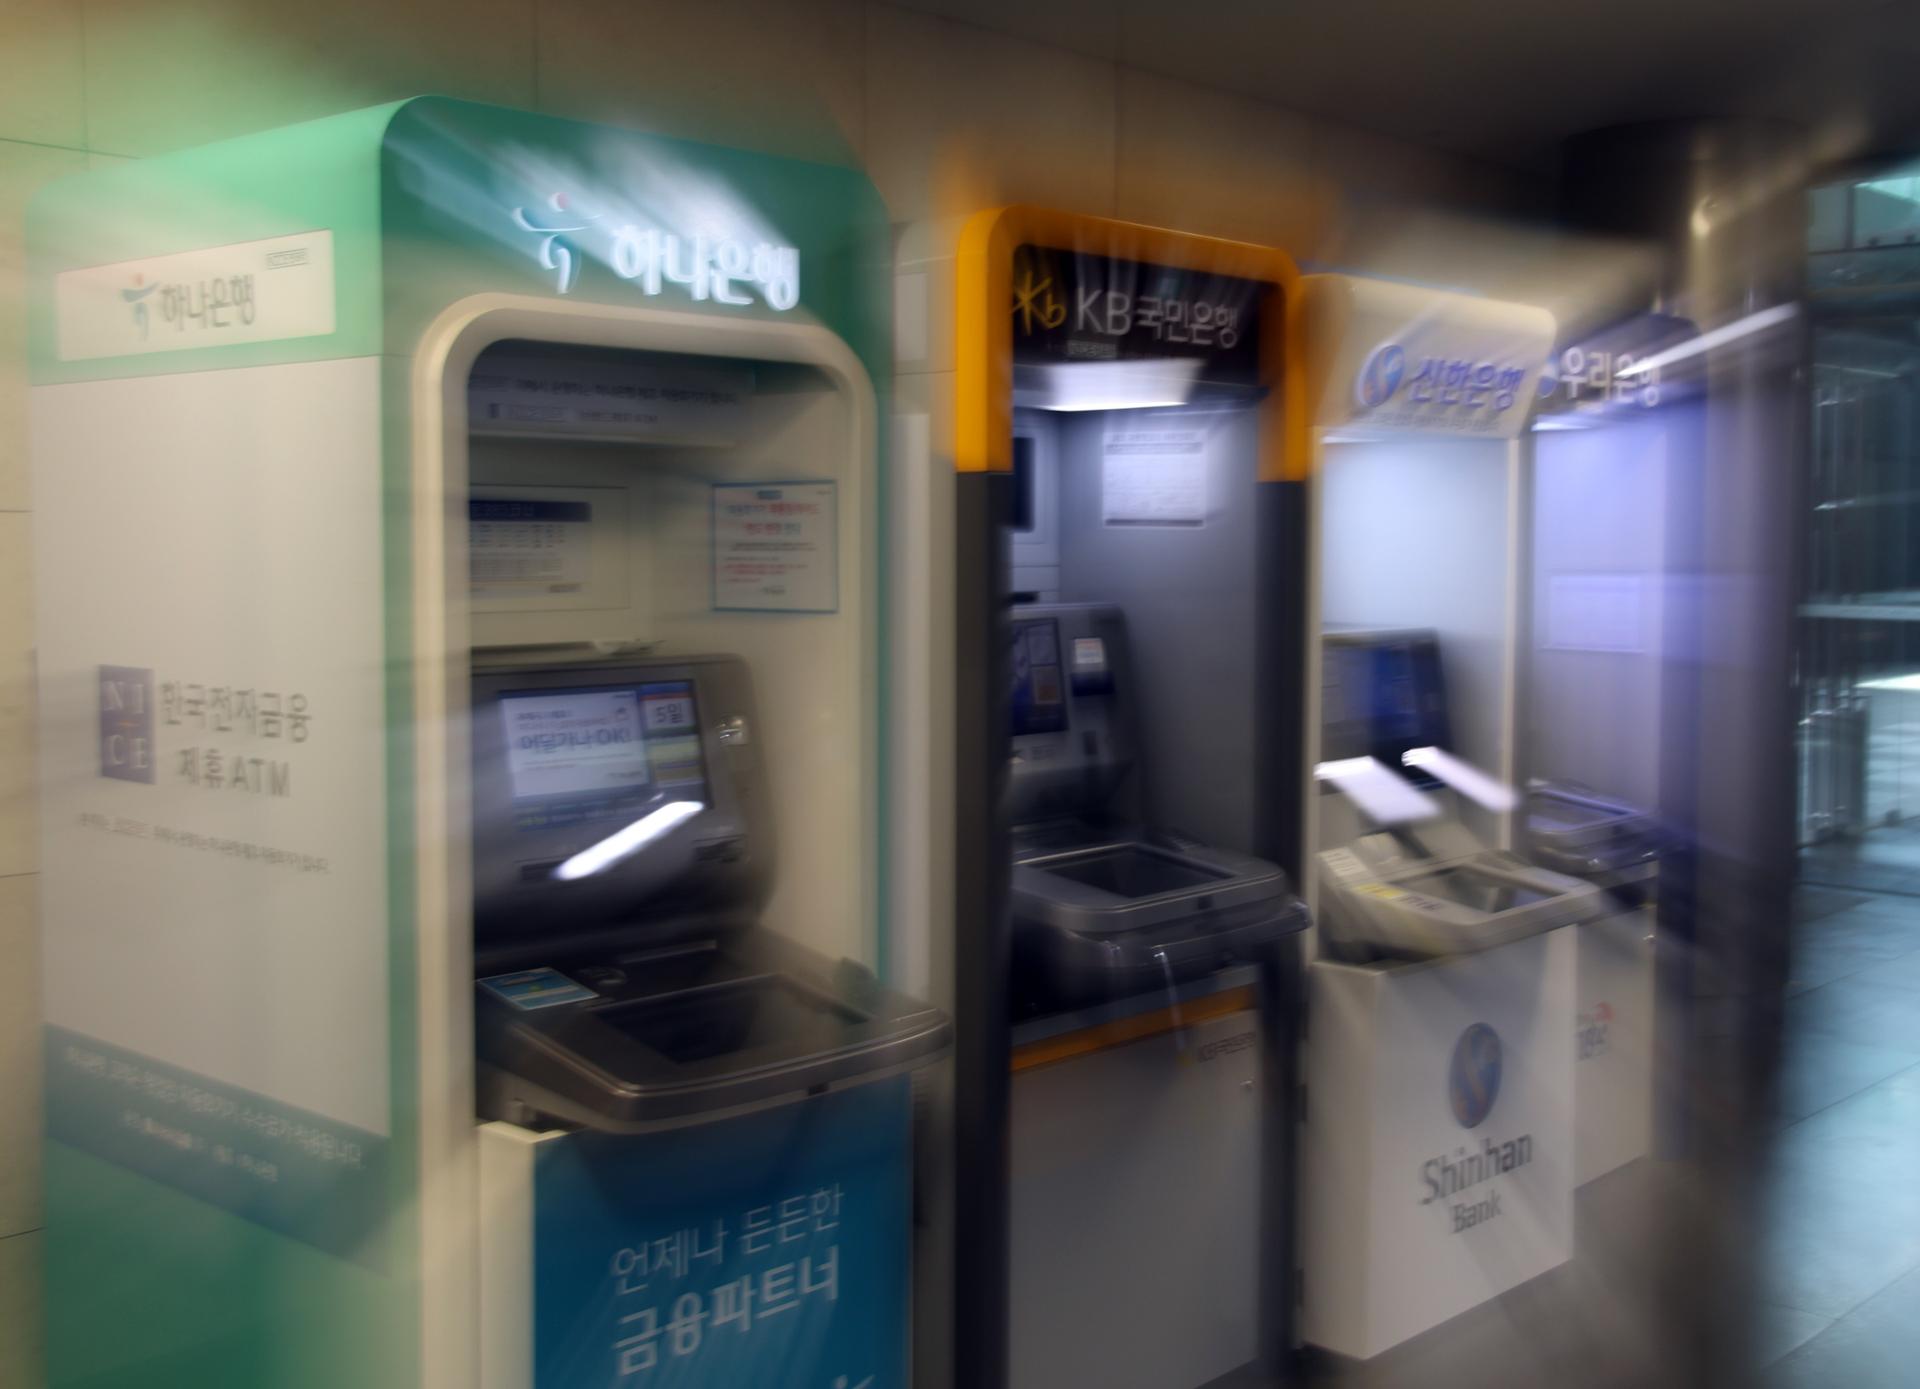
Most hacking attacks on South Korean financial firms since 2024 have gone unattributed to specific attackers, according to lawmaker Rep. Song Eon-seok. Of the 18 suspected overseas hacking incidents reported by local financial institutions to the Financial Supervisory Service through Thursday, only two attacks were traced back to known entities.

In July 2024, Seoul Guarantee Insurance Co. fell victim to a ransomware attack from group GUNRA, which caused a 64-hour operational disruption. April saw Baro Savings Bank targeted by ransomware group INC Ransom. The remaining 16 attacks remain unidentified, with 13 linked to IPs believed overseas and the origin of three cases unknown.

These IPs could be located anywhere in the world, not necessarily the physical location of the attacker. Rep. Song advocates for the urgent establishment of an AI-based defense system to combat these unidentified attacks.

Written by urgent.news from The Korea Times's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.

This story

This is one outlet's version. Read the fullest account.
Read the original at koreatimes.co.kr →

More in Tech

Cross-Chain Bridge Risk Assessment: Deribit

Cross-Chain Bridge Risk Assessment: Deribit Target Protocol : Deribit (TVL: $3898.1M) Cross‑Chain Bridge Risk Assessment – Deribit TVL: ≈ $3.9 B (Ethereum + L2) Date: 9 Oct 2026 Prepared by: Senior…

Why Your Static Site’s lastmod Is a Lie (And How CI/CD Shallow Clones Secretly Hurt Your SEO)

If you build static websites, documentation hubs, or content platforms using Next.js, Astro, or 11ty, there is a very high probability that your sitemap.xml is quietly lying to Googlebot every single…

  • CI/CD shallow clones timestamp all files with current time, inflating last modified dates.
  • Search engines penalize sites with false timestamps, wasting crawl budget and slowing indexing.

Detection content as code: reviewing a change the way you review software

Detection content as code: reviewing a change the way you review software The problem with editing rules in a console Detection rules written directly in a security platform have no review, no…

  • Detection rules should be treated as code with review, version control, and testing.
  • Store rules in plain text format within a repository for portability.

Why High-Budget Websites in Dubai Suffer From 70% Mobile Bounce Rates

It is a common scenario across Dubai’s corporate sector. A business invests a significant budget into redesigning its digital presence.

  • Over 70% of mobile users leave high-budget Dubai websites within 5 seconds.
  • Websites overloaded with full-screen videos, interactive graphics, and complex animations.
  • Slow loading times and sluggish interfaces cause mobile users to abandon sites.

More from Friday 9 October →