Urgent.News

What's breaking now, across thousands of outlets.

Tech

Watchdog unveils guidelines on deceptive 'dark patterns' on online platforms

Korea's fair trade watchdog on Tuesday released guidelines for online platforms to avoid "dark patterns," or deceptive practices designed to make it difficult for users to cancel subscriptions or induce them to make irrational purchases. The Fair Trade Commission (FTC) said the latest guidelines consolidate and update existing guidance and provide detailed examples of violations to help platform…
Watchdog unveils guidelines on deceptive 'dark patterns' on online platforms

On Tuesday, Korea's fair trade watchdog unveiled guidelines aimed at preventing online platforms from employing deceptive practices known as "dark patterns." These practices are designed to complicate the cancellation of subscriptions or encourage irrational purchases from users. The Fair Trade Commission (FTC) stated that these guidelines consolidate and update previous guidance, offering detailed examples of violations to assist platform operators in adhering to the rules.

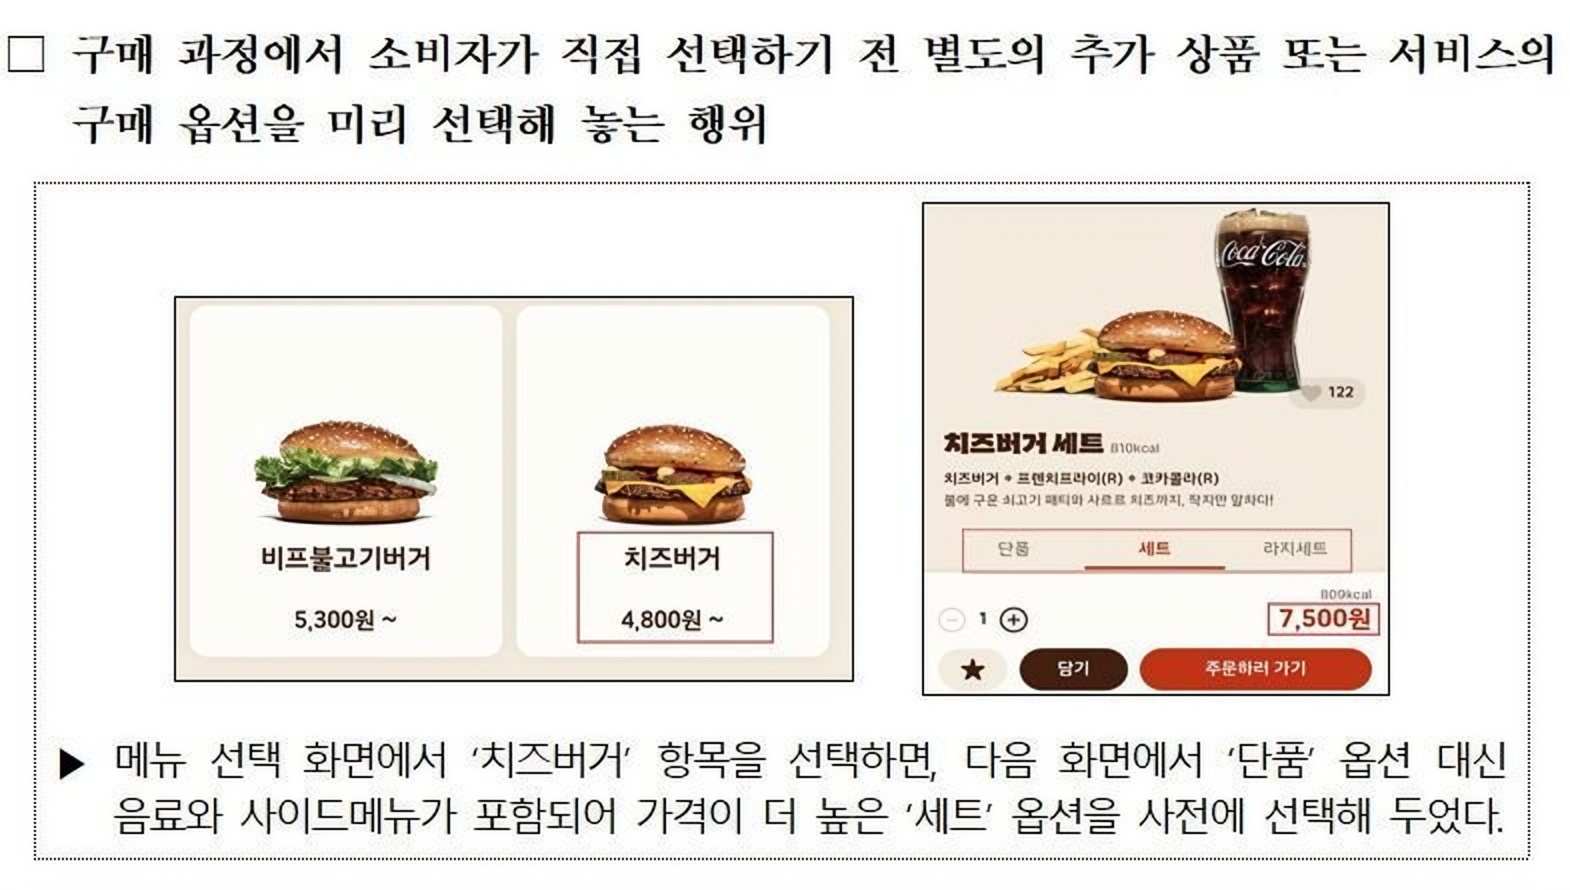
Dark patterns involve tactics that deceive consumers into making payments or signing up for services without a full understanding of their commitments. Examples include enrolling users in monthly subscription services without explicit consent or making the cancellation process unnecessarily complex. According to the guidelines, platform operators should ensure cancellation links are easily accessible, such as on the website's homepage or within the "My Account" section, rather than in less intuitive locations like "Security Settings."

The FTC advised platform operators against automatically adding options that users have not explicitly selected during the signup process.

Written by urgent.news from The Korea Times's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.

This story

This is one outlet's version. Read the fullest account.
Read the original at koreatimes.co.kr →

More in Tech

My refund handler checked the ledger before paying. It still paid twice.

A refund handler commits the refund, then loses its reply. Maybe the HTTP response timed out. Maybe the worker died before it acknowledged the queue message.

  • Refund handlers check ledger before payment but still pay twice due to various reasons.
  • Four handlers tested: naive always pays twice, others pay correctly once in 200 trials.

Traefik or Caddy? Choose a Reverse Proxy by How You Deploy

Adding a service behind a reverse proxy should be routine. But the workflow changes depending on whether routes live in one proxy config or are discovered from your containers.

  • Caddy is simpler for small, stable site configurations
  • Traefik suits frequently changing Docker services
  • Routing defined differently: Caddy explicitly, Traefik via metadata labels

Filter tcpdump by IP: Hosts, Direction, Subnets, and Ports

When a packet capture is full of traffic you don't care about, narrow it with a capture filter . For an IP address, the key distinction is whether you want traffic in both directions, only packets…

  • Use host keyword to filter by IP address in tcpdump
  • Apply net keyword with CIDR notation for subnet filtering
  • Combine host and tcp port numbers for port-based filtering

Node.js Feature Flag Rollouts: Stable Bucketing for 10% Notification Releases

Short answer: store the rollout percentage in the flag system, but make the release decision in the request path with a deterministic hash of an immutable user or account ID.

  • Store rollout percentage in flag system, decide release in request path
  • Use deterministic hash of immutable ID for consistent tenant delivery
  • Implement Go-based SHA-256 hashing to create 10,000 stable buckets

HyperShift CVE-2026-101919 — CVSS 8.8 Tenant Isolation Bypass via Kubeconfig Passthrough

An authenticated tenant with basic namespace permissions can break out to the host control plane in OpenShift clusters running Multicluster Engine with HyperShift.

  • OpenShift clusters with Multicluster Engine and HyperShift vulnerable to tenant isolation bypass.
  • CVE-2026-101919 rated CVSS 3.1 8.8 by Red Hat as Important.
  • Patch available; restrict Secret creation, deploy admission webhook, audit kubeconfig Secrets.

More from Tuesday 6 October →