Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records
A security breach at Gyazo, Helpfeel's image-sharing service, exposed about 23.62 million user records, including email addresses and password hashes, the Kyoto-based company said in a notice published Wednesday. It also exposed about 490 million image metadata records, mostly for images from January 2019 or earlier, including the IDs that make up Gyazo image links. Helpfeel said
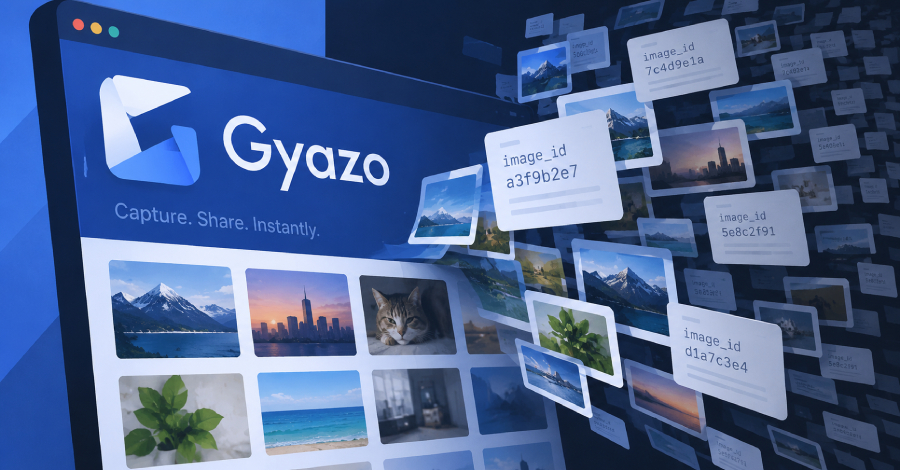
The Helpfeel company, a Japanese support and knowledge-base platform with more than 200 employees, experienced a cybersecurity breach on September 11. The attack exposed 23.62 million user records, potentially compromising personal identifiable information (PII) and private images. The stolen data includes names, emails, password hashes, device IDs, login session IDs, Google Single Sign-On tokens, profile information, language preferences, registration and login dates, subscription plans, and usage statistics.
Payment information, including credit card numbers, remained secure during the incident. However, the attackers gained access to 490 million image metadata records, including image IDs, source IP addresses, user agents, EXIF location data, OCR text, image titles, source URLs, and hashed passphrases. Helpfeel temporarily disabled image viewing to prevent potential harm and is continuing its investigation to determine the extent of the damage caused by the breach.
Written by urgent.news from TechRadar's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.