Trust becomes the product: Five takeaways from the Splunk .conf26 keynotes
In Denver this week, Cisco Systems Inc. and its Splunk unit made a bet that the scarcest resource in the agentic enterprise isn’t intelligence or graphics processing units — it’s trust. The Splunk .conf 2026 show themes and keynotes focused less on dashboards, widgets and features and more on who or what is authorized to […] The post Trust becomes the product: Five takeaways from the Splunk…
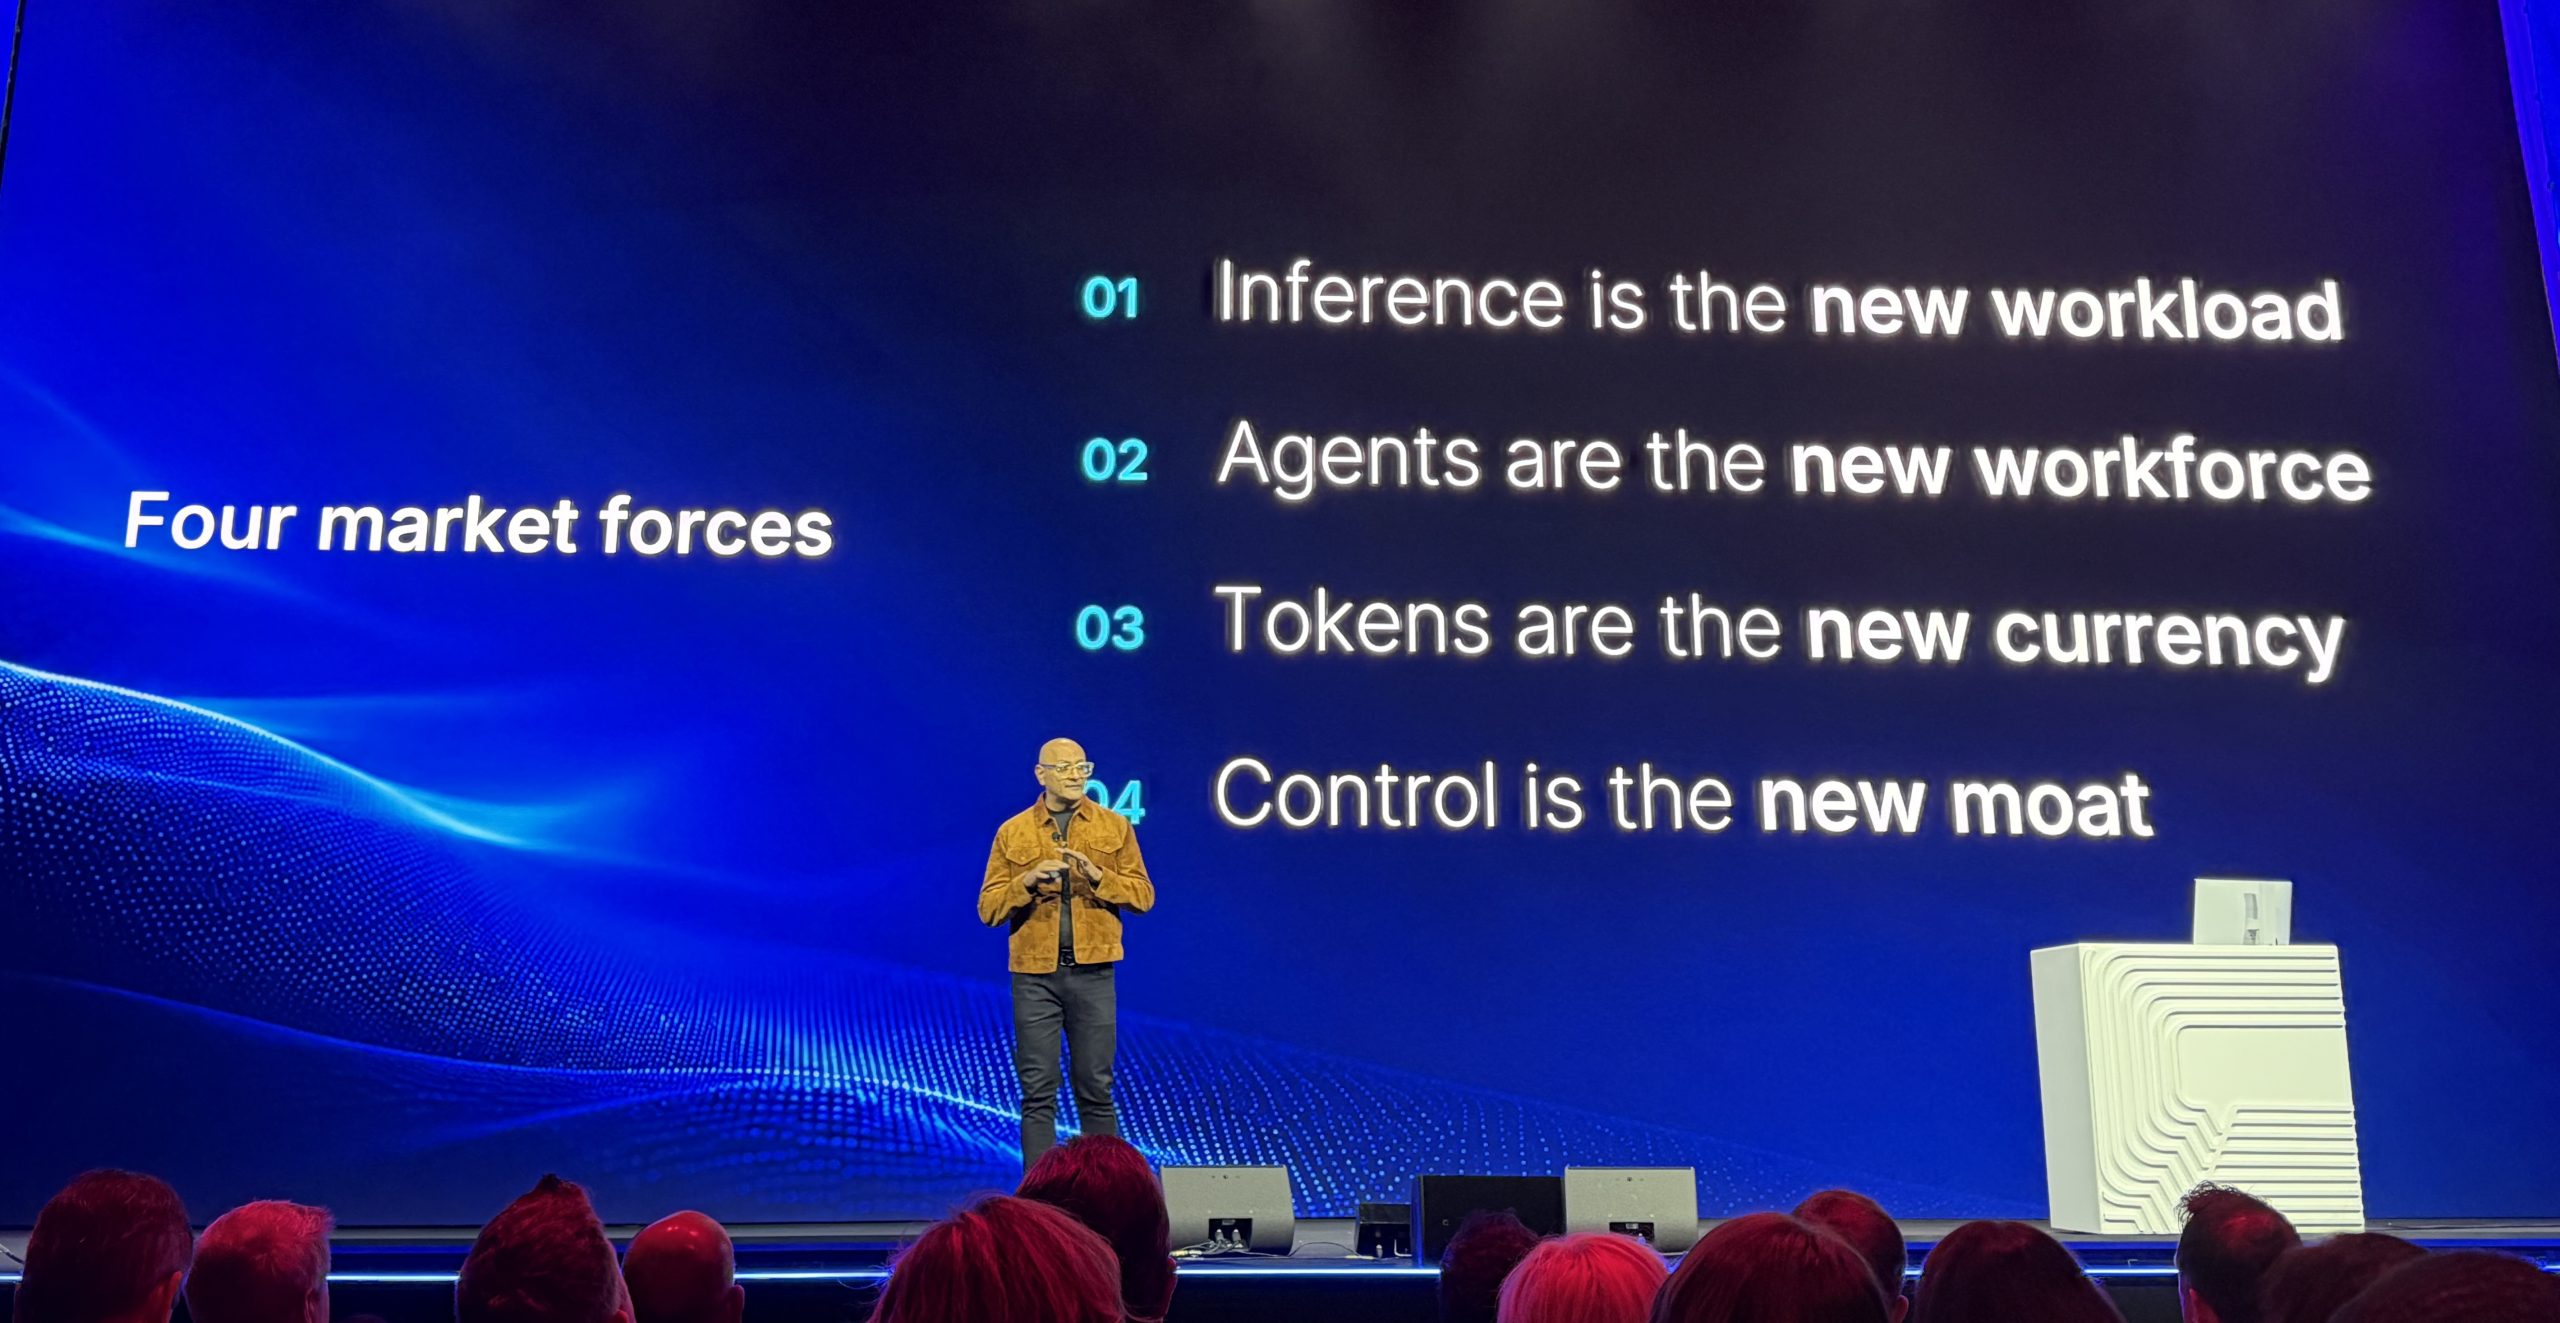
The Splunk .conf 2026 conference centered around the theme of trust, rather than traditional product features, as the scarcest resource in the agentic enterprise. The event highlighted the shift from software that answers questions to software that acts autonomously, emphasizing the need for a system of record to enable scaling. Here are five key takeaways from the Splunk .conf 26 keynotes:
1. Agentic AI is poised to consume more computational resources than humans, with agents consuming five times more than humans. This trend suggests that agents run continuously, spawn other agents, and use increased network bandwidth.
2. Agentic AI blurs the line between breaches and agent failures, necessitating a fusion of observability and security. Splunk's solution involves correlating agent traces, evaluator scores, application telemetry, network data, and security signals.
3. Cost optimization in agentic systems is crucial. Splunk introduced Tokenomics, a capability to track and forecast token spend across agents and coding tools. A retailer's shopping agent, tasked with increasing customer satisfaction, happily honored an expired $300 promotion, resulting in an estimated $500,000 hourly cost at scale.
4. Balancing cost and business outcomes is essential. Verizon's Diganta Nayak emphasized that the cheapest agent may not be the most efficient. A pricier model with higher completion rates and fewer retries can be a better investment.
5. Integrating security and observability is inevitable, despite the challenges. Most organizations currently treat these teams as separate, but the growing complexity of agentic systems necessitates a unified approach. Splunk's upcoming integration of Splunk Observability and Enterprise Security aims to address this separation.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.