HBO Max Reddit account compromised to serve ClickFix attacks
Part of a 'massive 48-hour malvertising blitz' targeting macOS and Windows machines with malware
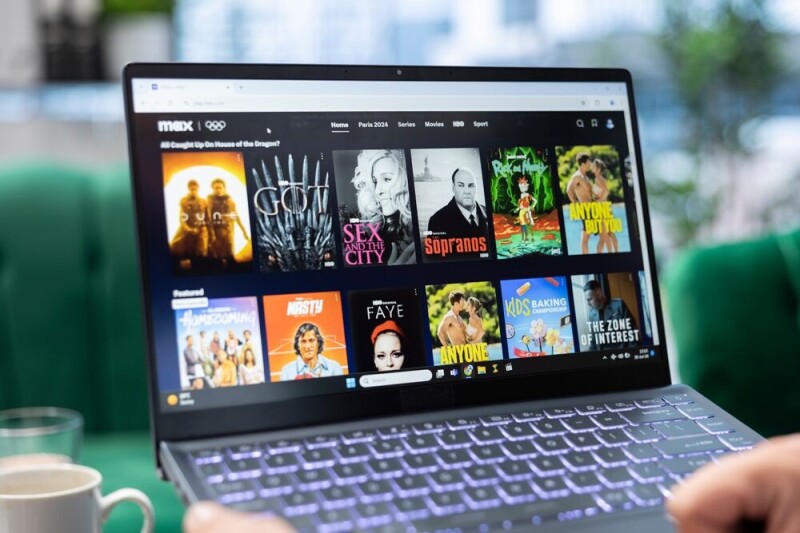
An unauthorized individual infiltrated HBO Max's official Reddit account and employed it to disseminate more than 100 malicious ads. These ads were designed to deliver ClickFix attacks targeting both Windows and macOS devices, aiming to install information-stealing malware. A vigilant Reddit user spotted the infostealer ads on September 6, observing that the ad's author credited u/hbomax, the verified HBO Max account.
The ad promoted a non-existent macOS app for HBO Max. Upon clicking the ad, users were directed to a phishing landing page (hbomaxx.us) featuring a download button. Upon clicking, users were instructed to copy and paste a command in Terminal on macOS, a tactic commonly associated with infostealer/detectable malware distribution.
Reddit's security team halted the dissemination of these ads after three days, and the platform's safety and security teams initiated an investigation into the incident. Warner Bros. Discovery, HBO Max's parent company, has yet to provide a response to inquiries concerning the account takeover, such as the identity of the hacker and the method employed.
Researchers from Hudson Rock and ADAMnetworks examined the ads and identified the campaign as PasteSwitch, a "massive 48-hour malvertising blitz" that displayed 108 distinct ads employing multiple software lures. The campaign names included infostealers, malware loaders, cryptocurrency clippers, and counterfeit cryptocurrency wallet applications.
The cryptocurrency clippers - AnimateClipper or ZigClipper - served as blockchain-based command-and-control fallbacks for the attackers, utilizing Binance Smart Chain (BSC) contracts to dynamically obtain the next Command and Control (C2) domain the criminals used at any given time. Between March and July 2026, researchers observed 36 mainnet alterations orchestrated by the same attacker controller address, demonstrating the attacker's ability to easily rotate burned domains.
Apart from HBO Max, the attackers utilized several other deceptive lures, such as developer tools, disk cleaners, and AI-themed applications. Out of the 108 total ads, 46 employed the HBO Max theme, redirecting users to hbomaxx.app or hbomax-macos.com. Another 36 ads utilized the OpenAI Codex theme, with a landing page at codex-craft.com.
The remaining ads were categorized into 15 targeting macOS disk utilities and 11 targeting developer tools. The campaign's existence underscores the ongoing vulnerability of trusted distribution channels to infostealer distribution, highlighting that such social engineering techniques remain prevalent and effective.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- HBO Max Reddit account compromised to serve ClickFix attacks theregister.com