Researchers Demonstrate Ghostscript Sandbox-Escape RCE via Crafted File Uploads in Popular Apps
A now-patched flaw in Ghostscript allows a crafted file to escape the program's security sandbox and run commands on the server that processes it. Ghostscript is the interpreter that many Linux servers use to convert uploaded PDFs, PostScript files, and images into other formats, often without the application calling it directly. Security firm pwn.ai showed this week that ordinary upload,
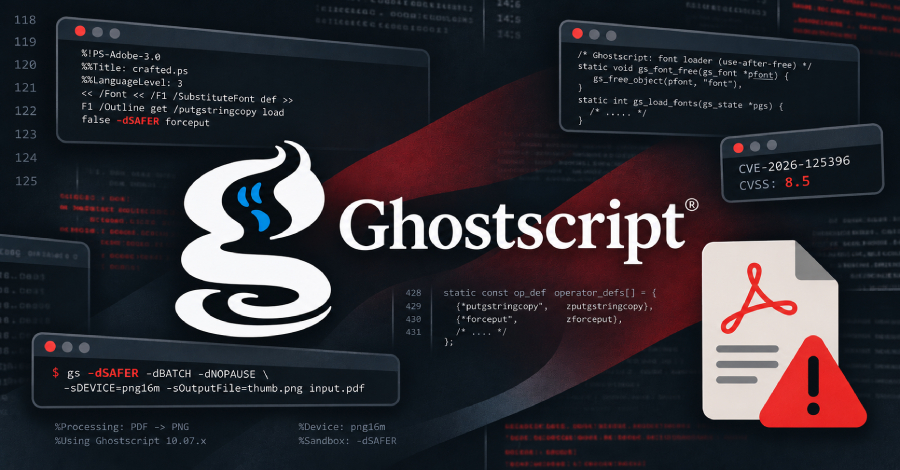
A security flaw in the Ghostscript interpreter allows attackers to exploit crafted file uploads from popular applications, bypassing the program's security sandbox and running malicious commands on the server. This vulnerability, identified as CVE-2026-125396, was patched on September 8 by the maintainers of Ghostscript. It affects file conversion, preview, and print features in about ten common applications, including ImageMagick, Pillow, libvips, and Qt plugins.
The issue arises from a use-after-free bug in the font loading component of Ghostscript, which allows attackers to disable the -dSAFER sandbox and execute commands. The exploitation can occur through various means, such as anonymous print jobs, emailed attachments, and public upload forms. The vulnerability is classified as a local flaw but can be accessed remotely through print jobs, email, and web uploads.
Although WordPress Core itself needed authentication to upload files, other applications like Forminator and Essential Addons for Elementor required less stringent access. Despite the patch, system controls and authentication measures can still help mitigate the risk until the renderer is updated.
Rewritten by urgent.news; may contain errors — check the original.
Source: thehackernews.com