AI Supply Chain Security: What Canary Tokens Found
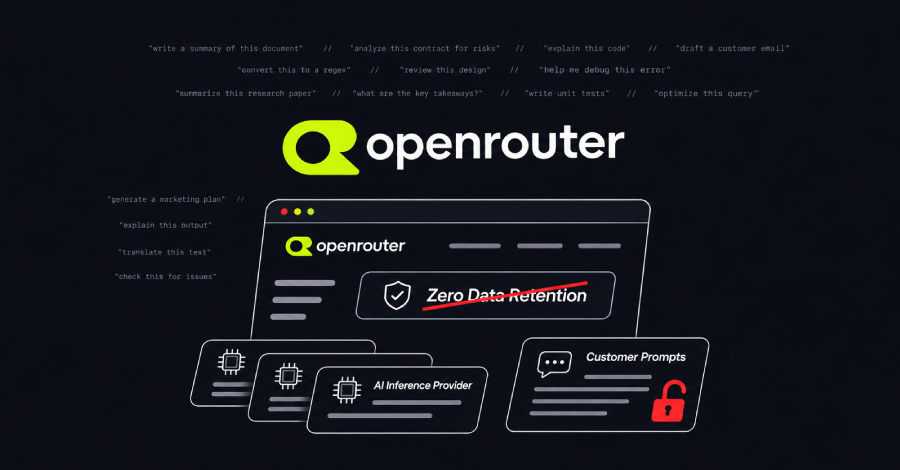
Researchers from Dragos submitted over two million AI prompts to various providers, embedding unique URLs and "canary tokens." Canaries serve as trackable markers to monitor where data breaches occur. Over a five-month period from July to November 2026, the investigation revealed three key findings.
Firstly, evidence of provider compromises was discovered. The researchers observed attempts to access controlled test systems and canary AWS accounts using seeded test prompts. Multiple resellers operating through an AI inference marketplace were able to view and retain customer prompts without exploiting vulnerabilities or bypassing platform controls.
Secondly, failures in privacy and data-handling practices were identified. The researchers observed cases where providers did not honor customer privacy settings or published policies. For example, prompts submitted to U.S.-based providers were transmitted to Chinese AI organizations, unique URLs were accessed months after a single inference request, and one seeded link appeared in an internal company chat in China.
Lastly, failures in privacy and data-handling practices were observed. Multiple cases of providers not honoring customer privacy settings or published policies were identified, such as prompts transmitted to Chinese AI organizations and unique URLs accessed months after a single inference request. One seeded link even appeared in an internal company chat in China.
Rewritten by urgent.news; may contain errors — check the original.
Source: dragos.com