I paired Pi-hole with Unbound on a Raspberry Pi, and my home network resolves its own DNS without Google or Cloudflare
A compact Raspberry Pi setup that blocks trackers and performs its own recursive DNS lookups locally.
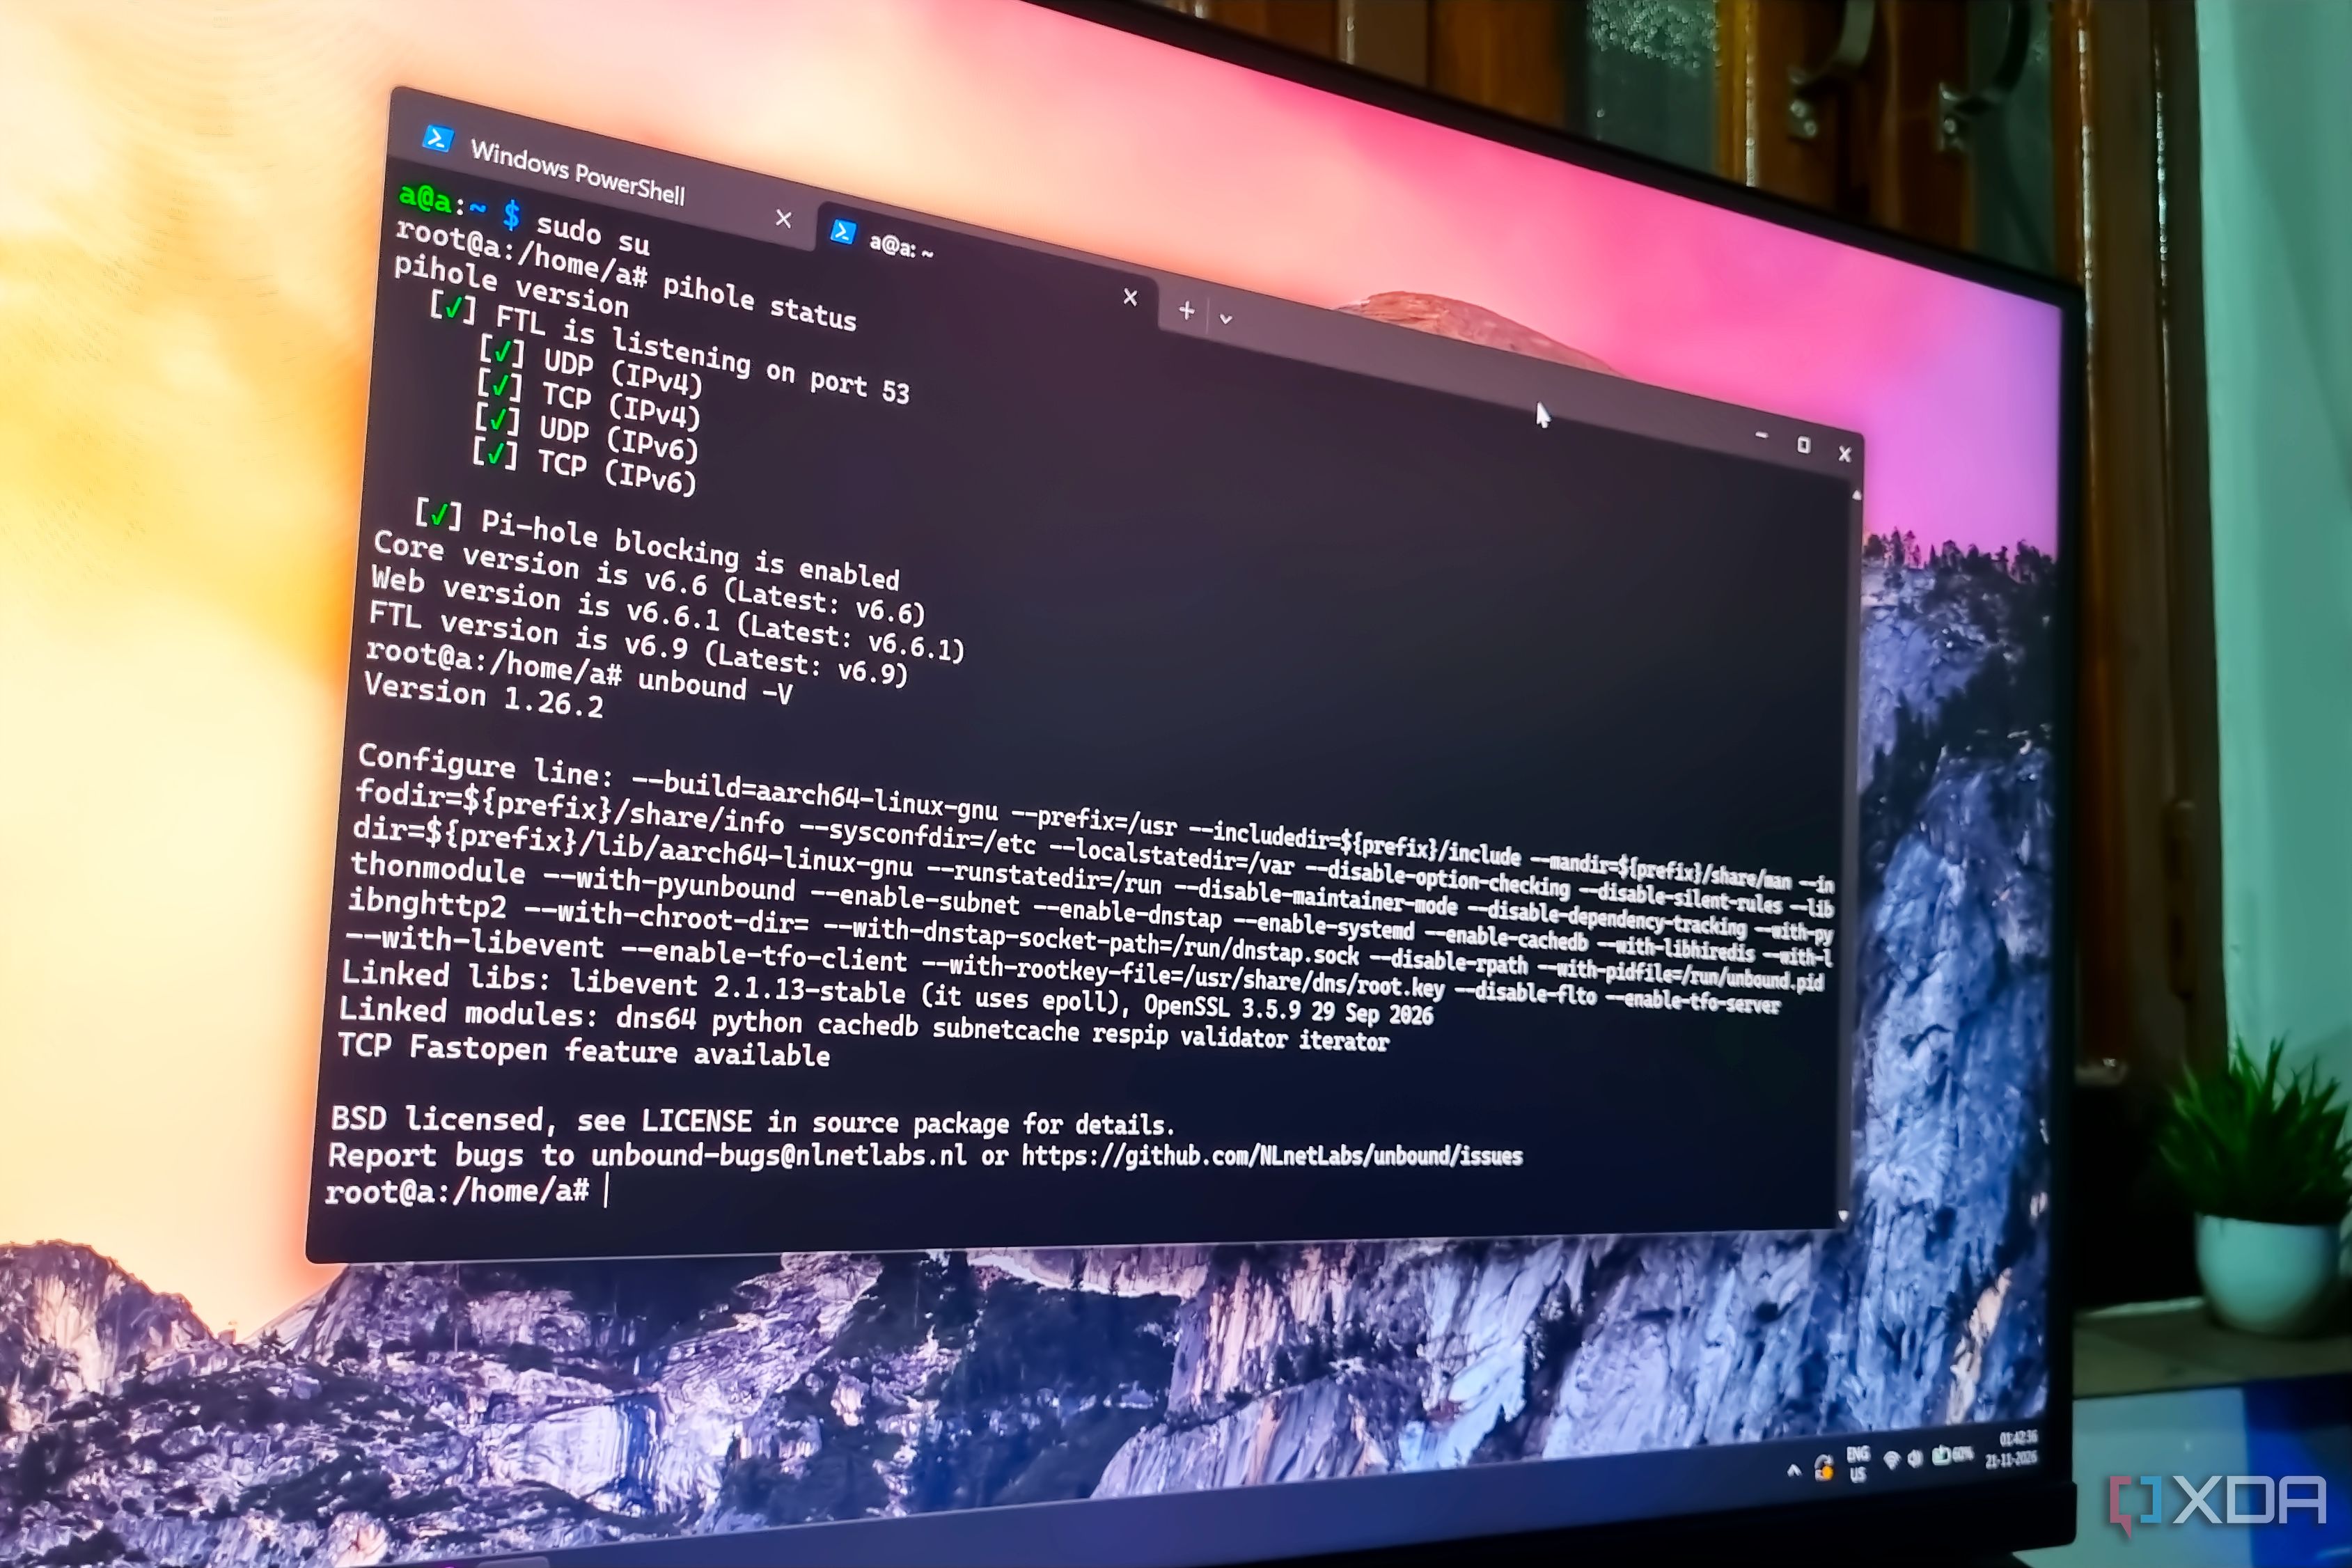
The article discusses the use of Pi-hole and Unbound on a Raspberry Pi to enhance privacy and control over a home network's DNS requests. Pi-hole, a popular DIY project, blocks ads and trackers by filtering DNS requests before they reach the public DNS provider. However, Pi-hole still relies on an upstream DNS resolver, like Google DNS or Cloudflare, for complete DNS resolution.
Unbound, a recursive DNS server, can be added alongside Pi-hole to handle DNS queries locally, providing an additional layer of privacy. Both Pi-hole and Unbound operate within the same DNS hierarchy as public DNS providers, but by using a Pi-hole and Unbound setup, the DNS requests are processed locally instead of being sent to external servers.
While this combination improves privacy, it still leaves room for potential security concerns. Unbound sends plaintext DNS queries without encryption, making it vulnerable to monitoring by ISPs or other observers. To address this, implementing an encrypted tunnel, such as WireGuard VPN, can mask traffic and provide a more secure connection.
In summary, running Pi-hole and Unbound on a Raspberry Pi offers enhanced control over DNS requests and improved privacy compared to relying on an ISP-managed or public DNS provider. However, additional measures are needed to ensure complete security, such as implementing encrypted VPN tunnels.
Rewritten by urgent.news; may contain errors — check the original.