Sticky note on monitor provided keys to the company’s kingdom
Don't leave your credentials out in public, where any visitor can see them.
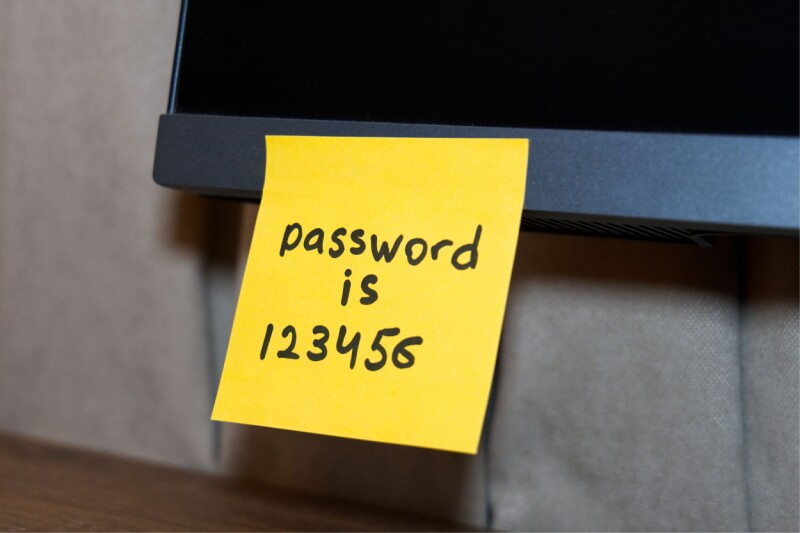
In a recent incident, a company's security was breached due to a sticky note with sensitive information left on an employee's monitor. Christian Espinosa, a seasoned penetration tester, discovered the note during a routine office walkthrough. The note contained a password that Espinosa used to gain access to the employee's account.
From there, he was able to infiltrate the company's network, accessing shared drives, HR files, salaries, and internal server names. The breach exposed personal identifiable information (PII) and financial records, posing serious risks of payroll fraud, identity theft, and vendor-payment fraud. Espinosa highlighted the importance of proper password management and limiting access to critical data.
The company acted swiftly, disabling the compromised account, reviewing VPN access logs, and tightening permissions on sensitive shares. Espinosa emphasized the potential for further damage if the malicious actor had continued the attack after the penetration test, underscoring the need for robust security measures.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Other reports of this story
- Sticky note on monitor provided keys to the company’s kingdom theregister.com