Sticky note on monitor provided keys to the company’s kingdom
Don't leave your credentials out in public, where any visitor can see them.
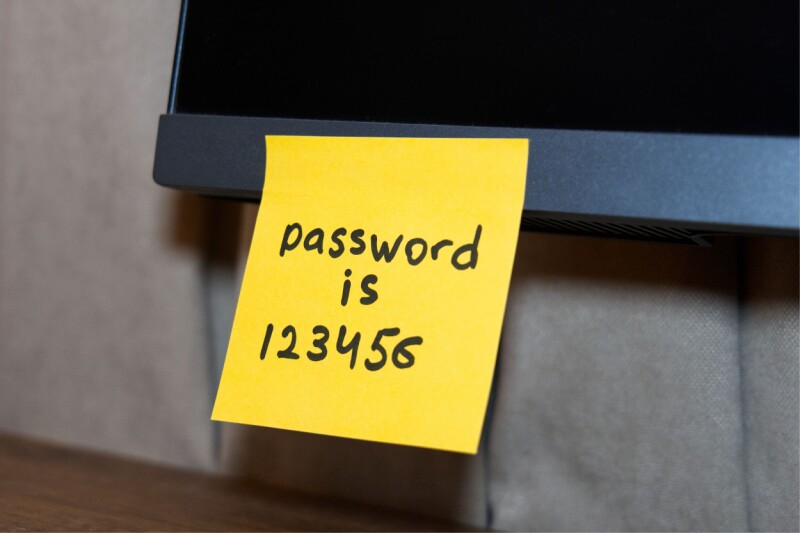
In a stark reminder of the perils of lax security practices, a password written on a sticky note taped to an employee's computer monitor provided unauthorized access to a company's network. Christian Espinosa, a seasoned penetration tester and CEO of Blue Goat Cyber, stumbled upon the note during a routine security walkthrough. Dismissing the sticky note as an innocuous piece of paper, Espinosa nevertheless extracted the password and promptly gained entry to the employee's account.
Unfettered access to the account allowed Espinosa to infiltrate the company's vital systems. He accessed a shared drive, containing a trove of sensitive employee information, such as home addresses, driver's licenses, and W-4 forms. Espinosa also discovered spreadsheets listing salaries and a list of internal server names, complete with the names of the individuals responsible for each server.
Alarmingly, the employee's account also granted access to a document outlining the steps to log into the accounting server, a seemingly innocent treasure trove to the cunning tester.
The account's reach extended to the accounting server, a prime source of client information, including vendor banking details, invoices, and payment records. Espinosa's unauthorized access to this server granted him the power to commit acts of payroll fraud, identity theft, and vendor-payment fraud. After making these discoveries, Espinosa immediately notified the client, who swiftly disabled the rogue account and began investigating possible breaches.
The aftermath highlighted the inherent dangers of leaving passwords scattered in plain sight. Espinosa emphasized the importance of securing physical documents and limiting access to sensitive data. The client, shaken by Espinosa's revelations, took immediate action to bolster their network security, tightening permissions on critical file shares and restricting access to those with a genuine need for the information.
Espinosa's cautionary tale serves as a stark reminder that even the most innocuous actions, such as taping a password to a monitor, can open the door to disastrous consequences.
Written by urgent.news from The Register Science's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Sticky note on monitor provided keys to the company’s kingdom theregister.com