Feds warn grocers: Don't chill on cyber defenses as freezer hacking spree heats up
No documented attacks against American supermarkets…yet
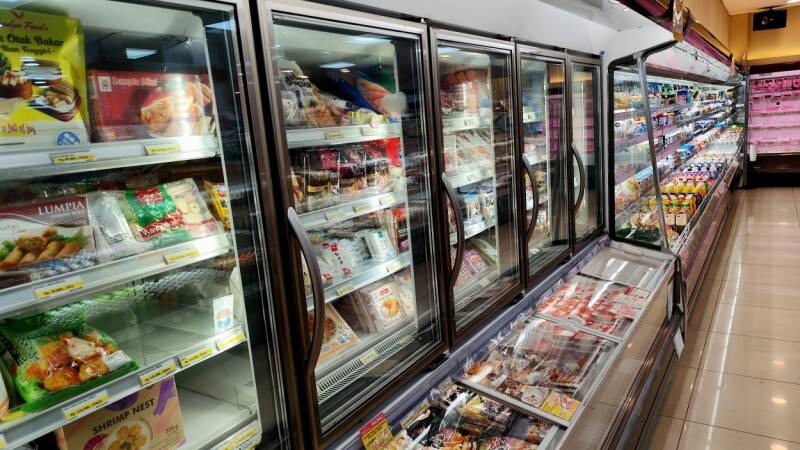
U.S. federal agencies are warning grocers to bolster their cyber defenses as hacking incidents targeting industrial smart freezers escalate, particularly in Europe. FBI Cyber Branch Operations Director Brett Leatherman stated that malicious actors are increasingly targeting critical infrastructure sectors globally, posing risks to inventory and equipment.
In recent months, hackers have compromised thousands of remote-controlled refrigeration systems across multiple grocery stores in France, Belgium, Ireland, Luxembourg, and Sweden. The attacks raise internal temperatures, leading to spoiled food and, in extreme cases, fires. The Register attempted to inquire with the FBI about documented attacks on refrigeration and cold chain monitoring systems in the United States but had not received a response or awareness of such incidents.
However, there are indications that U.S. operators are cognizant of the issue. Dutch grocery company Ahold Delhaize, which operates supermarket chains like Food Lion, Giant Food, and Stop & Shop, temporarily disconnected IT systems after a cyberattack affected many of its US and European brands, with European supermarkets being among the hit stores.
The Pentagon is investigating a series of freezer malfunctions at U.S. military bases in August, believed to be the result of a suspected cyberattack, according to four officials familiar with the matter.
In a recent advisory, the FBI, Cybersecurity and Infrastructure Security Agency (CISA), Health and Human Services, and departments of Agriculture and Transportation have issued a warning to organizations about ongoing cyber threats against industrial refrigeration and cold-chain monitoring systems. The agencies explain that attackers exploit unpatched or internet-accessible controllers to manipulate settings and force units into continuous heating or defrost cycles.
This can result in extensive inventory loss, equipment hazards, and the spoilage of food or medications.
To mitigate these risks, the government agencies advise grocers to take immediate action. They recommend disconnecting industrial control systems from the public internet whenever possible. If remote access is necessary, they suggest employing firewalls or edge devices, updating them to the latest versions to minimize vulnerabilities. Additionally, creating a dedicated VLAN for operational technology (OT) devices can help isolate industrial devices from business networks.
The agencies also urge grocers to replace default passwords with strong passwords and policies, enable phishing-resistant multifactor authentication (MFA) whenever feasible, and apply patches in a timely manner. They advise retiring and replacing legacy devices that no longer receive security updates from manufacturers. Defining and maintaining a device and IP allow-list, limiting access to OT devices to only those on the list, and enabling logging and regularly reviewing logs for any unusual activity are also recommended measures to bolster cyber defenses.
Written by urgent.news from The Register Science's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.