Apple Will Check Public iCloud Links for Harmful Content Starting in iOS 27.3
Apple says it will start checking public iCloud links for harmful content in iOS 27.3, iPadOS 27.3, macOS 27.3, and visionOS 27.3. Images in iCloud Photos and files in iCloud Drive shared using the "Anyone with the link" option will be "made accessible to Apple" for a content check. Apple doesn't define harmful content, but it could mean malware, malicious files, and/or child sexual abuse…
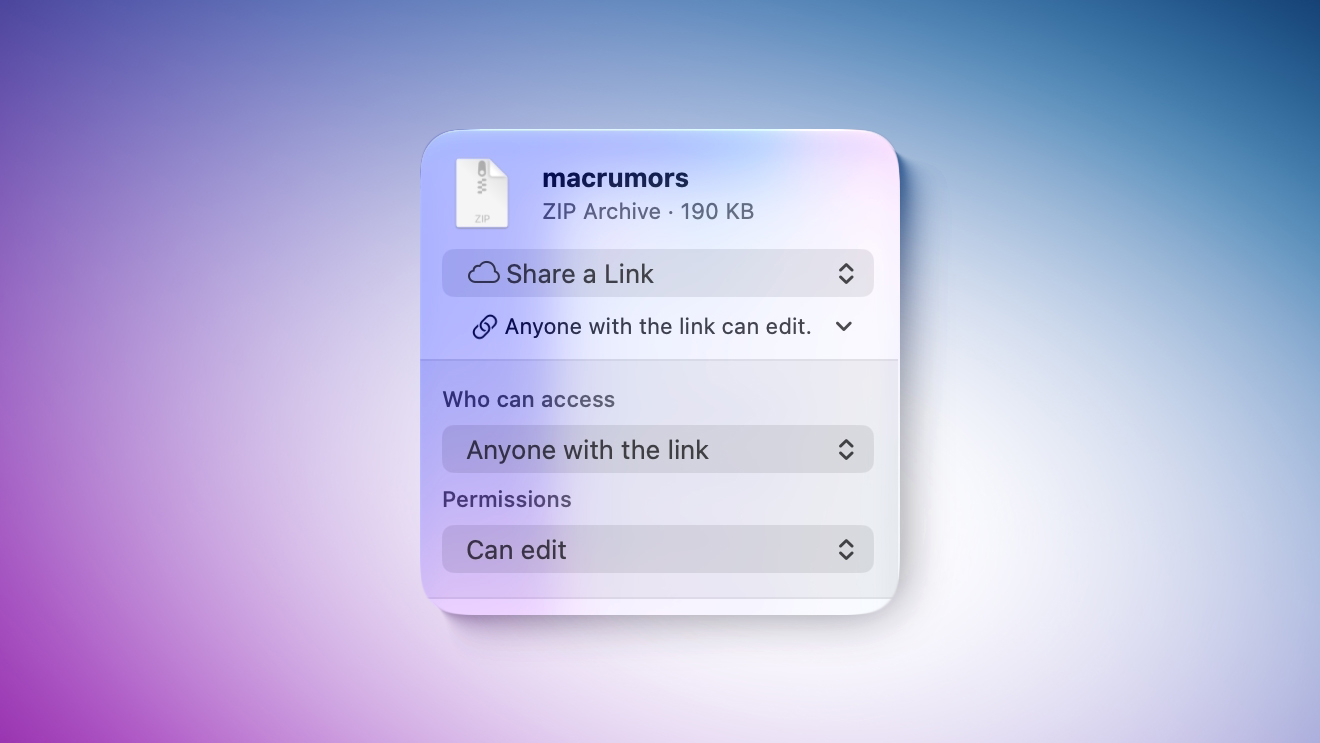
Apple has announced that it will begin scanning public iCloud links for potentially harmful content in the upcoming iOS 27.3, iPadOS 27.3, macOS 27.3, and visionOS 27.3 operating system updates. Files in iCloud Photos and those shared through the "Anyone with the link" option in iCloud Drive will be accessible to Apple for review.
While Apple has not provided a specific definition of what constitutes harmful content, it could involve malware, malicious files, or child sexual abuse material (CSAM), considering Apple's mention of law enforcement cooperation. Attempting to upload harmful content may result in Apple removing, refusing, modifying, or deleting the content and potentially taking action against the user's Apple Account.
Options for sharing iCloud files include "Send a Copy," which directly transmits a file, or "Share a Link," allowing someone to download the file. The latter option, "Anyone with the link," is the one subject to Apple's content checks. It remains unclear whether links created before the 27.3 update will undergo review. The software containing these changes is currently available to developers for beta testing and will be released to the public in December.
Written by urgent.news from MacRumors's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Also reported by 3 other outlets
- Apple will check shared iCloud links for ‘harmful content’ theverge.com
- iCloud's 'Anyone with the Link' option will trigger Apple content checks appleinsider.com
- Apple says it will check iCloud items shared to "Anyone with the link" for "harmful content" in 27.3 OS versions, and may delete the content or disable accounts (Ryan Christoffel/9to5Mac) 9to5mac.com