Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data
Attackers posing as IT support on Microsoft Teams talked employees into giving them remote control of their PCs. They then used insecure Active Directory Certificate Services (AD CS) settings to obtain login certificates for privileged accounts, including one for a domain controller. Microsoft said in a report that it investigated two such intrusions, one of which resulted in company
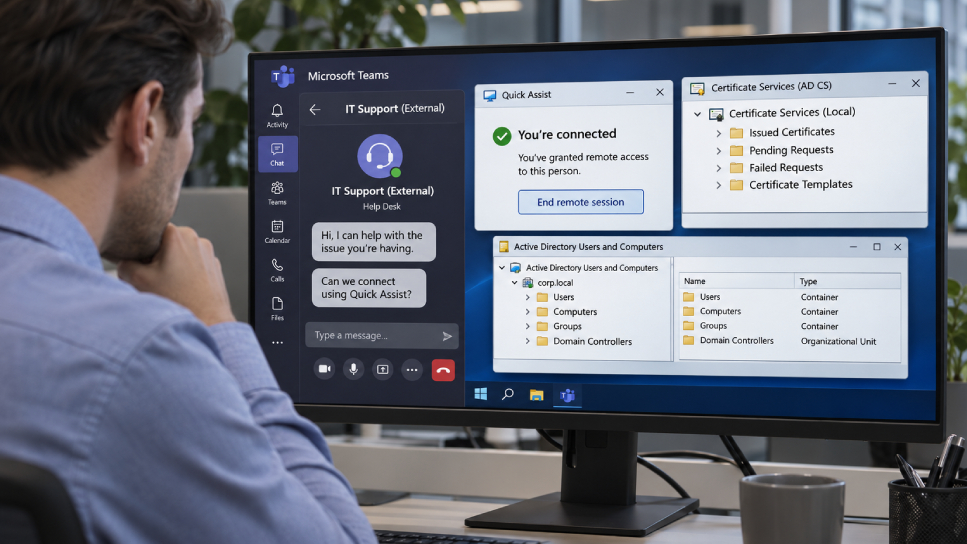
Attackers impersonated IT support on Microsoft Teams to gain remote access to employees' computers. Leveraging vulnerabilities in insecure Active Directory Certificate Services (AD CS) settings, the attackers obtained login certificates for privileged accounts, including one for a domain controller. Microsoft reported two such intrusions, each resulting in the theft of company data.
The incidents were initiated by social engineering tactics and poorly configured AD CS settings, not by any flaws in Microsoft Teams itself. The attackers used Quick Assist, a remote-help tool built into Windows, to gain direct control of the workstations. They then dropped and ran malicious files, exploiting the compromised accounts to move data to external servers.
Microsoft's security measures, such as automatic attack disruption and Defender alerts, disrupted these attacks, though one compromised account remained active in some cases. The report emphasizes the importance of proper AD CS configuration and swift response to contain and mitigate these types of breaches.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.