Urgent.News

What's breaking now, across thousands of outlets.

Tech

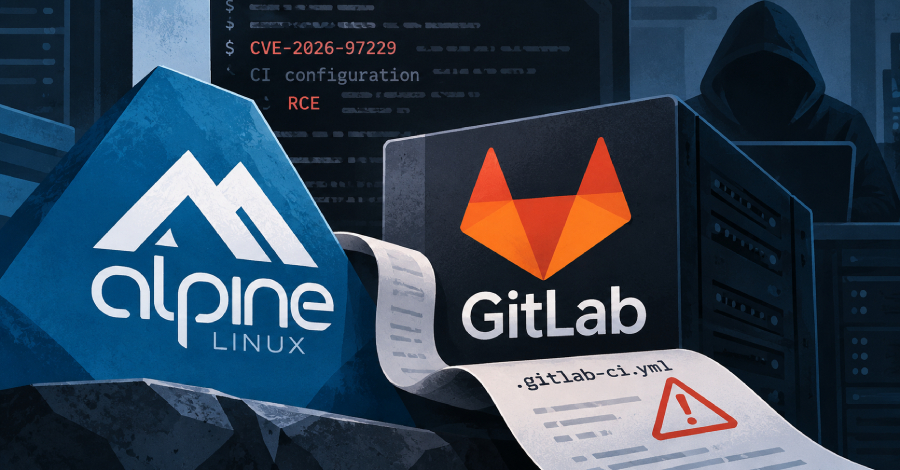
Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open

An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server a week after GitLab released a fix, Alpine Linux said on 28 October. The flaw, CVE-2026-97229 (CVSS score: 10.0), can let an attacker run code on a GitLab server through a crafted regular expression in a CI configuration. Alpine found no evidence that the attack worked but
Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

Taking Government Off Your To-Do List

AI could take more everyday administration off people’s hands. BCG Middle East’s Faisal Hamady explains why delivering that convenience will require reliable services, clear boundaries and a human…

Doosan Enerbility to Manufacture Key Reactor Module for NuScale Power’s SMR Project

Doosan Enerbility is expanding its role in the global small modular reactor (SMR) industry after signing a contract with U.S.-based NuScale Power to manufacture a key reactor component for its SMR…

  • Doosan Enerbility contracts to manufacture URPV module for NuScale Power's SMR.
  • Agreement signed October 29, expanding from material to equipment manufacturing.
  • NuScale Power's SMR design first approved by U.S. Nuclear Regulatory Commission.

More from Thursday 29 October →