Urgent.News

What's breaking now, across thousands of outlets.

Tech

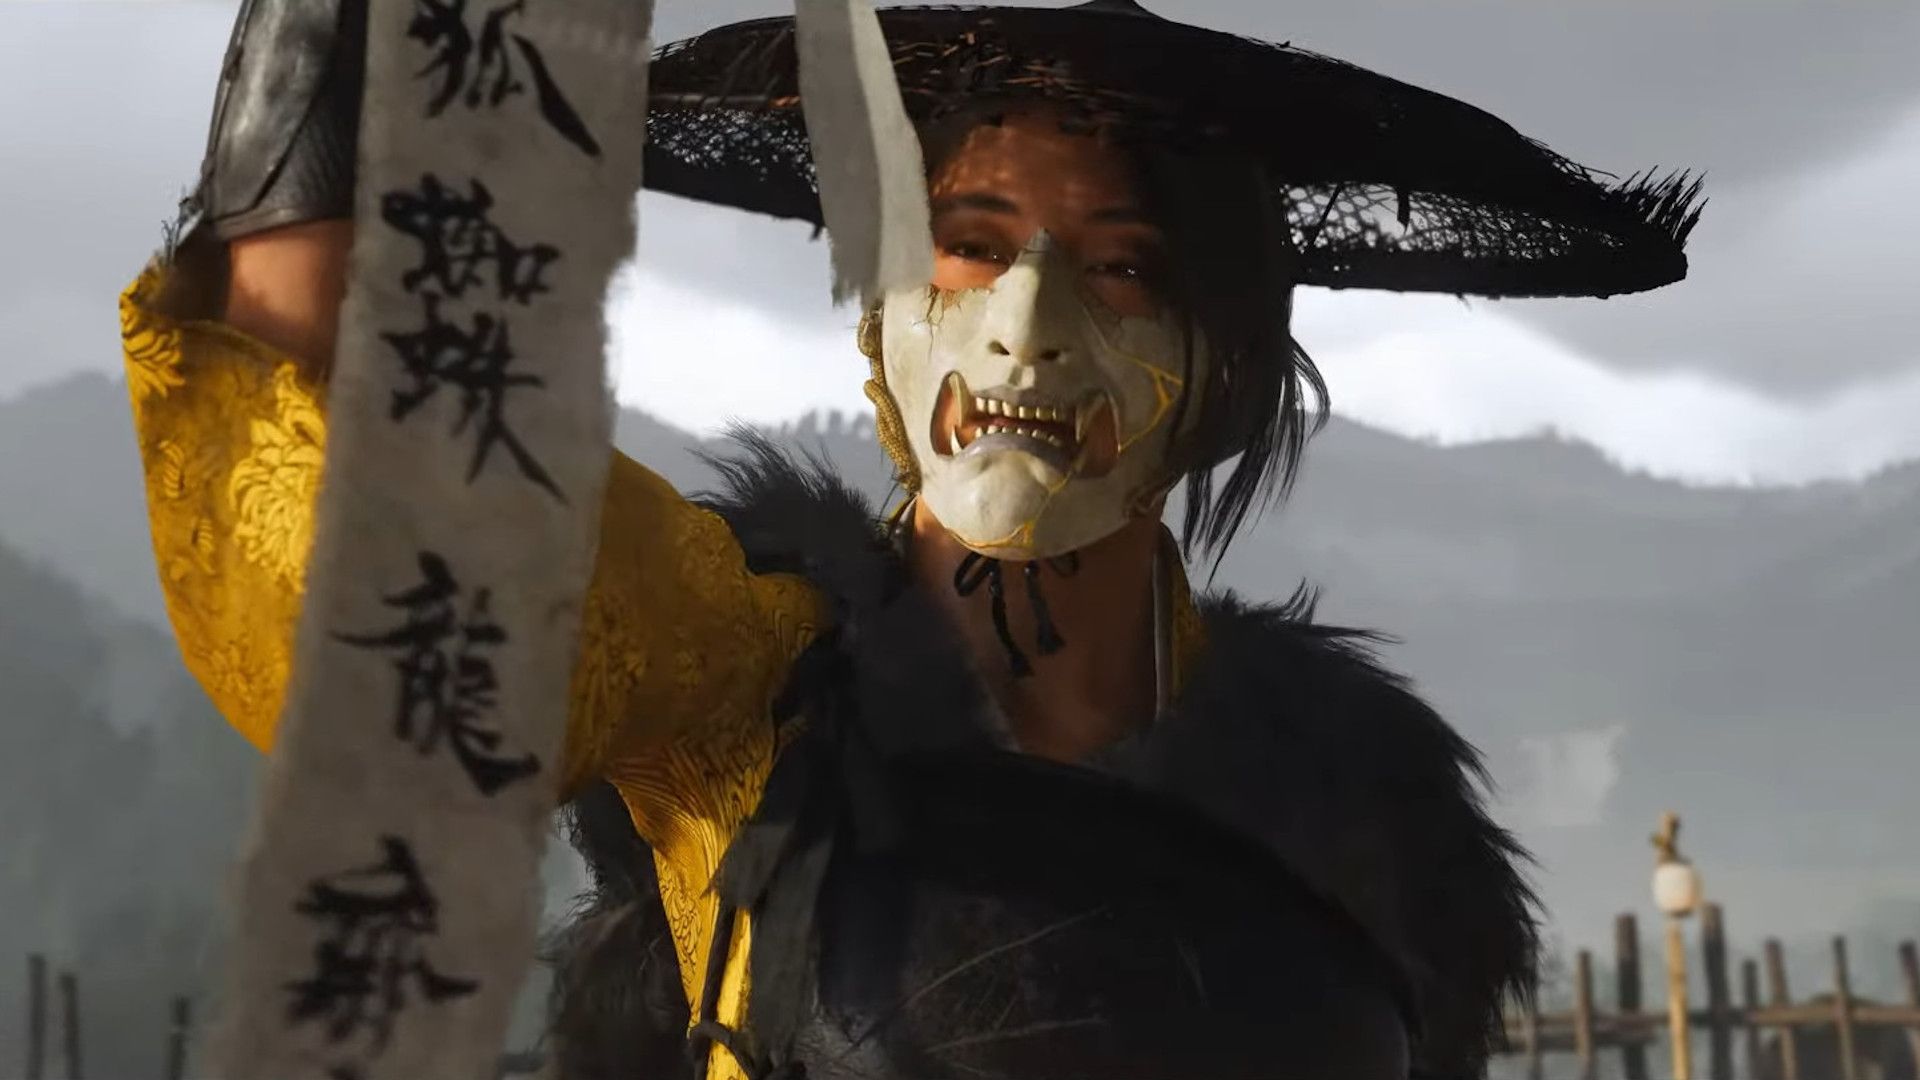
You just can't win—despite Ghost of Yōtei selling millions of copies, 24 people are reportedly being let go from Sucker Punch

Are the "challenges in the market" in the room with us right now?
You just can't win—despite Ghost of Yōtei selling millions of copies, 24 people are reportedly being let go from Sucker Punch

Despite the commercial success of Ghost of Yōtei, developer Sucker Punch has reportedly laid off 24 employees, marking a 10% reduction in staff. The studio's most recent game sold 3.3 million copies in its first month, making it the 11th best-selling game in the US in 2025. The email notifying staff of the layoffs stated that the decision was made after a careful review of market challenges and team needs for future projects.

The company assured employees that the decision was not made lightly and provided support during the transition. However, the article questions the health of the gaming industry, citing rising production costs, the impact of the AI bubble, and the consequences of Covid-19 overhiring.

Written by urgent.news from PC Gamer's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.

Read the original at pcgamer.com →

More in Tech

Retroachivment on real PS2

Hi everyone! I like building all sorts of stuff, and I figured I'd share what I've been working on for the last two months. I think you might like this one.

  • RetroAchievements integrated into real PlayStation 2 console
  • Achievements earned and recorded in RA account
  • Stable version 1.0.0 released on October 26

The read-only disk mount that left no trace on the server

The read-only disk mount that left no trace on the server FirstVDS described an unusual detail in its 19 October 2026 disclosure.

  • Attackers mounted customer virtual servers disks in read-only mode on Oct 19, 2026.
  • No traces of attack on affected virtual servers, making detection difficult.
  • Detect attacks by monitoring read-only attaches not initiated by backups or non-storage accounts.

The Two URLs Every WordPress Attacker Tries First (And How to Stop Guessing Being a Risk)

If you've ever checked your WordPress server logs, you've seen it: a steady stream of requests to /wp-login.php and /wp-admin from IPs you've never heard of, at all hours, with no referrer.

  • Default login URLs /wp-login.php and /wp-admin are primary targets for automated WordPress attacks.
  • Bots consistently use usernames like "admin" and site domain names in scan patterns.
  • Rate-limiting is more effective than CAPTCHA in mitigating these automated login attacks.

The call sheet is not a table

Backlot is an open-source film production scheduling app. It has five tables and none of them is the call sheet. On a film set, the call sheet is the document that tells you where to be and when.

  • Backlot film production app lacks a traditional call sheet table
  • Unique design generates call sheets per user, not as a separate table
  • Owner username linked to email, simplifying access control

The desktop is the agent - a first look at Praxis Linux (Phase 0)

90-second demo. Everything in it ran on a local model. The shape of the problem The desktop hasn't changed shape in thirty years.

  • Praxis Linux reimagines desktop as AI agent, not side AI
  • Canvas UI listens, understands, adapts to user needs
  • Phase 0 pre-alpha spike with Conversation, File, Code modes

More from Tuesday 27 October →