PHP2Shell: No login, no app code, no warning. What next?
PARTNER CONTENT: Learn what the flaws are, how far exploitation has gone, and how to get to full coverage fast with Tanium
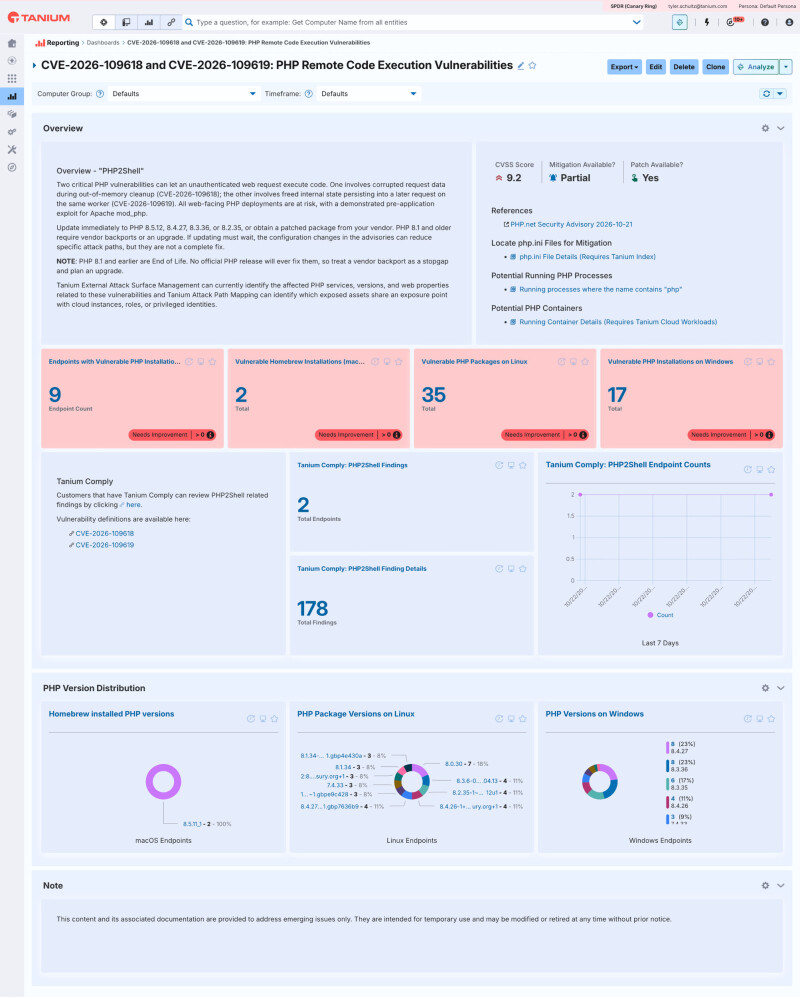
PHP2Shell represents two critical flaws that allow unauthenticated attackers to execute code on a server using a simple web request. Both vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affect every version of PHP prior to 8.5.12, 8.4.27, 8.3.36, and 8.2.35. PHP is found in various server setups including PHP-FPM, mod_php, php-cgi, FrankenPHP, and LiteSpeed.
The risk of exploitation is highest on ARM64 systems and those with address space layout randomization (ASLR) disabled. While reliable public exploits are scarce, early attacks have been detected by watchTowr and Cloudflare. Most at risk are internet-facing PHP applications, especially those running mod_php or on ARM64 hosts. Organizations should prioritize patching vulnerable PHP installations and monitor their systems for any signs of exploitation.
Tanium Guardian content is available to help detect and prioritize patching of PHP instances across Linux, Windows, and macOS environments.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.