PHP2Shell: No login, no app code, no warning. What next?
PARTNER CONTENT: Learn what the flaws are, how far exploitation has gone, and how to get to full coverage fast with Tanium
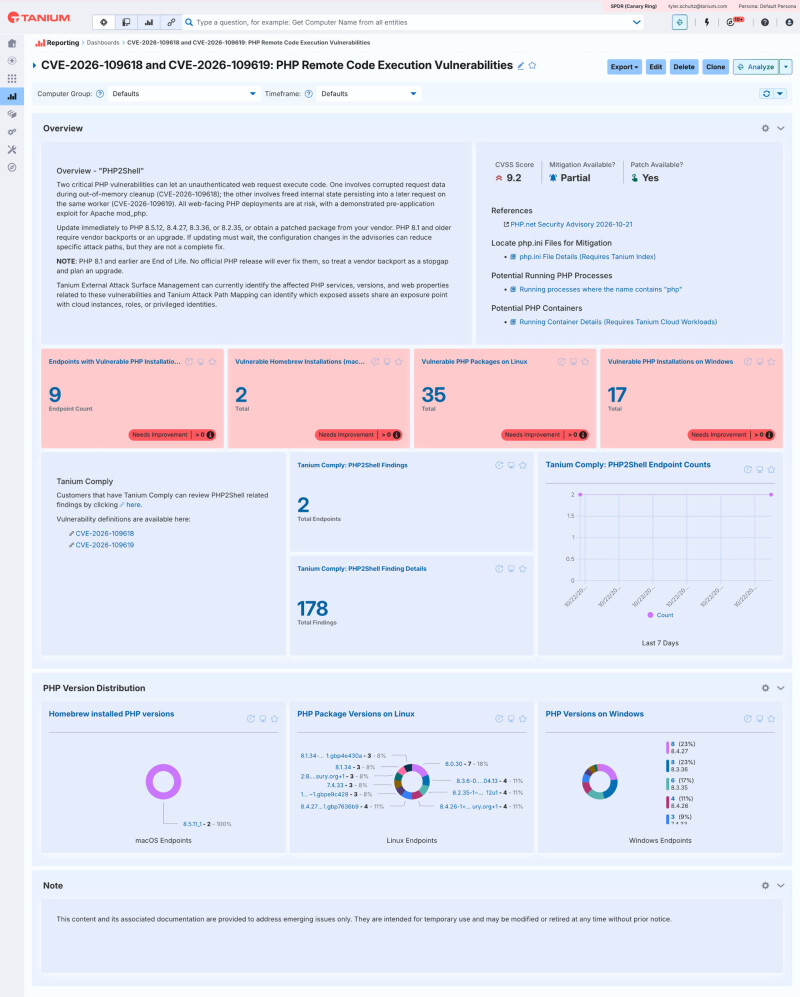
Two critical flaws, CVE-2026-109618 and CVE-2026-109619, named PHP2Shell, allow an unauthenticated attacker to run code on a server using only a crafted web request. Both vulnerabilities affect every earlier release of PHP, and public exploitation has begun. The patch to address these flaws is available for PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
However, finding and patching every copy of PHP in an environment is challenging, as PHP often hides in multiple locations. Tanium has released Guardian content to help identify PHP installations across Linux, Windows, and macOS, enabling organizations to prioritize patching efforts and minimize the risk of exploitation.
Written by urgent.news from The Register Science's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.