Leaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release Pipeline
LiteLLM on Friday revealed that an Agent Platform master key accidentally published to a public GitHub repository in late May 2026 ultimately allowed the threat actor to push a malicious version of the popular Python package. "On May 27, 2026, a configuration file was committed to the public LiteLLM-Labs/lite-harness repository which inadvertently contained the master key to a deployment of
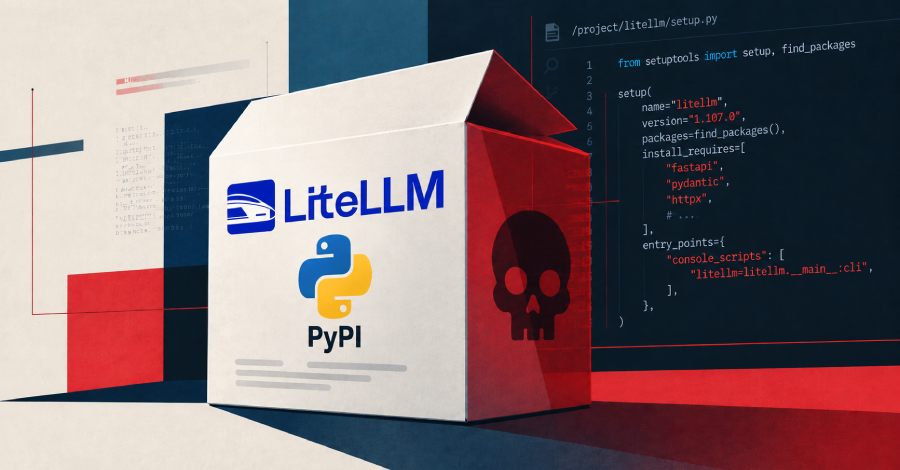
On Friday, LiteLLM disclosed that an Agent Platform master key inadvertently published to a public GitHub repository in late May 2026 granted an attacker the ability to distribute a malicious version of the widely used Python package. On May 27, 2026, a configuration file containing the master key for LiteLLM Agent Platform, an open-source tool used for orchestrating agents, was mistakenly committed to the LiteLLM-Labs/lite-harness repository.
The mistake was identified promptly, the commit was force-pushed, and the exposed key was required to be revoked. However, the critical master key remained unrevoked. An unknown assailant (operating from IP address 69.48.229[.]143) exploited this unrestrained key on October 10, 2026, to gain access to the Agent Platform and obtain a GitHub CLI OAuth token.
This token, not properly scoped and tied to the organization's owner account, enabled the attacker to assume owner-level privileges across all repositories, facilitating credential theft. Following this breach, the threat actor triggered and approved a release by utilizing one of the compromised GitHub tokens, after redirecting the deployment to a malicious repository.
The attackers also aimed to uncover and exfiltrate additional keys and tokens, particularly upstream inference API tokens. Following the incident, LiteLLM is working to revoke every token associated with their internal systems and vendor platforms.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.