Researchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli Data
Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their "Node2Shell" proof of concept ran code on the official Node.js 24.22.0 image for Linux arm64, with no debugger or custom build, by feeding crafted data to the bundled Brotli decoder (CVE-2026-111497). Node.js disclosed the flaw
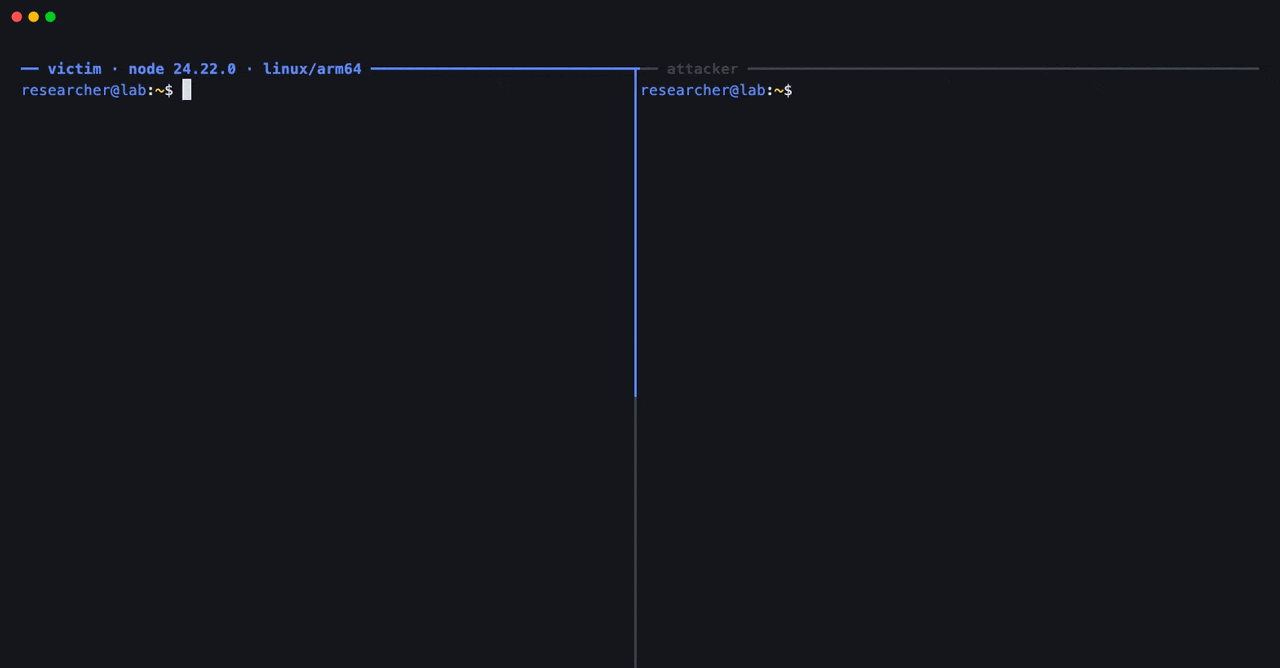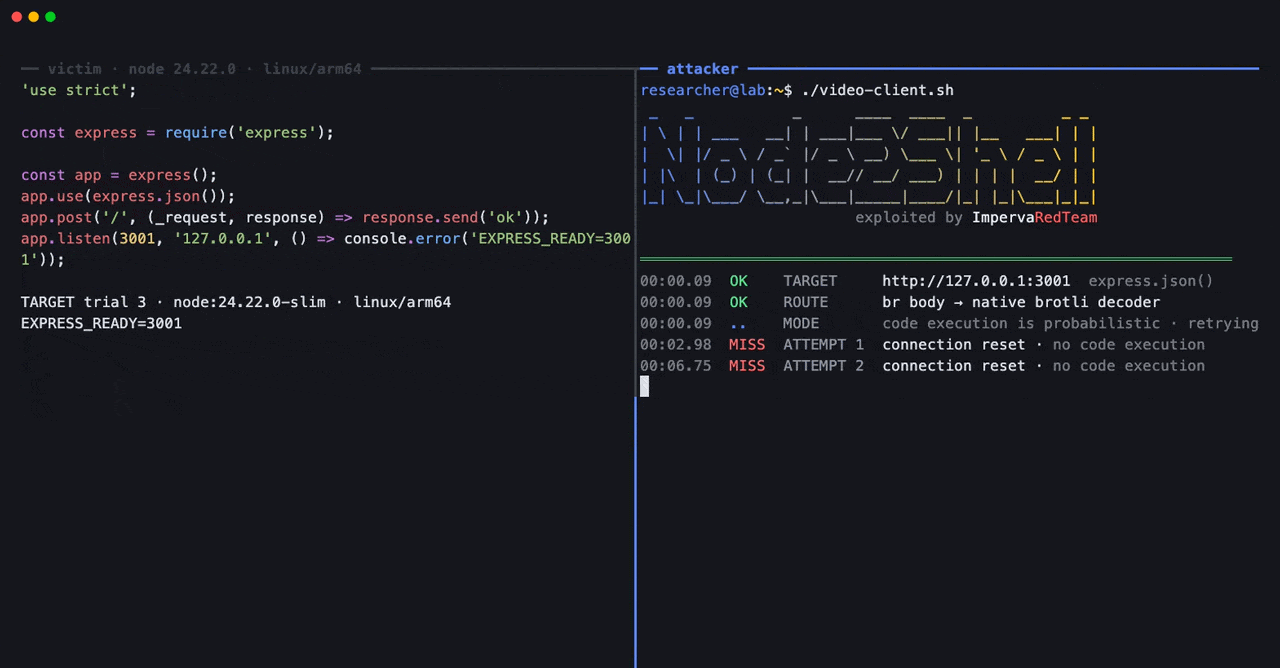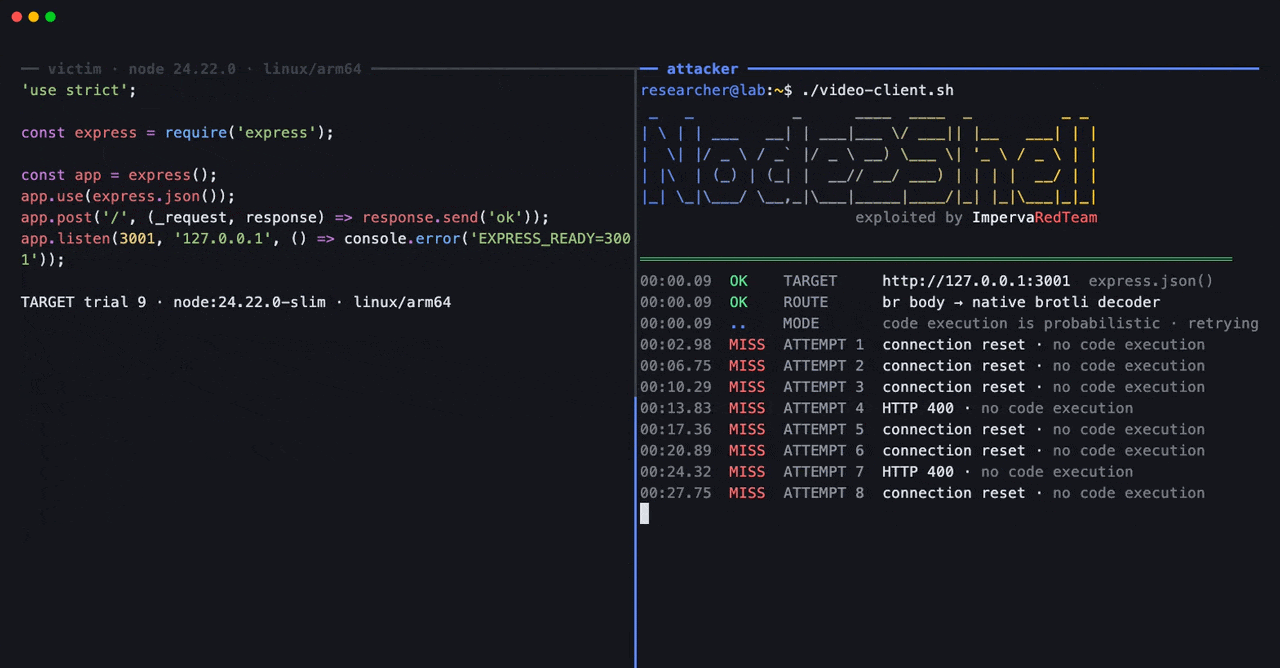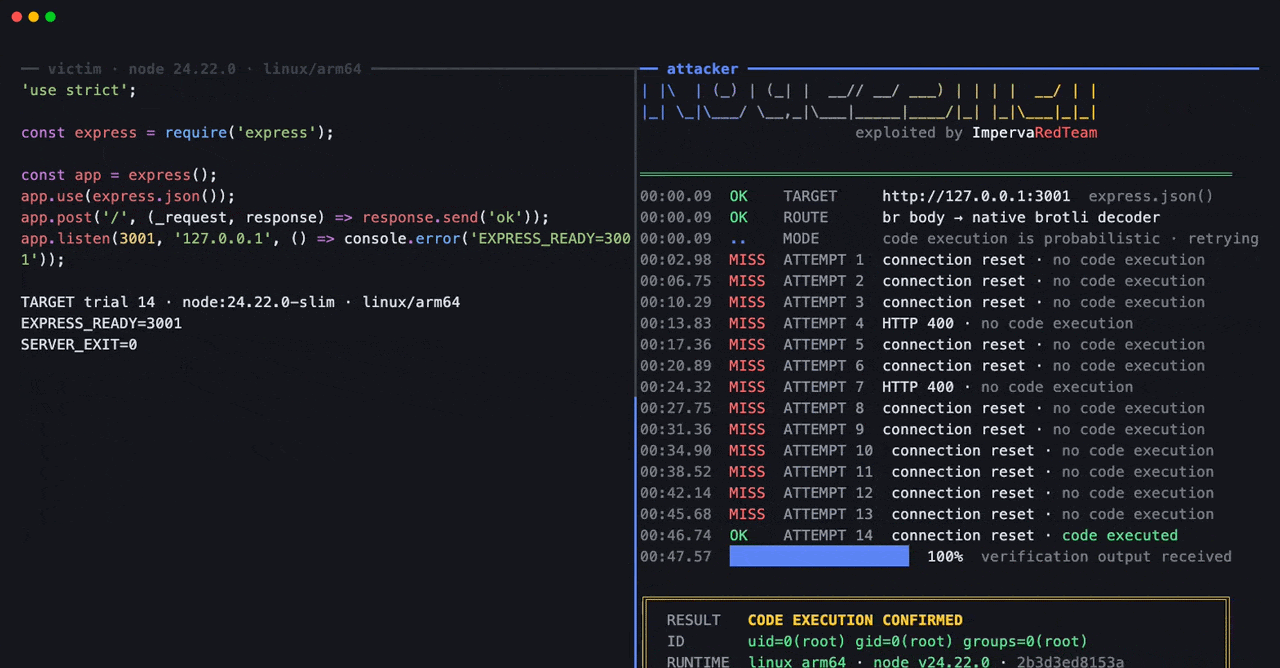
Security researchers at Imperva demonstrated a Remote Code Execution (RCE) vulnerability in Node.js called "Node2Shell". The exploit uses specially crafted Brotli data to trick the Node.js application into running malicious code. This issue affects standard Node.js builds, including the Linux arm64 version of Node.js 24.22.0, and can be exploited through either request bodies or responses in applications using Node.js.
Imperva released a proof of concept on October 21, showing that code execution was possible after several attempts, while subsequent releases like 24.22.1 rejected the crafted data and prevented code execution. The vulnerability stems from a flaw in Node.js's bundled Brotli decoder, which fails to handle an impossible point in a Brotli stream correctly, ultimately leading to an out-of-bounds write and potential code execution.
No exploitation has been reported in the wild as of October 22. Applications should update to the latest patched version to mitigate the risk, as no workaround is provided within Node.js itself.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.