Garmin opens the mic, speaker, and LTE to third-party watch apps
This could get interesting
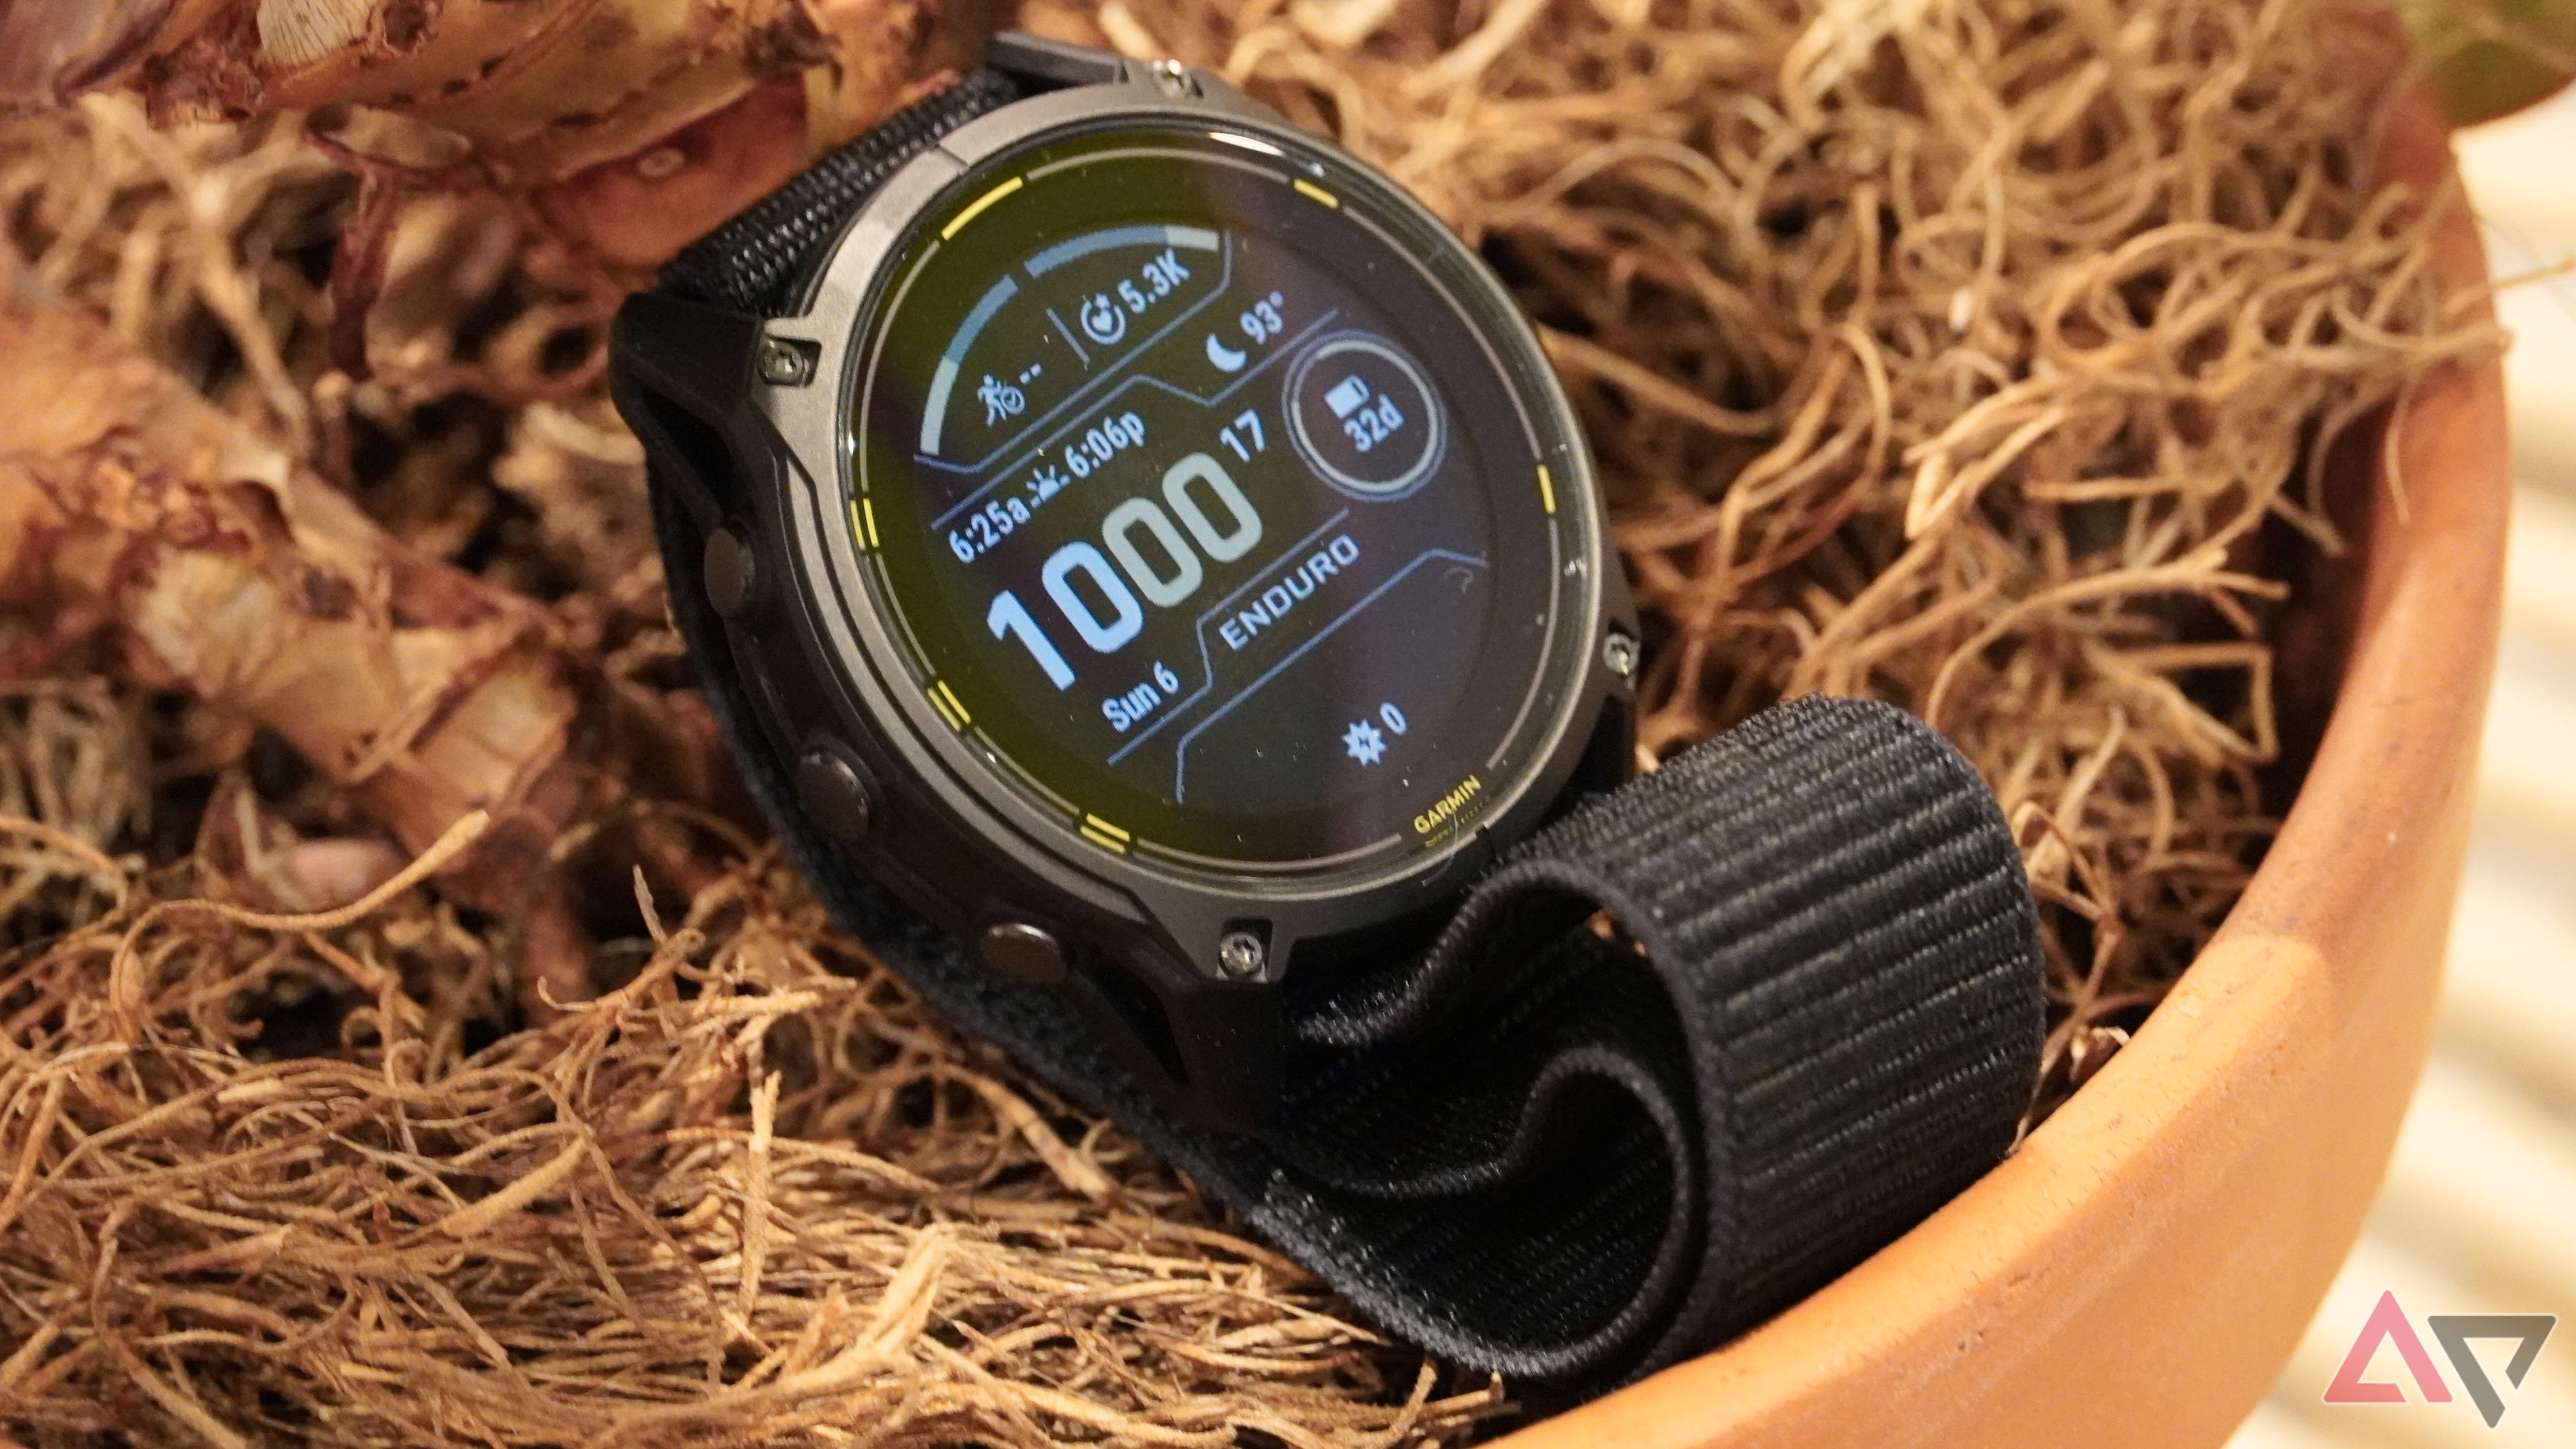
Garmin has recently expanded the capabilities of its smartwatches by granting third-party apps access to the microphone, speaker, and LTE connectivity through a new Connect IQ update. This development, as reported by Android Authority, could lead to enhanced user experiences on supported devices. The microphone feature allows for audio recording in WAV or Ogg formats, with noise and echo cancellation, while the speaker API enables third-party developers to utilize the built-in speaker on compatible watches.
Furthermore, Garmin has opened up LTE connectivity, which could be creatively employed in future applications. Supported devices include the Fenix 8, Fenix 9, Fenix E, Forerunner 70, 170, 570, and 970, as well as the Venu 4, X1, Vivoactive 6, D2, Enduro 3, Enduro 4, and other high-end models. While the update is relatively recent, it opens up possibilities for third-party developers to create better experiences on Garmin smartwatches.
The current Connect IQ Store, however, appears to be lacking in apps, reminiscent of the outdated app ecosystem of older devices like Symbian phones. This limited selection, compared to more polished app stores like Wear OS or the Apple Watch, highlights Garmin's usual approach of restricting access to their ecosystem, potentially stifling creativity among developers.
Written by urgent.news from Android Police's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Also reported by 1 other outlet
- Garmin third-party smartwatch apps are about to get more useful androidauthority.com