PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert
PHP will ship an out-of-cycle security release at 14:00 UTC today, October 21, for two critical vulnerabilities that its security team has rated 9.2 on the CVSS v4.0 scale but has not described. Security researchers at watchTowr say the two flaws allow remote code execution. Only the four supported PHP branches, 8.2 through 8.5, can receive the fix, and no exploitation has been reported so far.
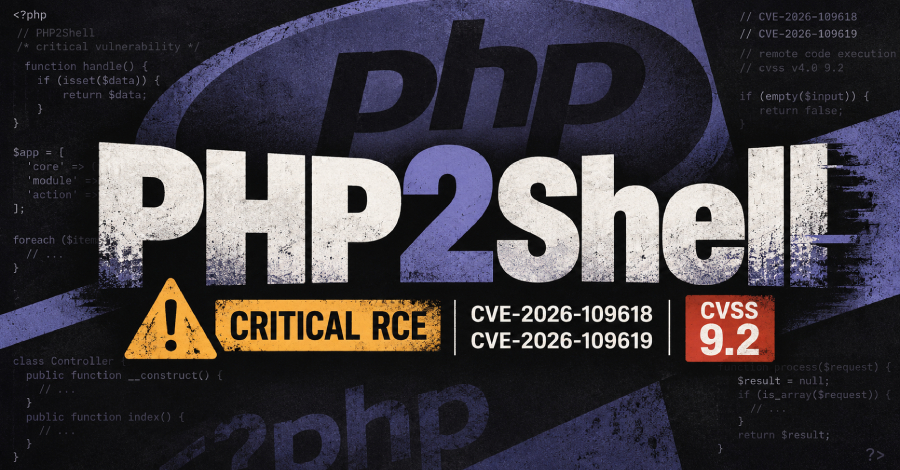
Two critical PHP remote code execution (RCE) flaws, rated 9.2 on the CVSS v4.0 scale, have prompted an emergency security alert and prompted PHP to release an out-of-cycle security update. The flaws, affecting all versions since PHP 5, have not been formally disclosed by PHP but were leaked on October 20 by a post on Hacker News.
The flaws, identified as CVE-2026-109618 and CVE-2026-109619, can allow attackers to execute arbitrary code remotely. However, the exact affected versions and the nature of the vulnerabilities remain unknown. Only the four supported PHP branches, 8.2 through 8.5, will receive the fixes, while older versions, including 8.1, 8.0, 7.x, and 5.x, will not be patched.
Researchers are calling the pair of flaws "php2shell." Security experts recommend six steps to mitigate the risks until the security release, including checking for vulnerable versions, isolating affected systems, and disabling unnecessary PHP functionalities.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.