Don't Hand Claude Your Docker Socket — Build It a Guarded One
A Python MCP server that gives Claude read-only access to Docker, with a name-resolved restart guard, secret redaction, and a 47-test mocked suite.
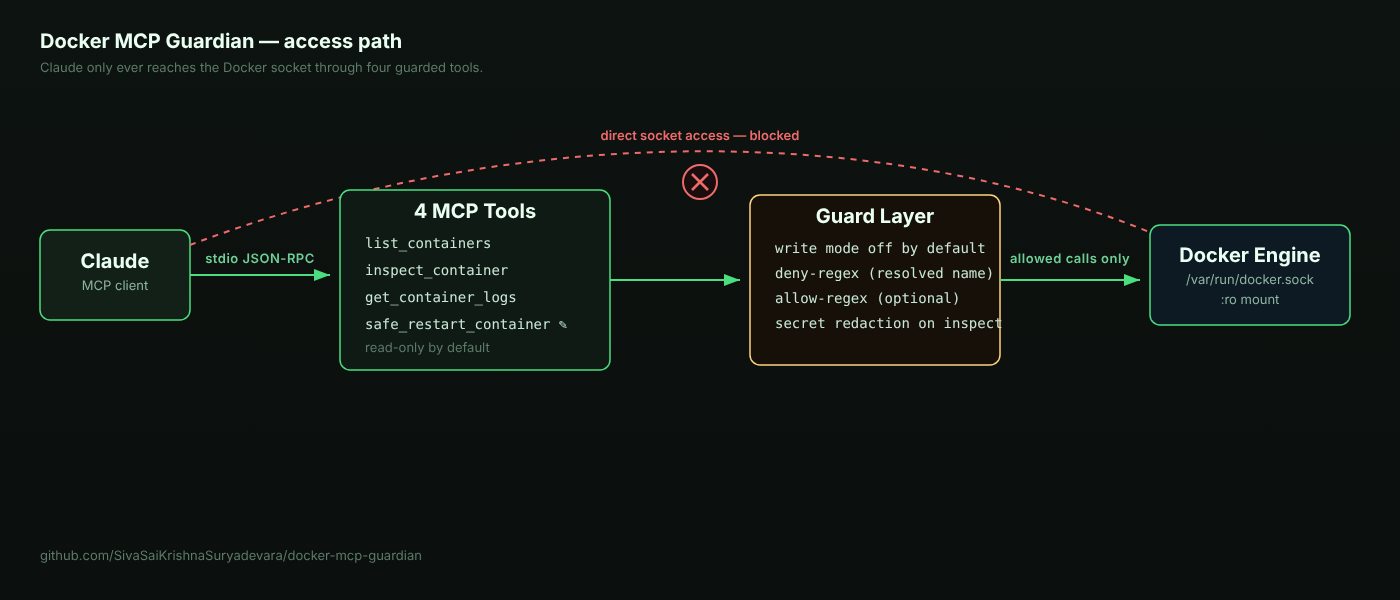
The GitHub repository SivaSaiKrishnaSuryadevara/docker-mcp-guardian houses the complete, tested codebase for a secure Docker MCP server. It's available at SivaSaiKrishnaSuryadevara/docker-mcp-guardian. A common setup mistake involves exposing the Docker socket with read-only permissions. However, this does not protect against unauthorized actions, as it only restricts file modifications, not the commands sent through the socket.
An attacker can still execute Docker API requests such as restarts, container creations, or deletions via a read-only socket.
When an LLM agent like Claude gains access to a Docker socket through an MCP server, the safeguards that would typically prevent malicious operations are bypassed. The only barrier between potentially harmful commands and execution is the tool layer, which could be inadequate. As a platform engineer, the author developed a Python MCP server on FastMCP to provide controlled access to Claude Desktop and Claude Code to containers without granting them destructive capabilities.
The server, written in Python, exposes four tools via stdio JSON-RPC: list_containers (reads), inspect_container (reads), get_container_logs (reads and scans for errors), and safe_restart_container (writes - only with a regex guard). The server is designed to be read-only by default, with only one write operation protected by a regex denylist and error scanning. It also redacts secrets from inspection results and prevents crashes when the Docker daemon is unavailable.
The server's implementation is deliberately minimal, with a focus on security and robustness. It uses FastMCP for the server API, adhering to a 1.x version to avoid breaking changes introduced in the 2.x version. Crucially, the server's logging is directed to stderr, eliminating print statements that could disrupt JSON-RPC communication.
Every tool returns structured error messages rather than exceptions, enabling Claude to understand and handle errors appropriately. The server also includes a DaemonUnavailable exception to handle cases where Docker is unreachable or unresponsive.
In summary, the server provides a secure interface for Claude to interact with Docker containers, ensuring that even read operations are carefully controlled to prevent unintended consequences.
Written by urgent.news from HackerNoon's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.