Hackers Use New ROMULUS ClickFix Platform to Deliver LegionLoader and Other Malware
Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as Legion Loader. According to Forescout Research - Vedere Labs, ROMULUS is akin to a malware delivery service that employs ClickFix-style lures on bogus landing pages to trick unsuspecting users into running malicious commands and infecting their own
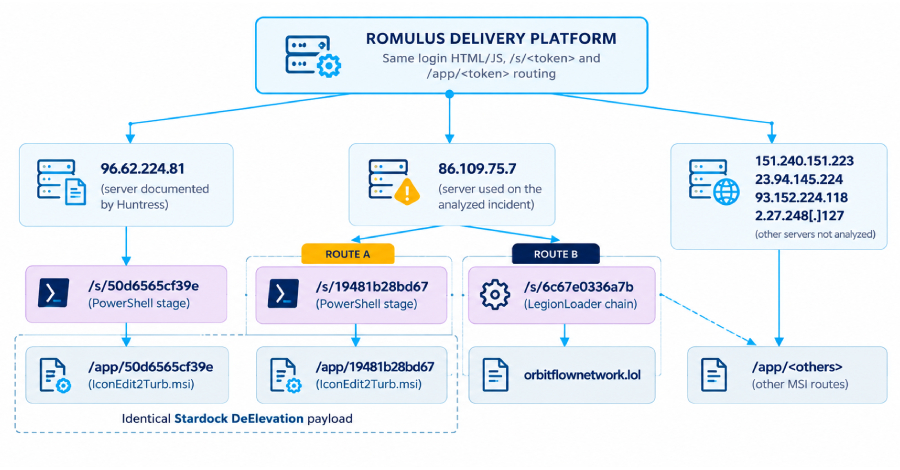
Cybersecurity experts have uncovered information about a new ClickFix platform named ROMULUS, which is being utilized to disseminate malware like Legion Loader. Vedere Labs, a research firm, explains that ROMULUS operates like a malware delivery service, employing deceptive lure tactics to coax users into executing malicious commands and infecting their devices.
Romige, a security researcher, suggests that ROMULUS might be a privately managed panel, a commercial cybercrime delivery service, an affiliate network, or simply copied software among operators. The cybersecurity company has identified six IP addresses running ROMULUS, including 96.62.224[.]81 and 86.109.75[.]7, which have been linked to campaigns using malicious ChatGPT Custom GPTs and ClickFix lure tactics.
The malware delivered through this platform can also include Legion Loader, also known as Satacom downloader, CurlyGate, and RobotDropper. While the identity of the ROMULUS platform's operators remains unknown, it bears no resemblance to RomulusLoader, a malware family tied to the China-aligned Silver Fox threat actor. ROMULUS exposes two endpoints responsible for downloading a PowerShell staging script, which determines the subsequent payload, whether it's a trojanized MSI installer or an encrypted archive containing Legion Loader.
The loader communicates with a remote server to download further payloads. This revelation highlights how ClickFix is transforming from a social engineering technique into a potent malware delivery mechanism. To counter this threat, it is crucial to monitor for suspicious PowerShell commands and DLL sideloading activities.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.