The 3-2-1 backup rule has a glaring caveat that ransomware exploits perfectly
A backup that's always plugged in is just another target.
The 3-2-1 backup rule, a widely recognized strategy for safeguarding data, has a significant flaw that ransomware exploits. This rule suggests having three copies of files on two different media types, with one backup stored off-site. However, there is a critical caveat that is often overlooked. Even when following this guideline, if ransomware (or similar malicious software) infects a single copy, it can potentially encrypt all copies.
To address this issue, implementing a cold storage backup is a simple and cost-effective solution. I discovered this limitation when researching ransomware that specifically targets Network-Attached Storage (NAS) systems. These types of ransomware not only target the main drive but also spread to other connected storage devices, including backup drives and shared folders, encrypting files across the board.
The only way a backup can protect you in this situation is if it is physically disconnected from the computer and inaccessible.
In my setup, I had a backup drive connected to the same system as my primary storage, using an rsync script to synchronize changes nightly. While this setup protects against hardware failure and corrupted files, it leaves my data vulnerable to ransomware if my system is compromised. Mounting my offsite backup as a mapped network drive further increases the risk since it provides a direct gateway for malicious software to access additional copies of my files.
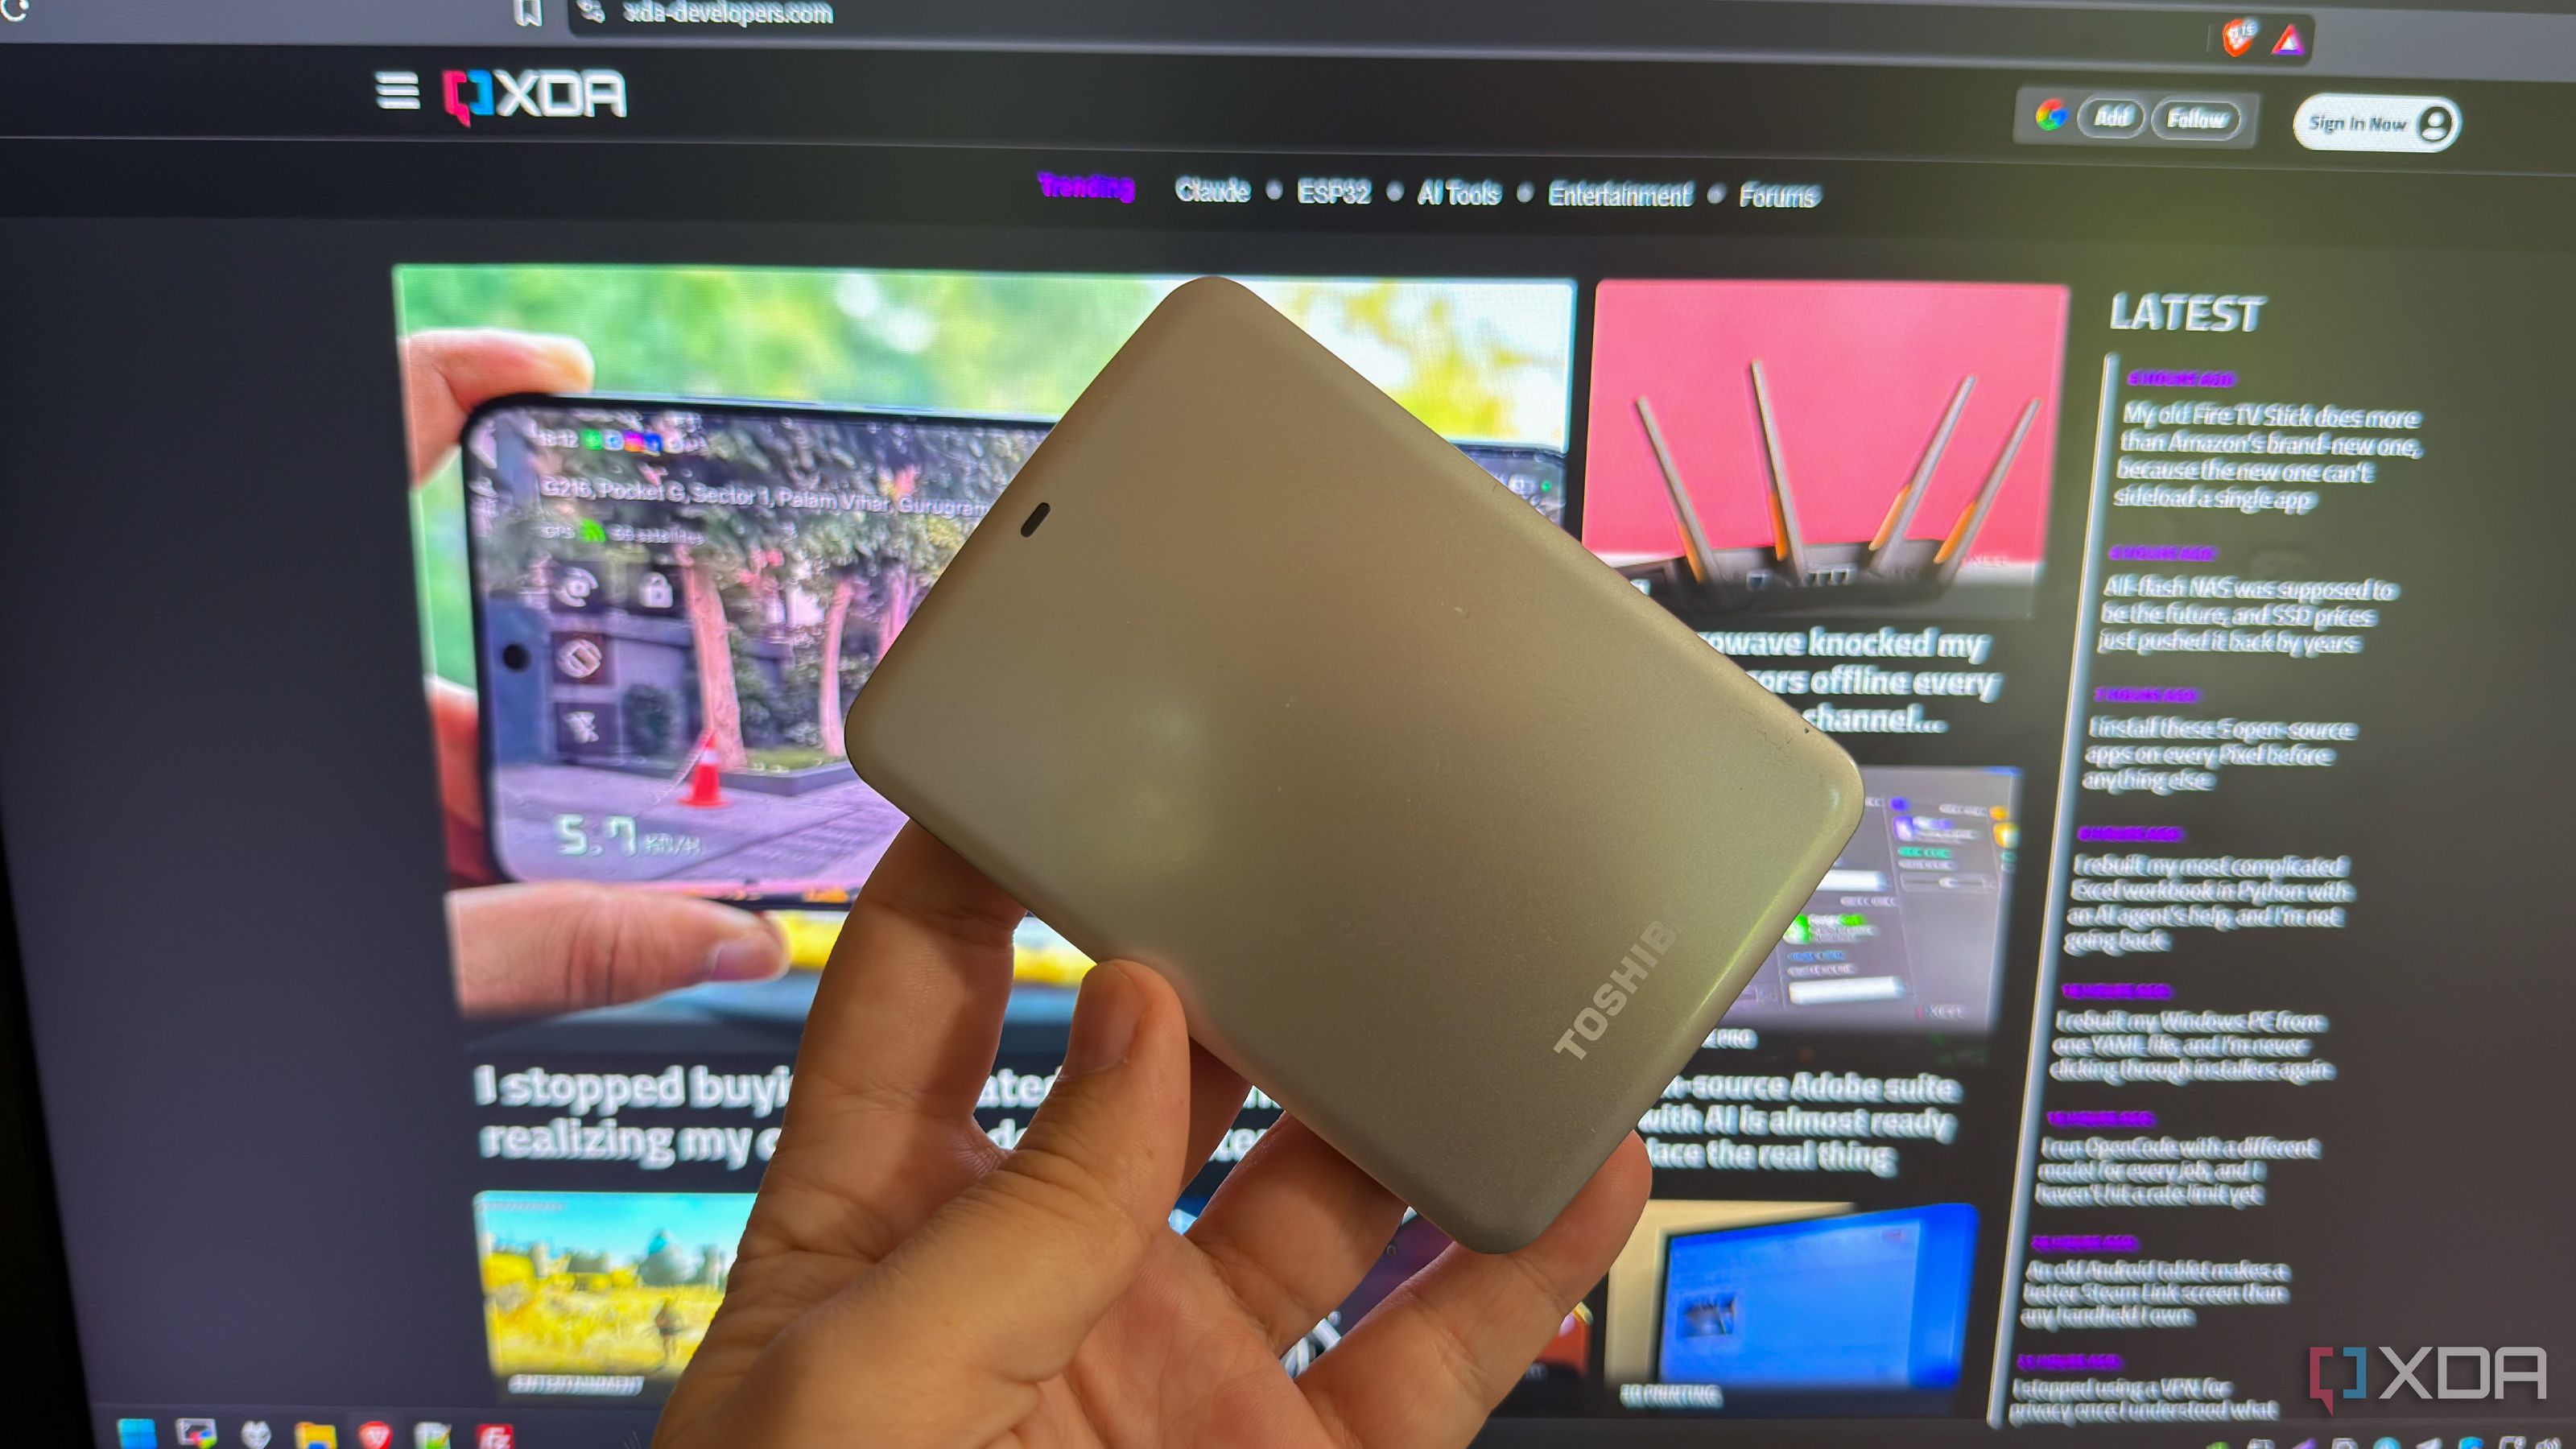
The simplest way to protect against ransomware is by using an external drive that remains unplugged and disconnected from the network when not in use. This involves plugging in the drive once a week or so, running a backup using an rsync command, and then disconnecting it again. This uncomplicated method provides an extra layer of protection, ensuring that only one copy of your files remains vulnerable.
While this approach might result in a few days of file changes being lost during recovery, it offers peace of mind by eliminating the need for complex software configurations that could be vulnerable to attack. I currently use this method and have taken standard precautions online to minimize the risk of a ransomware attack.
Written by urgent.news from XDA Developers's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.