Ledger to review sales and anti-tamper policies after $93 million hardware-wallet supply chain attack
Ledger is reviewing chain-of-custody practices and anti-tamper protections after modified hardware wallets sold through a third party were allegedly fitted with LTE implants that captured recovery phrases and enabled $93 million in crypto theft.
Ledger is conducting a thorough review of its sales practices and device protection measures following a supply chain attack that led to the theft of $93 million from user cryptocurrency wallets. The company's Chief Technical Officer, Charles Guillemet, confirmed that the Ledger is examining anti-tampering protections on its devices in the wake of the incident.
Users with tampered devices are advised to contact Ledger support for guidance on returning the devices for examination. The CEO, Pascal Gauthier, emphasized the importance of reviewing the company's controls around sales and reseller relationships. The attack was first detected on October 9, when multiple wallets lost funds simultaneously across Bitcoin, Ethereum, and Tron networks.
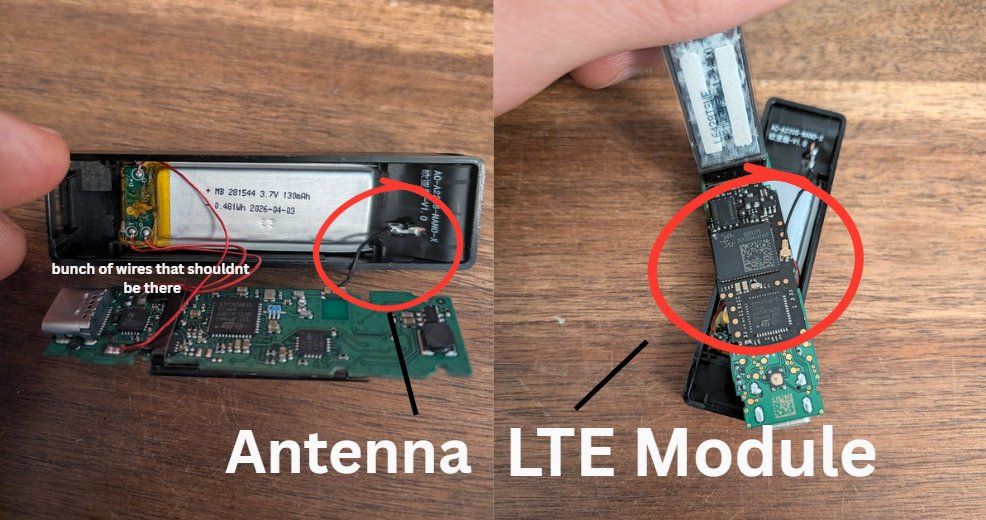
Further investigation revealed that the attackers inserted a hardware implant with a cellular module into new devices at an undisclosed point in the supply chain. This implant recorded recovery seed phrases as users entered them during device setup and transmitted the unencrypted information to the attackers via LTE networks. Ledger's internal systems and direct sales channels remain secure, but the company is advising users to avoid devices purchased from third-party resellers and to transfer funds to secure wallets while investigations continue.
Ledger is also revising its vendor verification processes to ensure stricter supply chain controls and collaboration with researchers and vendors to assess current practices.
Written by urgent.news from Tom's Hardware's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.