Broadcom adds hypervisor protection to VMware
Citing the growing speed and volume of artificial intelligence-enabled attacks, Broadcom Inc. today introduced VMware HyperArmor, software that protects the hypervisor underlying VMware Cloud Foundation and gives administrators more time to test and deploy security patches. Announced at VMware Explore in Frankfurt, HyperArmor targets two common routes into virtualized infrastructure: stolen root…
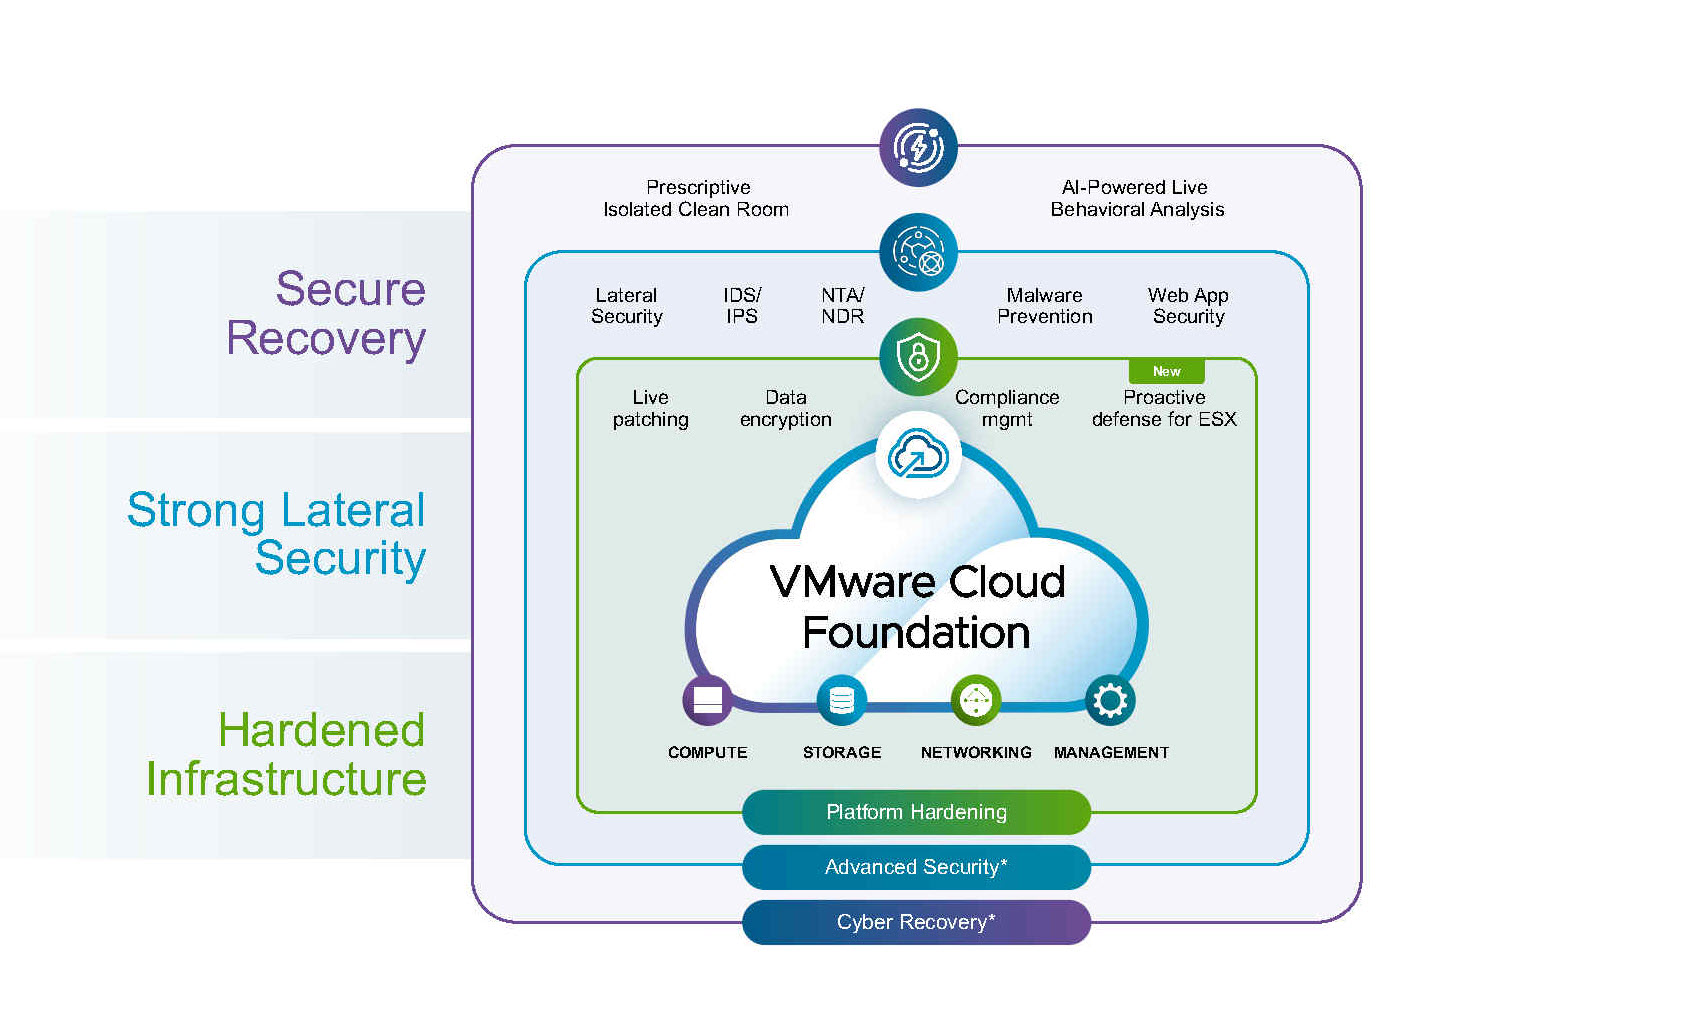
Broadcom unveiled VMware HyperArmor at VMware Explore in Frankfurt, a software solution aimed at safeguarding the hypervisor supporting VMware Cloud Foundation. The product addresses the increasing speed and volume of AI-driven attacks by providing additional time to test and deploy security patches. It combats two primary vulnerabilities: stolen root credentials and unpatched vulnerabilities.
HyperArmor incorporates host-level virtual patching, executable program and script controls, and multifactor authentication for remote access to VMware ESX hosts. Broadcom's chief marketing officer, Prashanth Shenoy, highlighted the urgency of the issue, stating that enterprises cannot patch at a rate matching the acceleration of attacks.
HyperArmor operates at the ESX layer, which directly supports virtual machines, offering host-level virtual patching that detects and blocks malicious actions without altering the underlying infrastructure software. This feature eliminates the need for host reboots or software upgrades. Eric Chen, a distinguished engineer at Broadcom, emphasized that the protection offers administrators breathing room while still emphasizing the importance of patching their systems.
The software establishes a baseline of permitted activity on ESX hosts, which have a limited set of processes. It automatically inventories existing scripts, requiring administrators' approval for new ones. Unauthorized executables and scripts are blocked by default. Unlike general-purpose application protections, HyperArmor directly enforces restrictions within the host due to its knowledge of the allowed processes.
The product continuously monitors host processes and behavior with minimal performance impact, without requiring security agents inside individual guest virtual machines. Additionally, HyperArmor integrates multifactor authentication into the ESX Secure Shell login process, requiring users to provide standard SSH credentials and complete a time-based one-time password challenge.
This additional layer of security prevents unauthorized access even with a root password. HyperArmor complements VMware vDefend, which provides network and workload-level security through microsegmentation, traffic inspection, and network-level virtual patching. VMware Avi Load Balancer protects web applications and APIs. Shenoy explained that HyperArmor operates at the ESX host layer, while vDefend functions at the network and workload layer, along with web application firewall protection by Avi.
Currently supporting ESX 8.x and later releases, HyperArmor extends protection to customers upgrading to newer VMware platforms. The software can be purchased directly from Broadcom or through its partners and resellers, utilizing the same sales channels available for VMware Cloud Foundation. Pricing details were not disclosed.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.