Two characters open up a world of typosquatting opportunities in Chromium browsers
Attackers abusing rare Cyrillic and Latin letters to impersonate popular websites
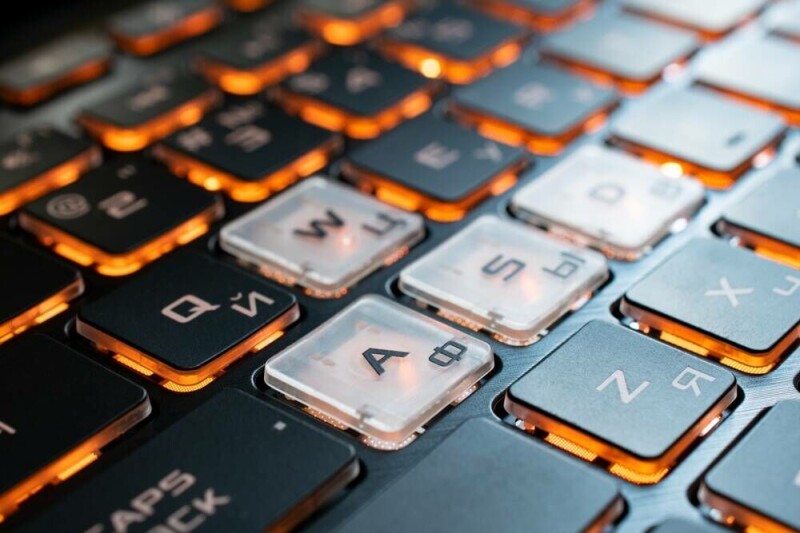
Two characters can be exploited by cyber-criminals to launch typosquatting attacks against Chromium browsers, researchers have warned. These characters, ө and ƙ, appear visually similar to common letters like 'e', 'o', 'i' and 'k'. Unlike ASCII-compliant characters, these glyphs are not filtered out, providing attackers with new ways to deceive users.
The researchers identified 20 lookalike domain names that can bypass Chromium's security measures. Unlike traditional URLs, these domains appear genuine in Unicode, but trigger security warnings that reveal their true identity in Punycode. Despite Chromium's multiple security layers, including checks for common spoofing methods and comparison to popular websites, these domains can still slip through.
Users may receive warnings, but only if the imitation domain differs by a single character or an adjacent swap. Email clients are also vulnerable to similar attacks, displaying domains without the same level of scrutiny.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.