Length Extension Attacks: How Hash-Based Signatures Can Be Forged
Learn how Length Extension Attacks work by exploring MD5 internals, message padding, internal states, and how attackers can extend signed data without knowing t
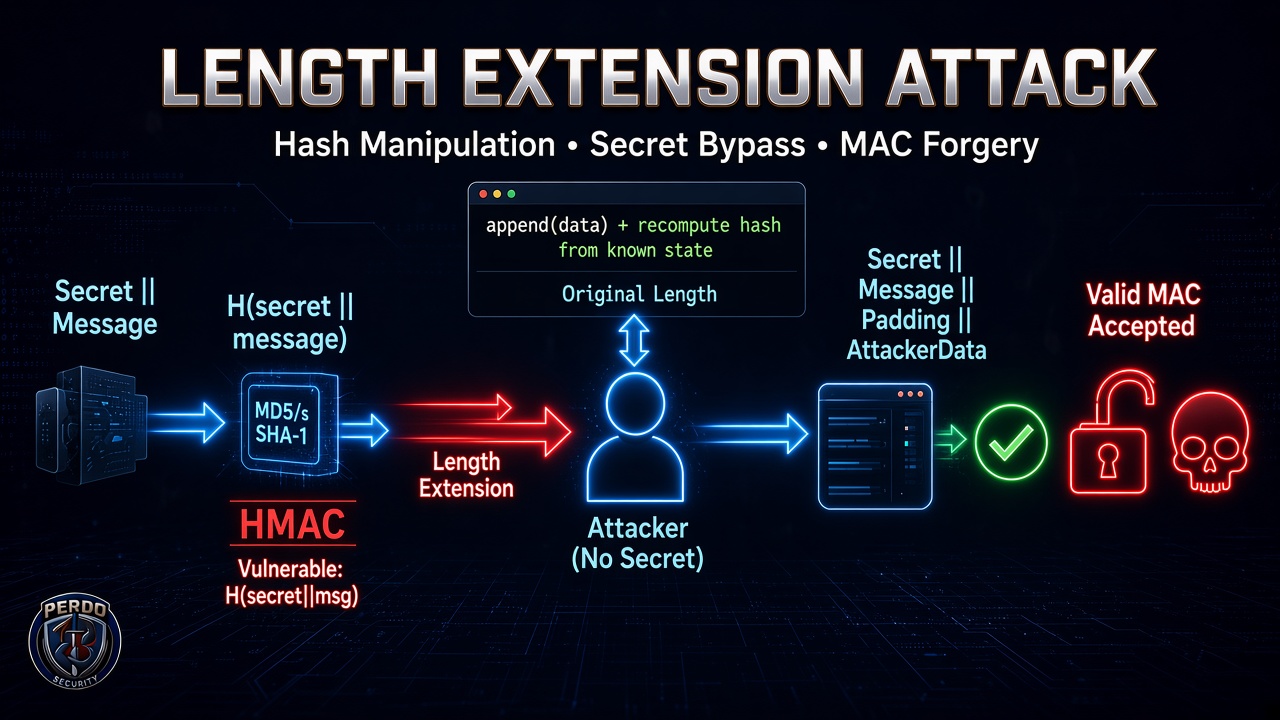
Length extension attacks can be used to forge hash-based signatures, making it possible to alter a message without knowing the associated secret and still have it appear legitimate. This occurs due to the construction of the hash algorithm, which allows such attacks to happen. In this article, we will explore the concept of length extension attacks and how they can be leveraged to forge hash-based signatures.
Written by urgent.news from HackerNoon's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.