Urgent.News

What's breaking now, across thousands of outlets.

Tech

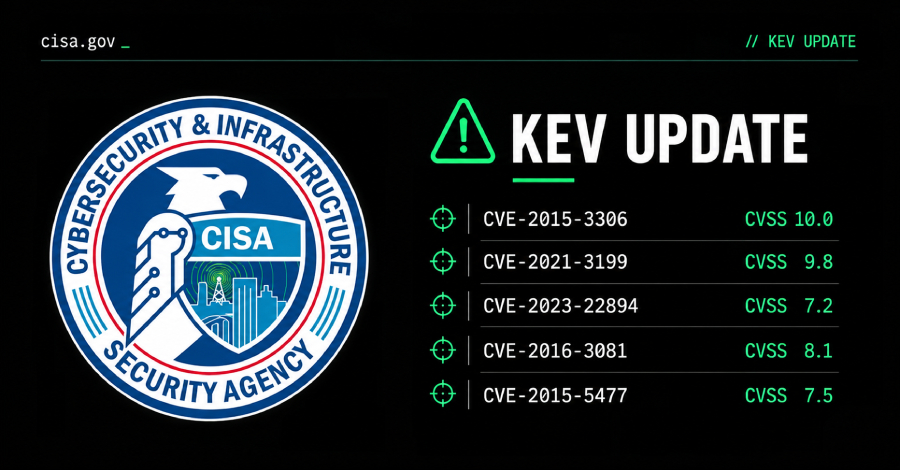
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below - CVE-2015-3306 (CVSS score: 10.0) - An improper access control vulnerability in ProFTPD that could allow
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

Put a Meter in the Take-Home

You open the submission on a Monday and the README still has a public URL in it. The health check answers. A debug header sits in the response, cheerful and uninvited.

  • Candidate must ship a small change within a 90-minute time budget
  • Include GET /status in a small HTTP service returning JSON with ok:true and rev:set
  • Submit diff, statusnote.md documenting decisions, and teardown proof without secrets

More from Friday 9 October →