CelcomDigi Launches Protect+ With AppleCare Services From RM50/Month
CelcomDigi has introduced Protect+ with AppleCare Services, a multi-device protection plan for selected Apple devices. The plan allows customers to cover a single device or bundle up to three additional eligible devices under one monthly subscription. The new plans start from RM50 per month when paired with the purchase of selected new iPhone models through […] The post CelcomDigi Launches…
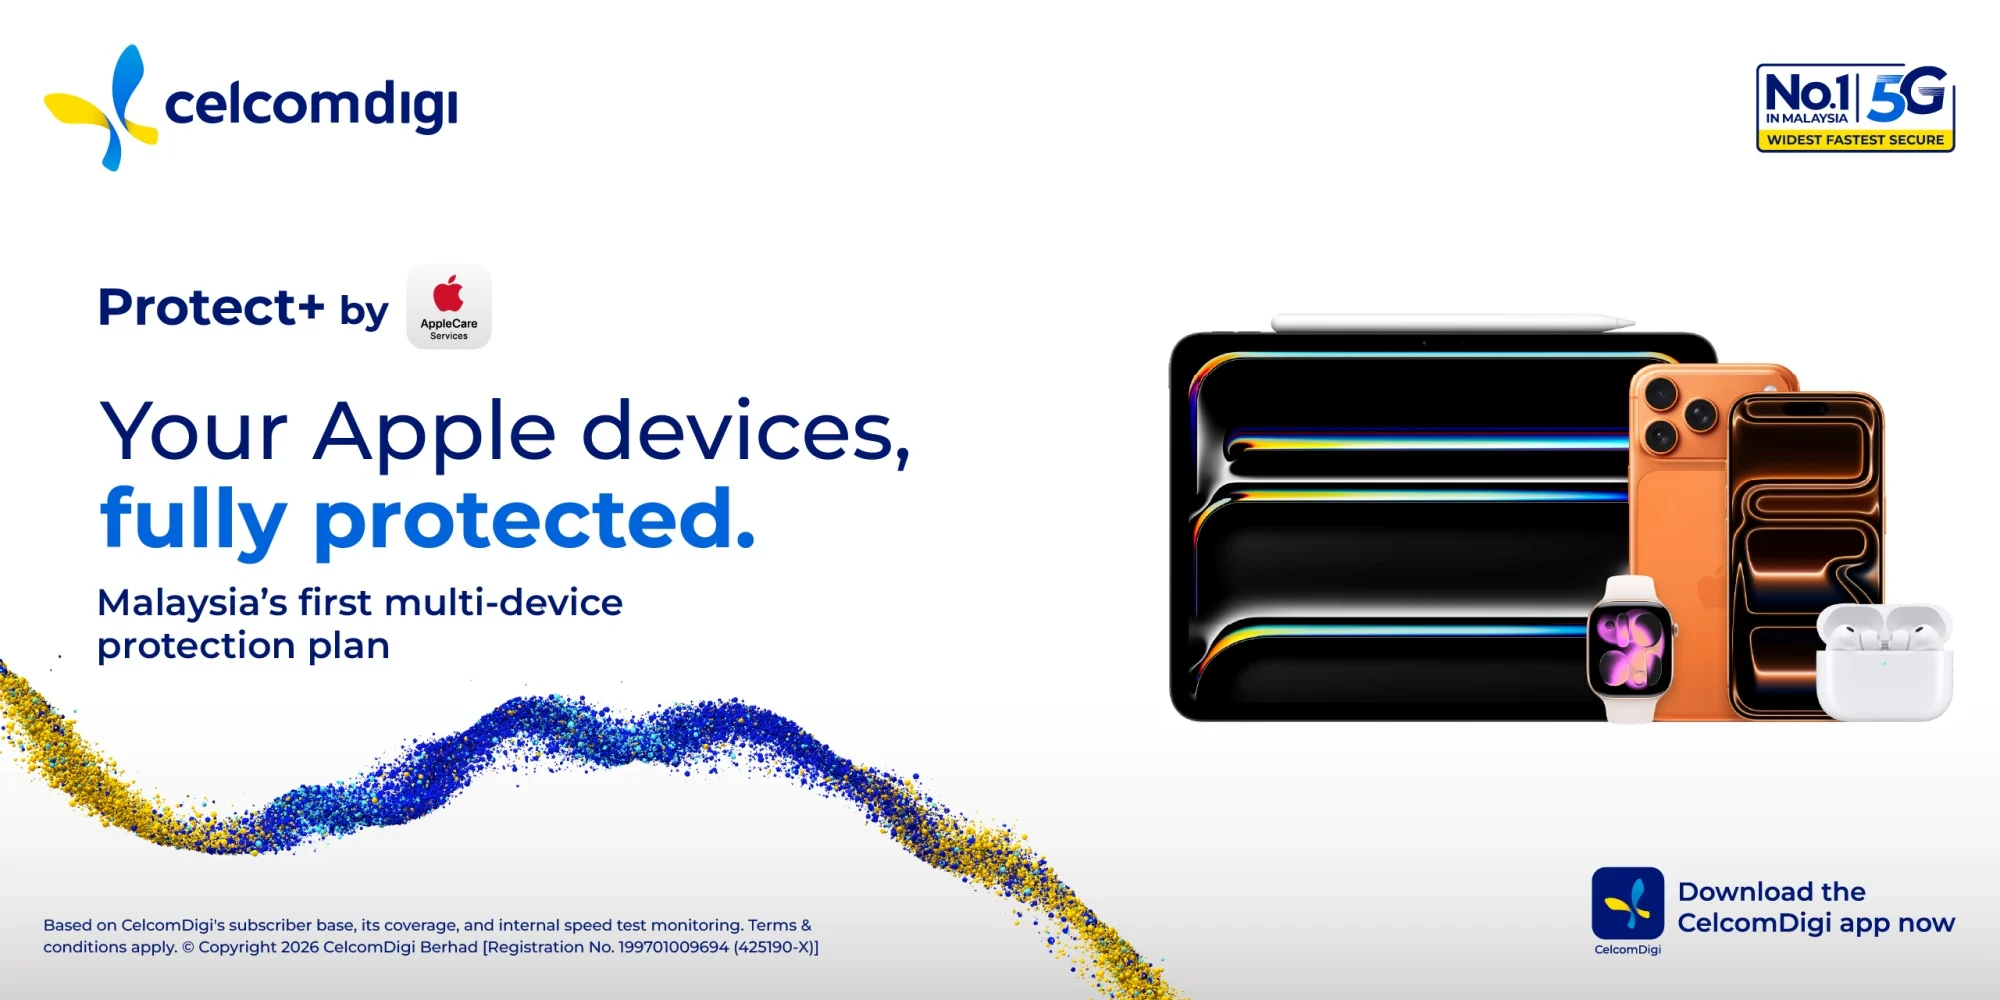
CelcomDigi has launched a new protection plan called Protect+ with AppleCare Services. This multi-device plan offers coverage for selected Apple devices, starting at RM50 per month when combined with the purchase of specific new iPhone models through CelcomDigi's Easy360 device installment programme. The plan can also be purchased separately through CelcomDigi's website, online stores, and retail outlets across Malaysia.
Protect+ with AppleCare Services provides coverage for accidental damage like drops and spills, along with 24/7 priority assistance from Apple experts and Apple-certified repairs. Battery replacement is also covered when a device's battery capacity falls below a certain threshold. For iPhones, the plan includes protection against theft and loss, with a like-for-like replacement if the device is no longer in the customer's possession. Additionally, customers can swap eligible devices while enrolled in the plan.
AppleCare Services have been available in Malaysia for some time, offering protection against accidental damage and access to technical support and certified repairs for supported Apple products. CelcomDigi's new offering combines this with multi-device protection and extra theft and loss coverage for iPhones. The Protect+ plan is currently available through CelcomDigi's sales channels nationwide. For more information, visit the official Protect+ page.
Written by urgent.news from Lowyat.NET's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.