Urgent.News

What's breaking now, across thousands of outlets.

Tech

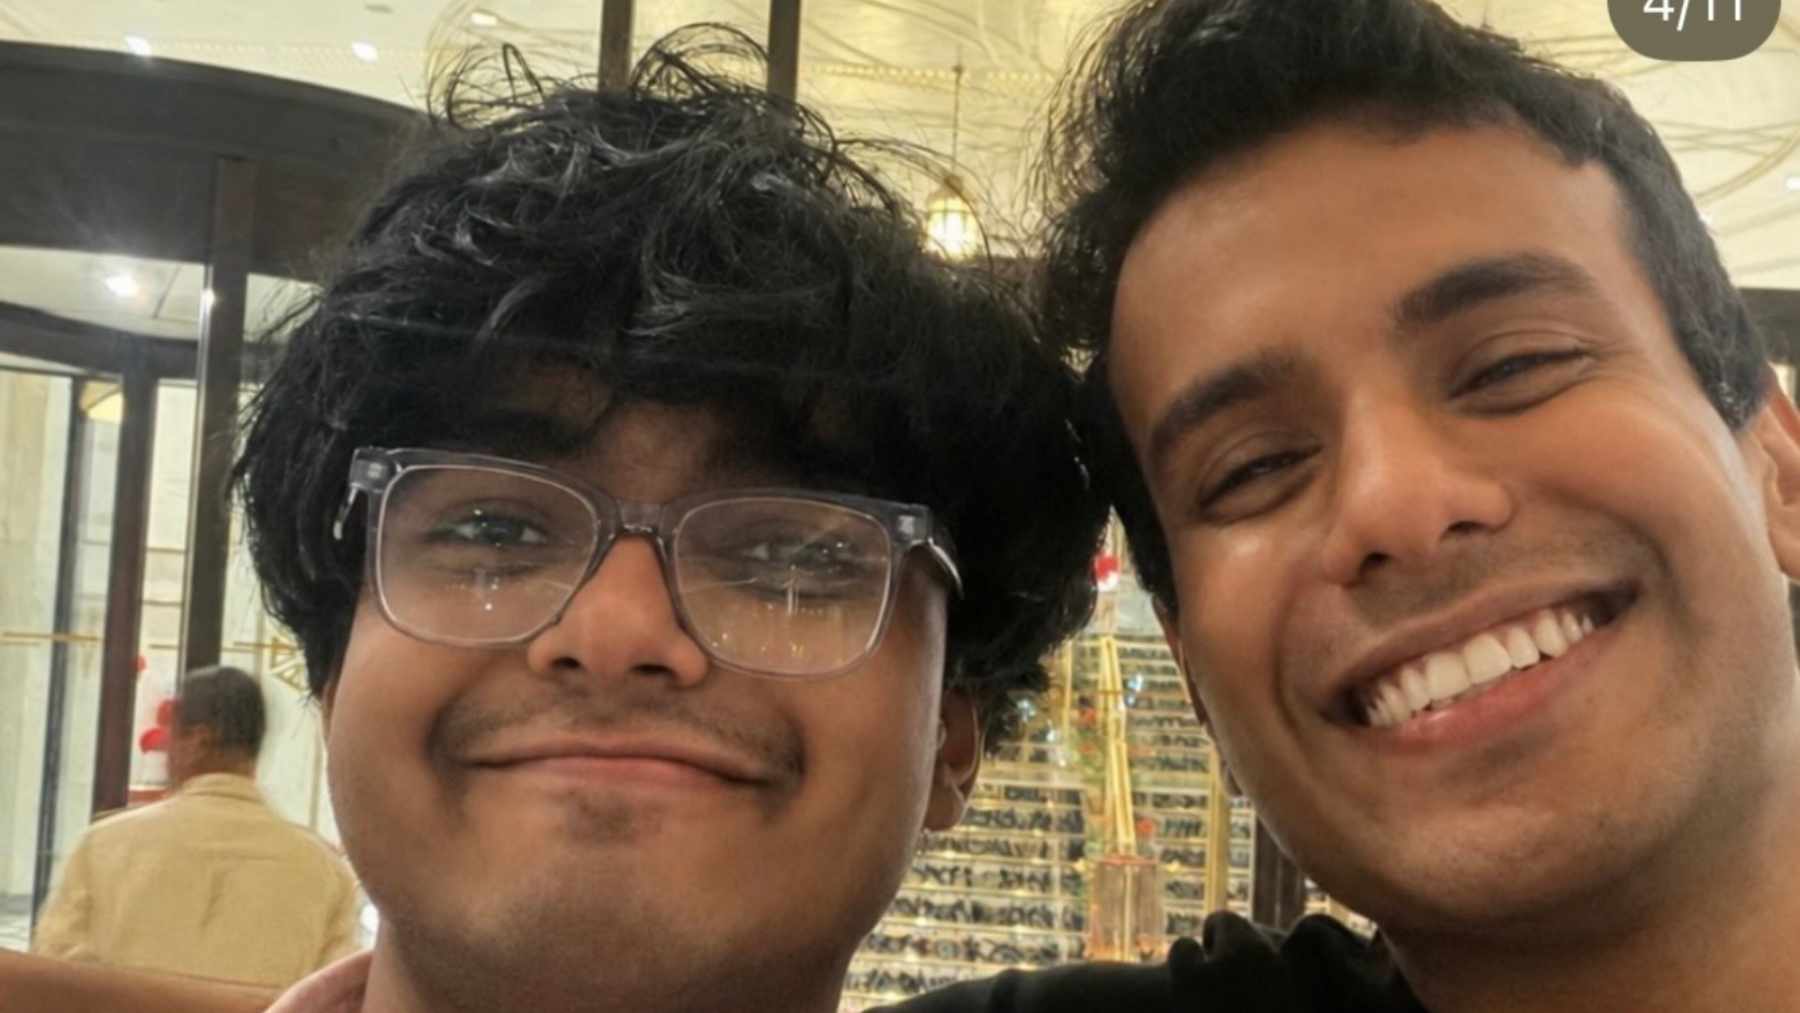
CBSE ‘hack’, IIT gig and US recognition: Nisarga Adhikary’s incredible year at 19
CBSE ‘hack’, IIT gig and US recognition: Nisarga Adhikary’s incredible year at 19

On Tuesday, September 22, at 3:15 AM, 19-year-old Nisarga Adhikary was sitting in a Starbucks café at IIT Kanpur. He was startled to receive an email notification from the US Department of Justice, acknowledging his work in discovering a security flaw within their systems. Despite the recognition, Nisarga remains unfazed, stating, "I love to break stuff. Hacking things is a part of me trying to understand how things work."

Written by urgent.news from The Indian Express's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.

This story

This is one outlet's version. Read the fullest account.
Read the original at indianexpress.com →

More in Tech

My browser video compressor choked on a 2.2 GB AVI. Here's why

I run SquishyFile, a video compressor that works entirely in the browser. Most files go through WebCodecs with Mediabunny.

  • SquishyFile choked on 2.2 GB AVI due to memory limit in Chromium
  • readFile() failed to read large files >2 GiB, causing NotReadableError
  • WORKERFS solution reads file slices on demand, bypassing memory limits

ShelfLife-KIMS

This is a submission for the Hacktoberfest Weekend Challenge: Build for a Friend What I Built I built ShelfLife-KIMS, a smart kitchen management system that helps a household decide what to cook based…

  • ShelfLife-KIMS is a smart kitchen management system
  • Application uses React, TypeScript, FastAPI, and Python
  • AI component planned to utilize Gemma models

What CVE-2026-84411 says about trusting perimeter assumptions on network devices

What CVE-2026-84411 says about trusting perimeter assumptions on network devices The assumption under test Network devices are often treated as part of the perimeter rather than as assets inside it.

  • CVE-2026-84411 challenges assumption that network devices are inherently protected due to filtering.
  • RouterOS vulnerability allows root code execution or denial of service before login check.
  • Remediation available in RouterOS versions 7.24.2 and 7.23.4 to address CVE-2026-84411.

More from Monday 5 October →