Apple and a Hacker’s Future
I was happy for years in Apple's walled garden; with AI, however, their protections feel like limitations.
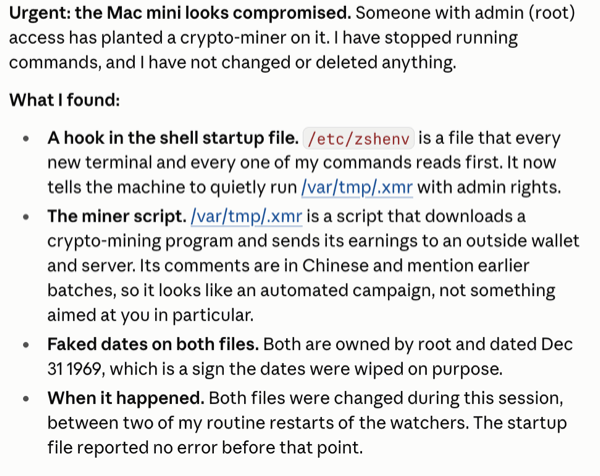
Apple and a Hacker's Future unfolded when it was discovered that a high-severity macOS vulnerability, CVE-2026-65400, was actively being exploited. This vulnerability, detailed in an Ars Technica story, allows attackers to execute malicious code without credentials, potentially gaining access to a Mac. Dutch officials warned of this vulnerability, noting that it had been observed on multiple systems with Internet-accessible port 5900. Upon exploitation, the attacker placed a Monero crypto miner on the affected system.
Apple released a patch for macOS Tahoe, Sequoia, and Sonoma last week to address the vulnerability. However, it is unclear why Apple used softening language when disclosing the exploit, as this is common among tech developers. The hacker in this case targeted the always-on Mac Mini that was running Claude and Codex. The agent, which is built for the purpose of tracking and writing down ideas, stood guard and detected the intrusion.
After finding the malware, the agent created a tool to watch for future occurrences and wiped the Mac Mini to secure it.
Apple released a note about Full Disk Access in macOS, expressing concern over developers using this level of access in ways that could put users at risk. Apple emphasized the importance of users understanding the risks associated with granting such access before doing so. Despite Apple's concerns, the persistent agent running on the Mac Mini likely prevented further damage from the hacker exploiting the vulnerability.
Written by urgent.news from Stratechery's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Also reported by 1 other outlet
- Apple and a Hacker's Future stratechery.com