Teen suspected of running KillSec ransomware group as cops seize servers, arrest three
Operation KillSwitch takes over leak site holding at least 110 TB of stolen data
A 16-year-old suspect is believed to have led the KillSec ransomware group, which orchestrated around 1,000 global attacks. Authorities executed an international operation on Thursday, seizing the group's infrastructure and making three arrests. The operation, led by Germany, replaced the group's leak site with a police notice. Europol confirmed the 16-year-old as the suspected main operator, though they did not explicitly state this individual was arrested.
Spanish police arrested a minor, a Romanian national, but did not link this to the 16-year-old. The U.S. Department of Justice (DoJ) announced a Dutch national, Fouad Eltibrizi, was arrested by UK police and charged with cybercrimes in the U.S. and Puerto Rico. Eltibrizi is the only suspect publicly named. Romanian police stated a 24-year-old contributed to the group's formation in October 2023, though it's unclear if the person was arrested.
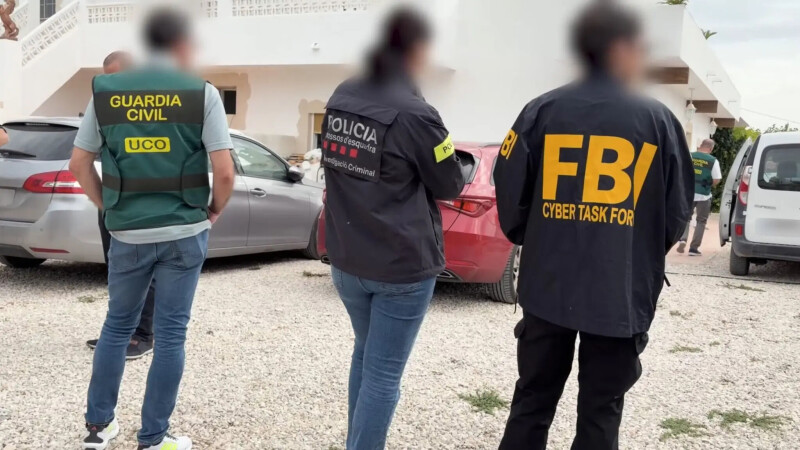
A Romanian national in his twenties was also arrested on suspicion of acting as a KillSec affiliate. A suspected developer, who turned 18 in August, was a minor during some of the alleged offenses. Spanish authorities mentioned a woman under investigation but not arrested. The coordinated raids on September 30 involved ten European and U.S. agencies, targeting eight properties in Greece, Romania, Spain, and the UK.
Authorities secured over 110 TB of data to prevent unauthorized access. They are examining seized devices and data to identify victims, attacks, suspects, and trace the group's financial activities. Police have taken control of five central servers used for managing the group's operations and storing victim data. Security firms Bitdefender and Group-IB supported the investigation.
KillSec employs double extortion, encrypting victims' systems and threatening to publish stolen data unless payment is made. The group recently ranked among the top 10 ransomware groups globally, primarily targeting financial services, healthcare organizations, government entities, and large enterprises. Group-IB CEO Dmitry Volkov stated that identifying and apprehending the people behind KillSec is crucial in turning a takedown from a pause into an end.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.