Teen suspected of running KillSec ransomware group as cops seize servers, arrest three
Operation KillSwitch takes over leak site holding at least 110 TB of stolen data
A 16-year-old suspect was reportedly the primary operator of the KillSec ransomware group, responsible for approximately 1,000 suspected cyberattacks globally. On Thursday, an international operation led by Germany dismantled the group's infrastructure and made three preliminary arrests. Europol confirmed the 16-year-old as the suspected main operator, though it did not explicitly claim a warrant for their arrest.
Spanish authorities reported the arrest of a minor, a Romanian national, but did not explicitly link this arrest to the 16-year-old. The US Department of Justice announced the arrest of a Dutch national, Fouad Eltibrizi, who is charged with alleged cybercrimes in the US and Puerto Rico and faces extradition. Eltibrizi is the sole suspect named publicly by authorities.
Romanian police stated that a 24-year-old contributed to the group's establishment in October 2023, while other sources suggest formation in 2024. Authorities did not disclose whether this individual was arrested. Additionally, a Romanian national in his twenties was apprehended in Romania on suspicion of being a KillSec affiliate.
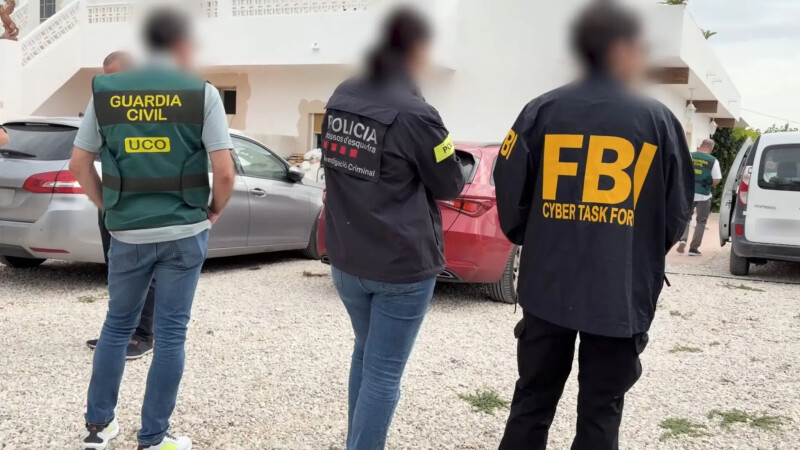
Europol identified another minor who turned 18 in August and was a minor during some alleged offenses. Spanish police mentioned an unidentified woman under investigation but not arrested. The coordinated raids occurred on September 30, following inquiries that began in early 2025. Ten European and US police agencies participated, with raids conducted at eight locations across Greece, Romania, Spain, and the UK.
Spanish authorities said they searched a home and an office in an Alicante hotel, while Romanian police searched four residences. Neither Greece nor the UK provided further details on their involvement. Authorities secured at least 110 terabytes of data to prevent unauthorized access to KillSec's leak site. Investigators are studying seized devices and data to identify victims, attacks, suspects, and trace the group's criminal income.
The operation resulted in the seizure of five central servers managing the group's activities and storing victims' data. Security firms Bitdefender and Group-IB assisted the investigation. KillSec employs double extortion, encrypting victims' systems and threatening to release stolen data unless payment is made. Group-IB included KillSec in its 2025 top 10 ransomware groups ranking for APAC, LATAM, and the Middle East.
The company's researchers noted that KillSec typically targets financial services, healthcare organizations, government entities, and large enterprises. KillSec also offered stolen data for sale at prices between $5,000 and $500,000. Group-IB CEO Dmitry Volkov stated that servers can be replaced in weeks, but the individuals who build the platform and approve each attack cannot.
Identifying and supporting law enforcement in apprehending these individuals turns a takedown from a pause into an end. KillSec first launched with a Windows encryptor, later adding a version capable of encrypting VMware ESXi hosts, deleting data, shutting down VMs, and removing recovery points.
Written by urgent.news from The Register Science's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.