Urgent.News

What's breaking now, across thousands of outlets.

Tech

Murata Begins Mass Production of World’s Smallest 0201-inch Size Three-Terminal Low-ESL MLCCs

Murata Manufacturing Co., Ltd. (TOKYO: 6981) (ISIN: JP3914400001) has begun mass production of the LLD series, the world’s smallest* three-terminal low-equivalent series inductance (ESL) multilayer ceramic capacitors (MLCC).
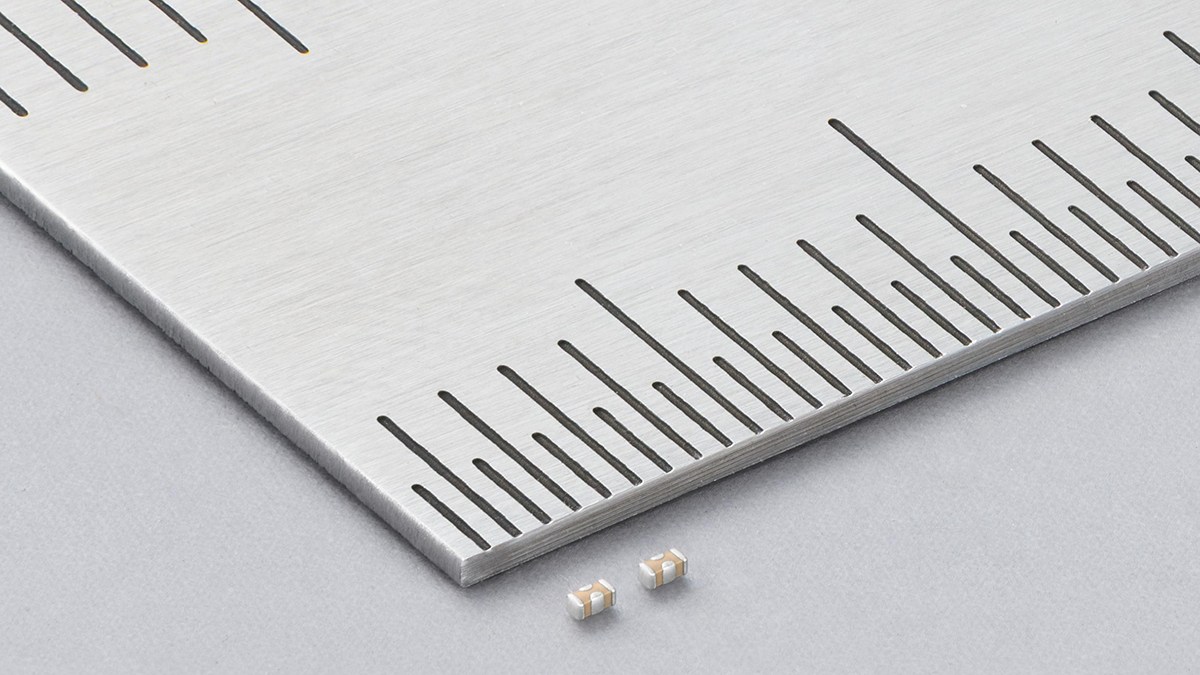
Murata Begins Mass Production of World’s Smallest 0201-inch Size Three-Terminal Low-ESL MLCCs

We haven't written up this one. ITWeb has the full story — the link below goes straight to it.

This story

This is one outlet's version. Read the fullest account.
Read the original at itweb.co.za →

More in Tech

I built a referral leaderboard that ignores page views. Here's the credit model.

Most referral leaderboards count the wrong thing. They count clicks or visits, and the moment a visit is worth something, somebody points a traffic tool at it and the board is over.

  • ViralRefer's referral leaderboard ignores page views, countering manipulable clicks.
  • Users earn credits by friends performing the same action, not just viewing the link.
  • The system is fair, with 26 language variants and Cloudflare Pages hosting.

Why coding agents should work on a copy of your repo

A coding agent should work on its own copy of your repository, on its own branch, so that nothing it does touches your working files until you have read the diff and merged it yourself.

  • Coding agents should work on a copy of your repository on a separate branch.
  • Git worktrees enable multiple working directories within a single repository for agent tasks.
  • Review agent changes with git diff before merging and removing the worktree directory.

소스 인식 검증(ProvenanceGuard)이 1인 개발자에게 의미하는 것

왜 소스 인식 검증이 중요한가 LLM 에이전트가 여러 검색·데이터베이스 도구를 호출해 답변을 만들면, "사실 여부"만 검증하는 기존 방법으로는 충분하지 않다. 답변이 어느 소스에서 온지를 잘못 연결하면, 의료 기록이나 고객 계정처럼 민감한 데이터에서 큰 위험이 된다.

  • ProvenanceGuard verifies information sources for LLM agents
  • Developed by Hugging Face to prevent risks with sensitive data
  • Requires five steps: claim division, source matching, support checking

CVE-2026-9586: One XML Field in Sangoma Switchvox Reaches the PostgreSQL Backend

CVE-2026-9586: One XML Field in Sangoma Switchvox Reaches the PostgreSQL Backend A phone provisioning endpoint that trusts what it is told Sangoma Switchvox is a business phone system that provisions…

  • Sangoma Switchvox phone system vulnerable to SQL injection.
  • Unauthenticated attacker can execute arbitrary SQL statements.
  • Fixed in Switchvox 8.4.0.2, released July 2026.

More from Wednesday 30 September →