Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across a codebase at no cost. Dan Ochs, director of AI solutions consulting for Blitzy, said the provider’s Proactive Insights platform uses multiple artificial […]
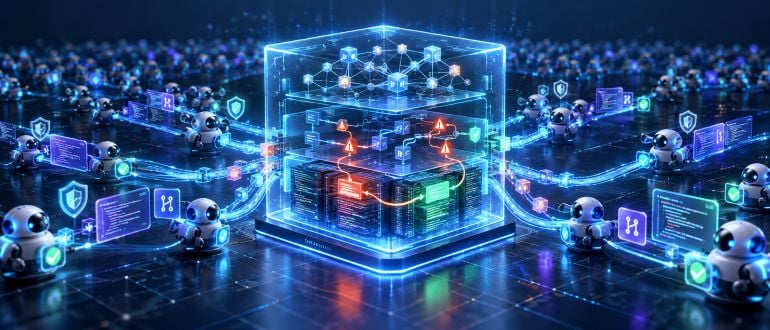
Blitzy has unveiled a sandbox platform enabling DevOps teams to reverse-engineer up to one million lines of code, generate 25,000 lines of tested end-to-end code, and identify security vulnerabilities without cost. Dan Ochs, director of AI solutions consulting for Blitzy, explained that the Proactive Insights platform utilizes multiple AI models from Anthropic, OpenAI, and Google, AI agents, and a knowledge graph to uncover vulnerabilities, assess their reachability, assess fixability, and generate remediation code.
Blitzy constructs a knowledge graph encompassing architecture, dependencies, business logic, and data flows, which is queryable and continually updated as the codebase evolves. Known and unidentified vulnerabilities are traced through their execution paths, cross-referenced with dependencies, and verified for remediation. Thousands of AI agents then collaborate to build, validate, and test code in parallel, with output presented as prioritized pull requests by risk level for review by human software engineers.
Blitzy ensures no code is used to train AI models and that data remains encrypted during transmission and storage to meet compliance requirements. The company is offering the sandbox environment at no cost to facilitate broader adoption among DevSecOps teams, as many are now prioritizing vulnerability discovery by cybercriminals.
DevSecOps teams face a race against time to identify and remediate potentially thousands of vulnerabilities before they are exploited. Ochs emphasized that DevSecOps teams must rely increasingly on AI platforms capable of understanding how a codebase is constructed at scale. While many DevOps teams utilize AI for code generation, the next step is embedding AI into DevSecOps workflows for vulnerability discovery, validation, and remediation.
The challenge lies in ensuring the AI platform comprehends the codebase to generate executable code in production environments. Software engineers are increasingly becoming managers of AI agents assigned specific tasks to autonomously complete. DevOps teams will adopt this shift at different paces, but with the looming flood of vulnerabilities, now may be the optimal time to begin utilizing such capabilities.
Written by urgent.news from DevOps.com's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.