Urgent.News

What's breaking now, across thousands of outlets.

Tech

Compromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPI

Unknown threat actors have managed to compromise two legitimate MemTensor packages across the npm and Python Package Index (PyPI) repositories to push a platform-specific Go-based implant dubbed sckit designed for Windows, Linux, and macOS. According to reports from Aikido, SafeDep, Socket, and StepSecurity, the libraries in question below - @memtensor/memos-cloud-openclaw-plugin versions
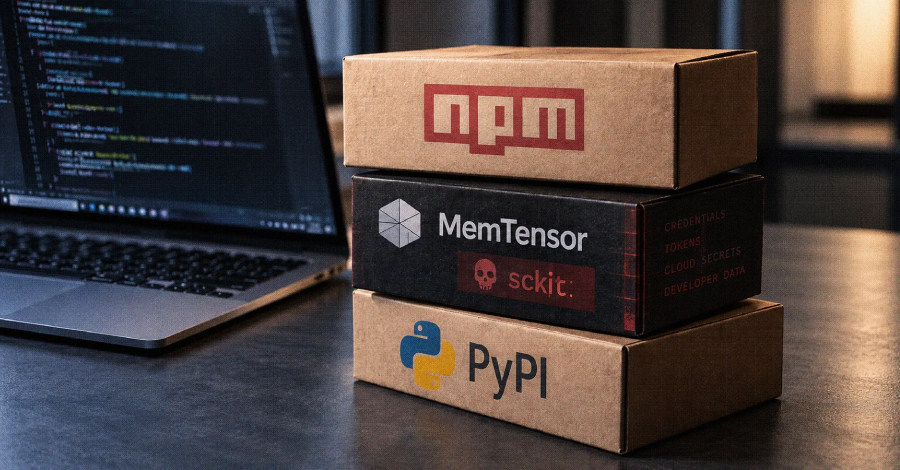
Compromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPI

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

📱 Let's learn System Design by designing WhatsApp

📱 System Design do WhatsApp Neste artigo, mostramos como o WhatsApp pode ser desenhado passo a passo, começando pelos problemas reais do sistema e descobrindo, a partir deles, os conceitos de…

  • WhatsApp designed step-by-step, starting with messaging problem
  • WebSocket as persistent, bidirectional communication channel discovered
  • Load Balancer used to distribute connections among servers

Critical WordPress RCE vulnerability announced

A critical vulnerability has been discovered in WordPress 's get_page_template() function for page-template resolution that could allow remote-code execution (RCE) by an unauthenticated attacker, in…

More from Wednesday 23 September →