North Korean fake recruiters infect 30K devices, steal $10.7M in crypto
North Korean cyber group WaterPlum targeted developers with fake jobs at crypto, AI and NFT companies, infecting at least 30,000 devices across more than 100 countries.
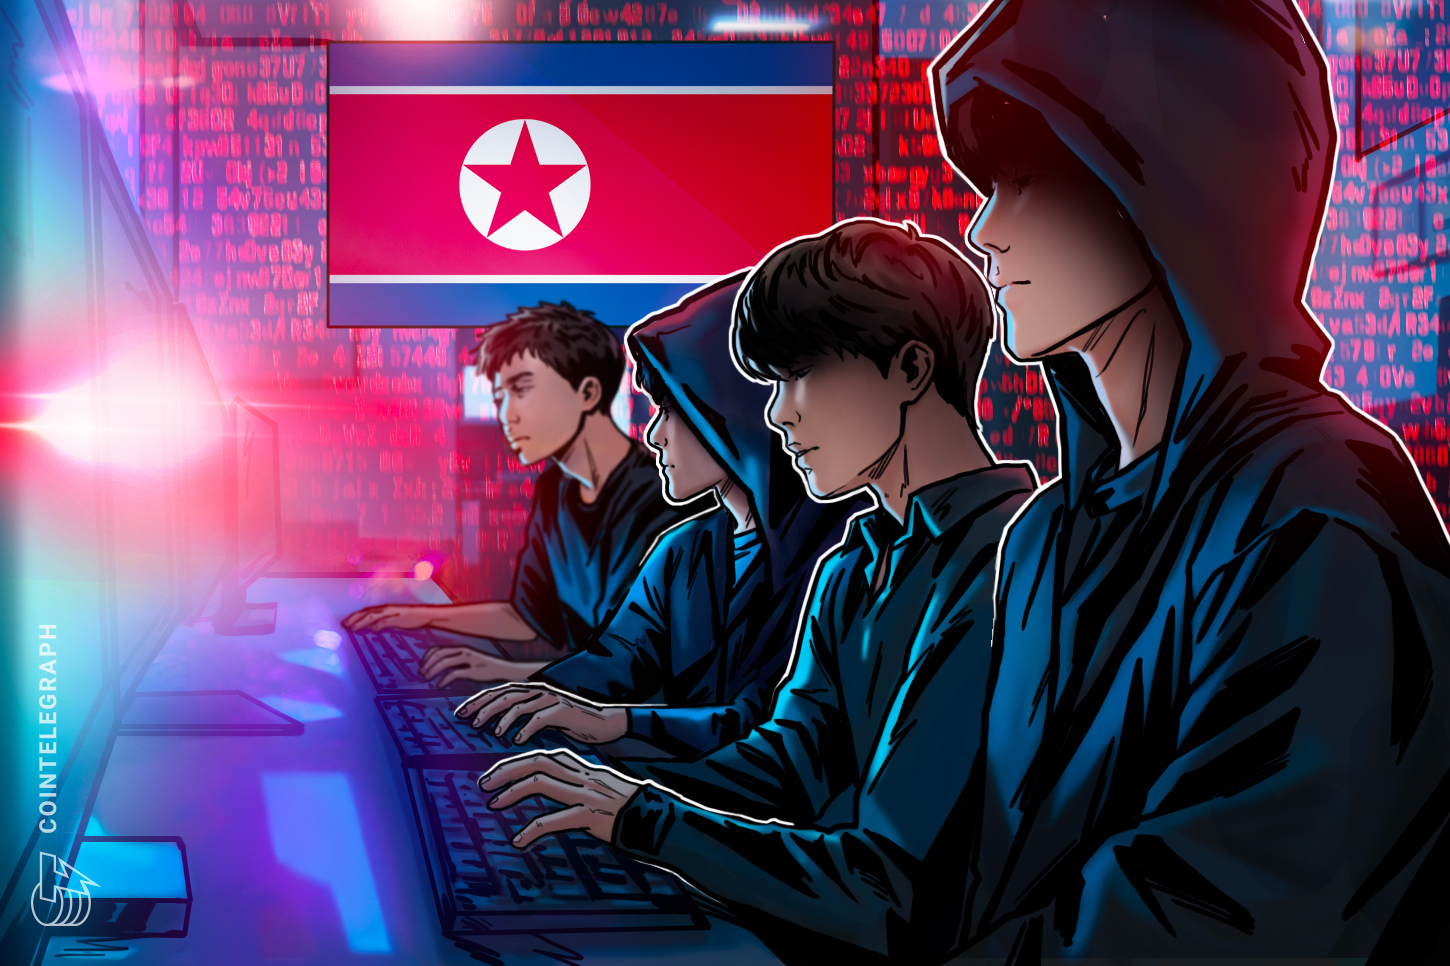
North Korean hacking group WaterPlum, also known as Contagious Interview, has targeted developers with fake job offers from crypto, AI, and NFT companies, infecting over 30,000 devices in more than 100 countries. These fake recruiters, impersonating legitimate AI, cryptocurrency, or NFT companies, have stolen at least $10.7 million by luring unsuspecting job seekers with malware.
The group primarily targets web designers, engineers, and specialists in cryptocurrency, blockchain, and Web3 technologies. WaterPlum's tactics include recruiting on social media, online platforms, gig work platforms, or freelance marketplaces. Once inside a victim's computer, they use remote-access trojans and infostealing malware to exfiltrate sensitive data and cryptocurrency.
The damage extends beyond stolen cryptocurrency, as stolen identity documents can enable North Korean IT workers to impersonate victims and earn income, or sensitive information can be used for extortion.
Written by urgent.news from Cointelegraph's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.