Thread-identity switcheroo for io_uring
We haven't written up this one. Lobsters has the full story — the link below goes straight to it.
This story
This is one outlet's version. Read the fullest account.
What's breaking now, across thousands of outlets.
We haven't written up this one. Lobsters has the full story — the link below goes straight to it.
This is one outlet's version. Read the fullest account.
The code is now available through Valve's GitLab repository. Read Entire Article
Patching Guide for CVE-2026-75650: Closing the Adobe Commerce RCE CVE-2026-75650 is a critical remote code execution vulnerability in Adobe Commerce, Adobe Commerce B2B and Magento Open Source.
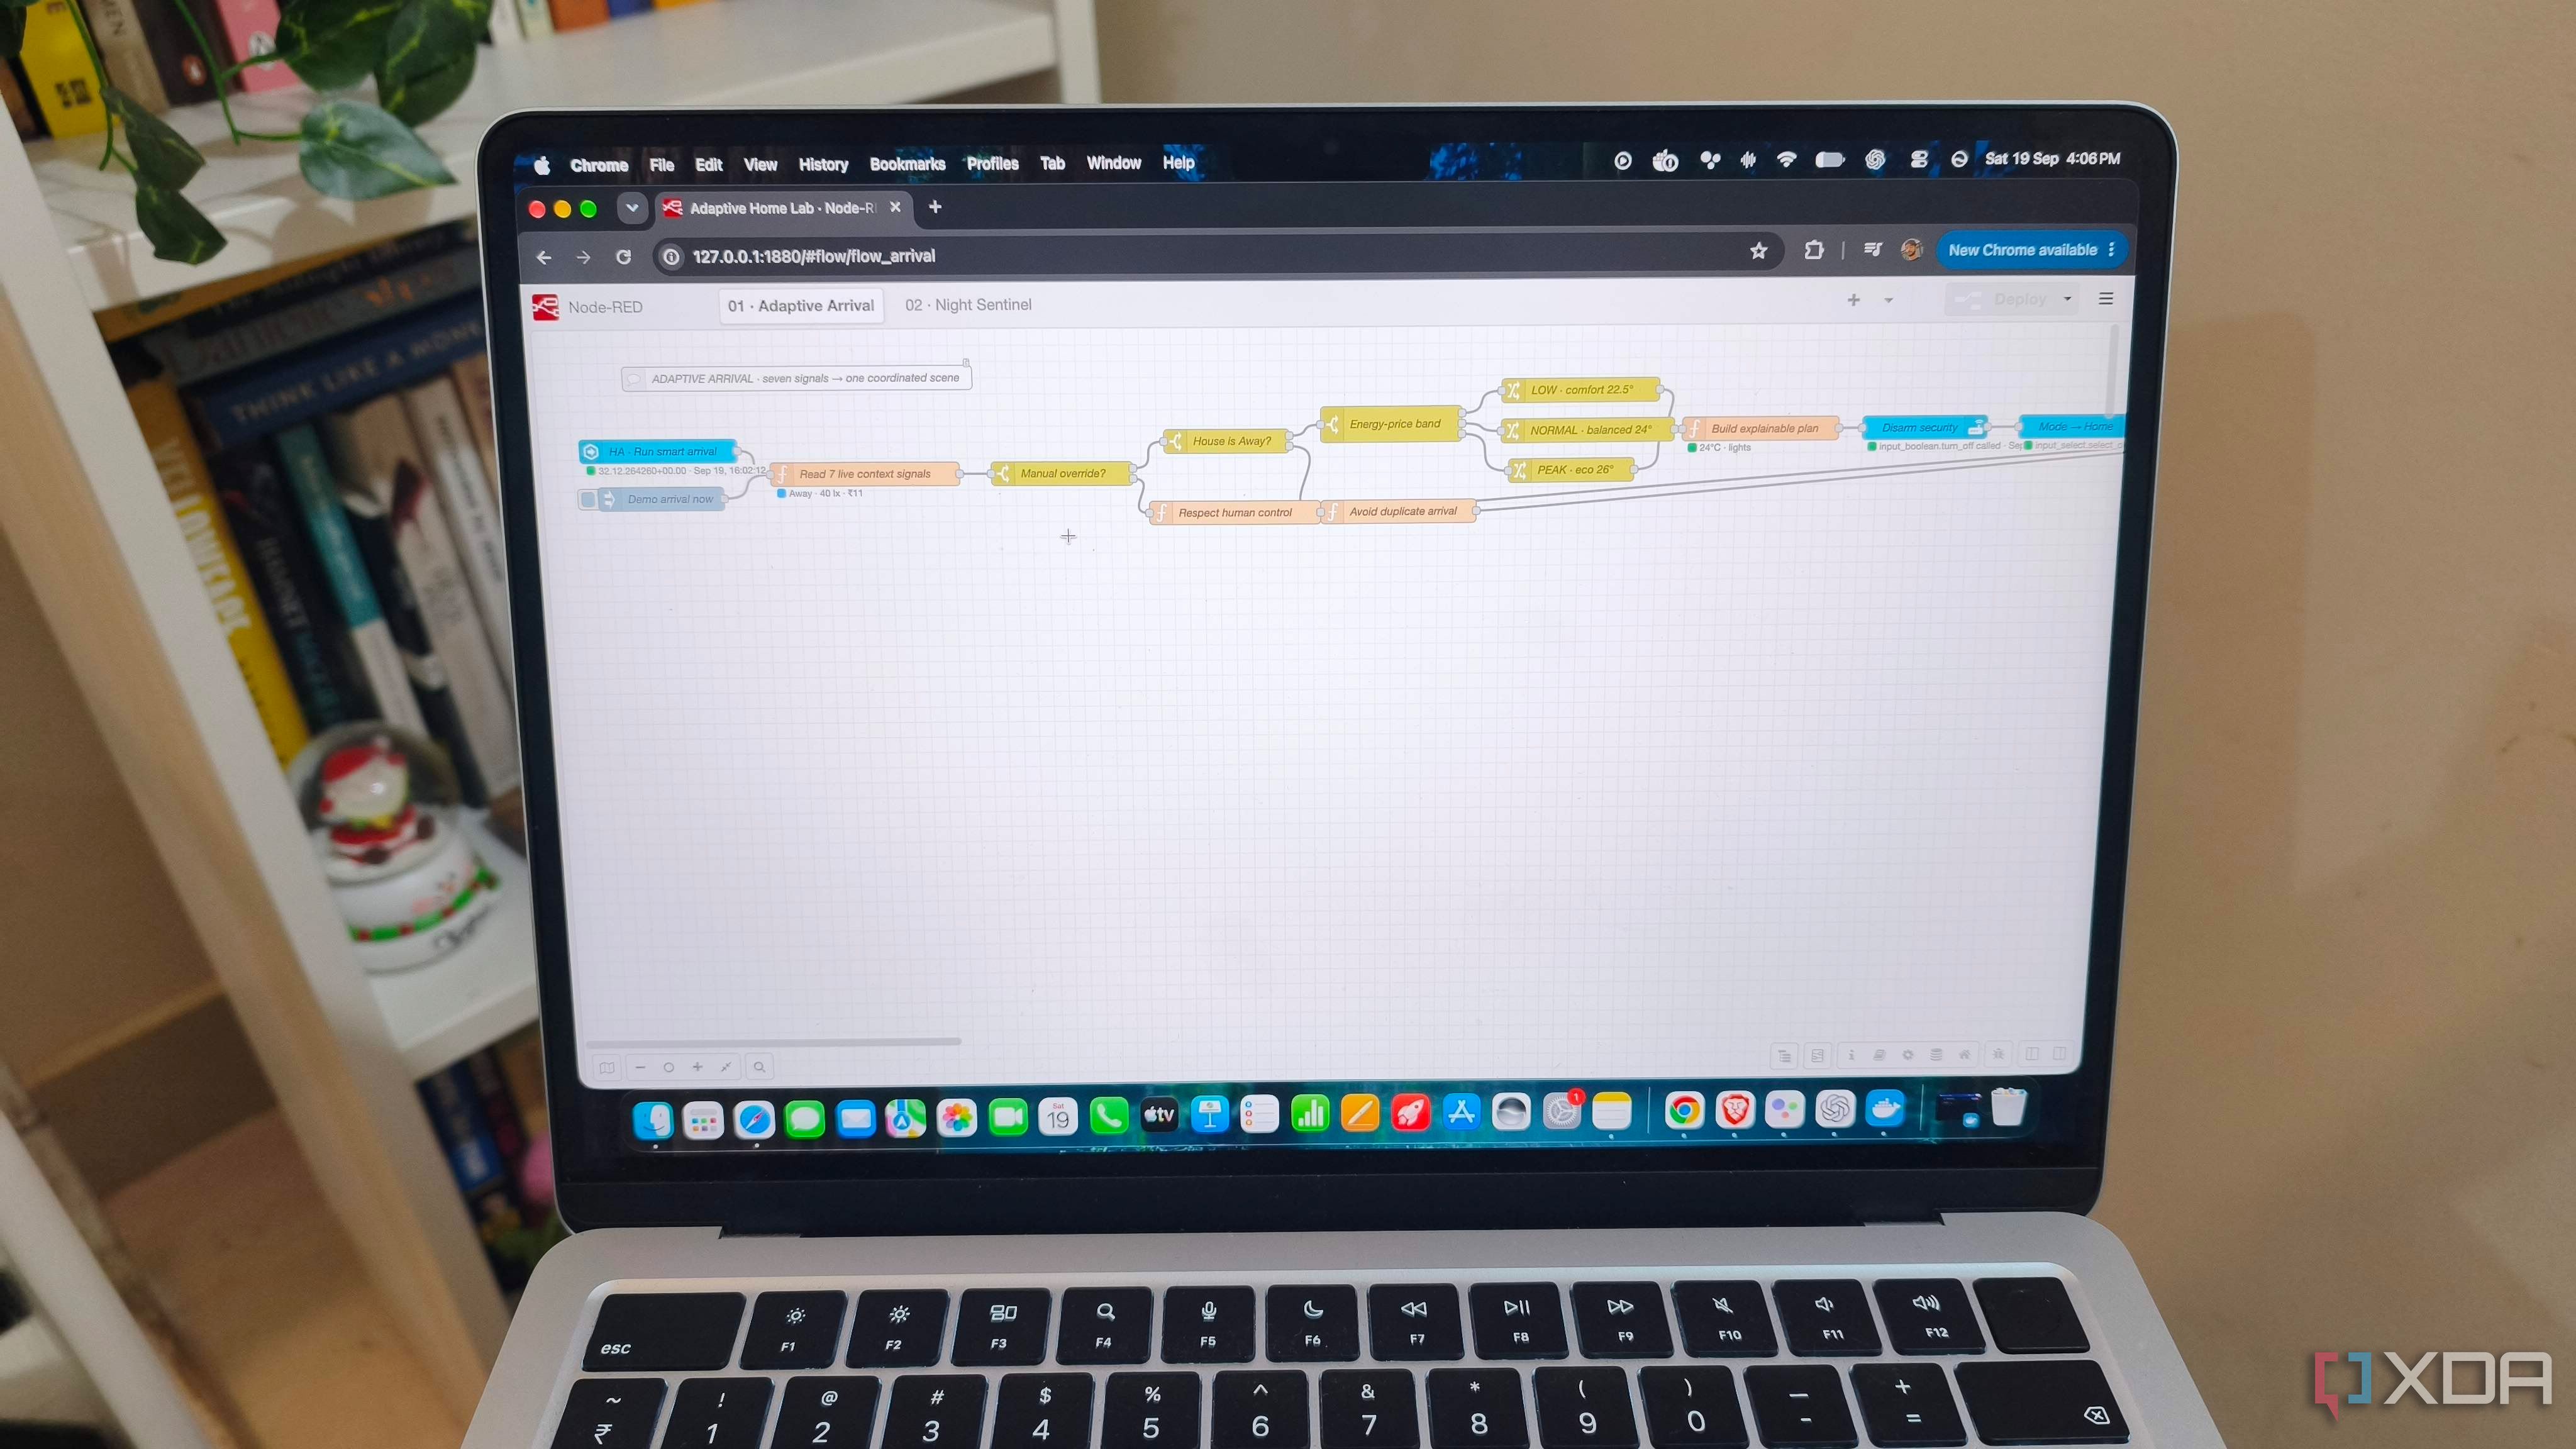
Home Assistant hit its limits
A behavioral security system rarely receives perfectly consistent evidence. Imagine one session produces: Network Signal → unusual request pattern Identity Signal → authenticated legitimate user Host…
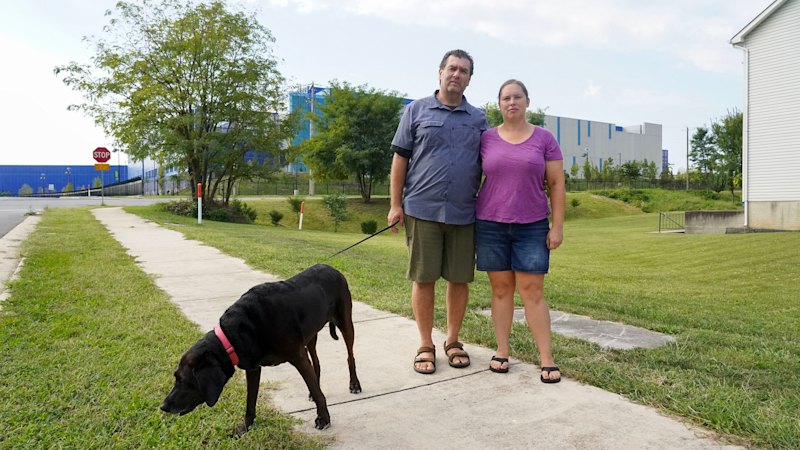
About 70 per cent of the world’s internet traffic flows through this county in Virginia. Whether it is a road map for Australia, or a cautionary tale, depends on who you ask.
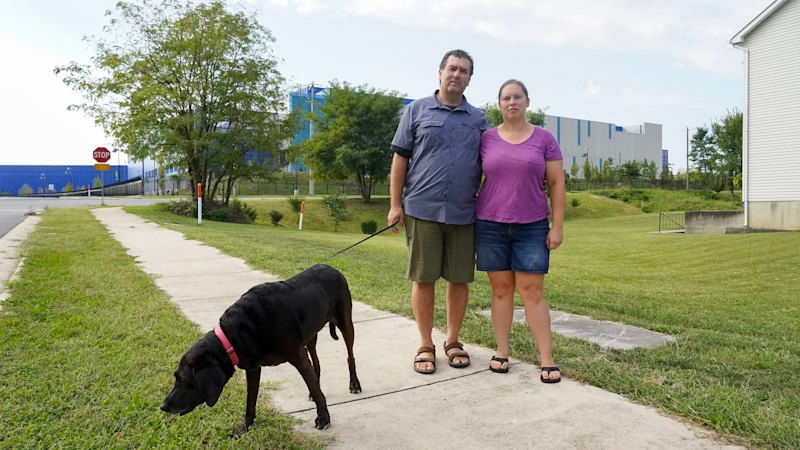
About 70 per cent of the world’s internet traffic flows through this county in Virginia. Whether it is a road map for Australia, or a cautionary tale, depends on who you ask.