Home Assistant couldn't do the automation I wanted, so I linked it to Node-RED instead
Home Assistant hit its limits
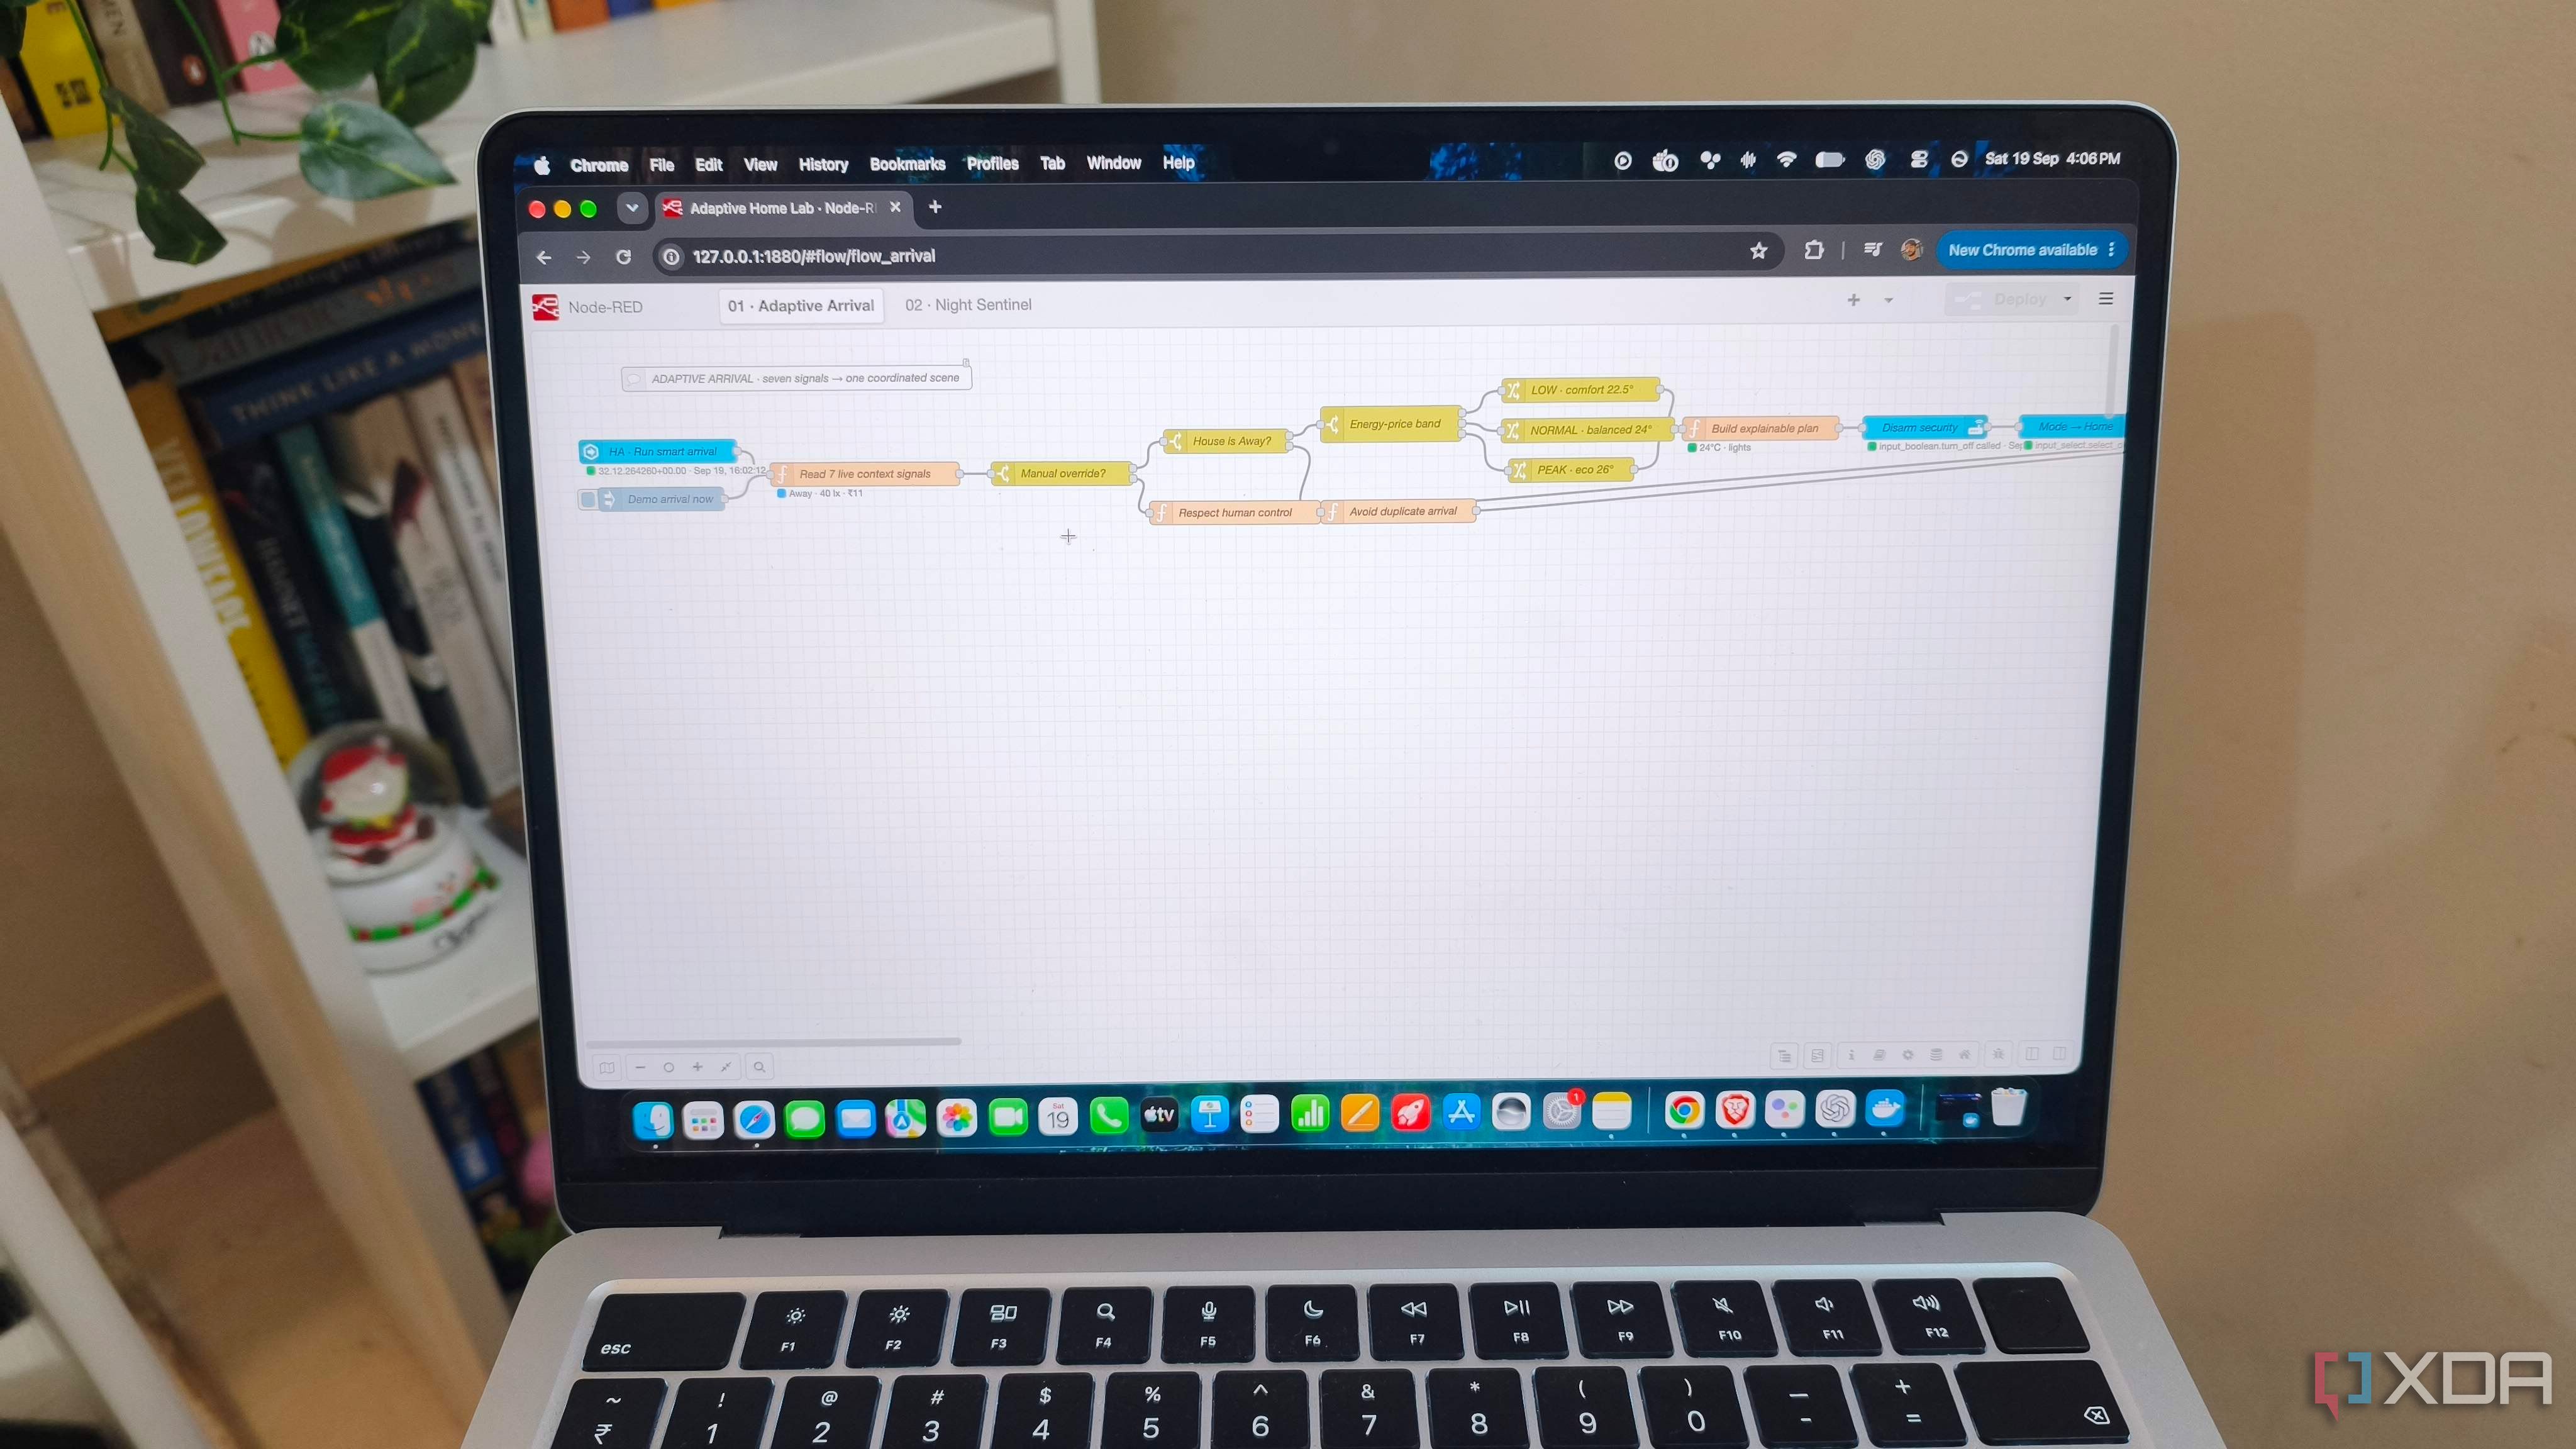
Home Assistant is a useful tool for integrating smart home devices and automating basic tasks, such as turning on lights or air conditioners under certain conditions. However, for more complex automations, it may not be the best option, according to XDA Developers.
One user, a Lead QA Engineer, found Home Assistant limited in its capabilities and decided to link it to Node-RED for more advanced automation. The user wanted to automate tasks such as opening the garage door from their car screen and creating a pop-up on their phone when arriving home to open gates in sequence.
The user has now set up 99 automations using Home Assistant and Node-RED, including tasks such as controlling floor heating and cooling, air and appliances, and protecting the home. Dev.to reports that the user was able to automate tasks such as opening gates, despite them running on Alfred Smart, an access control system.
Brief written by urgent.news from XDA Developers, Dev.to — 2 reports on this story. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.