Zero-day flaws in TP-Link security cameras could let hackers eavesdrop on you — but there's a fix
Security researchers discovered zero day flaws that could let hackers eavesdrop on you via TP-Link C200 cameras.
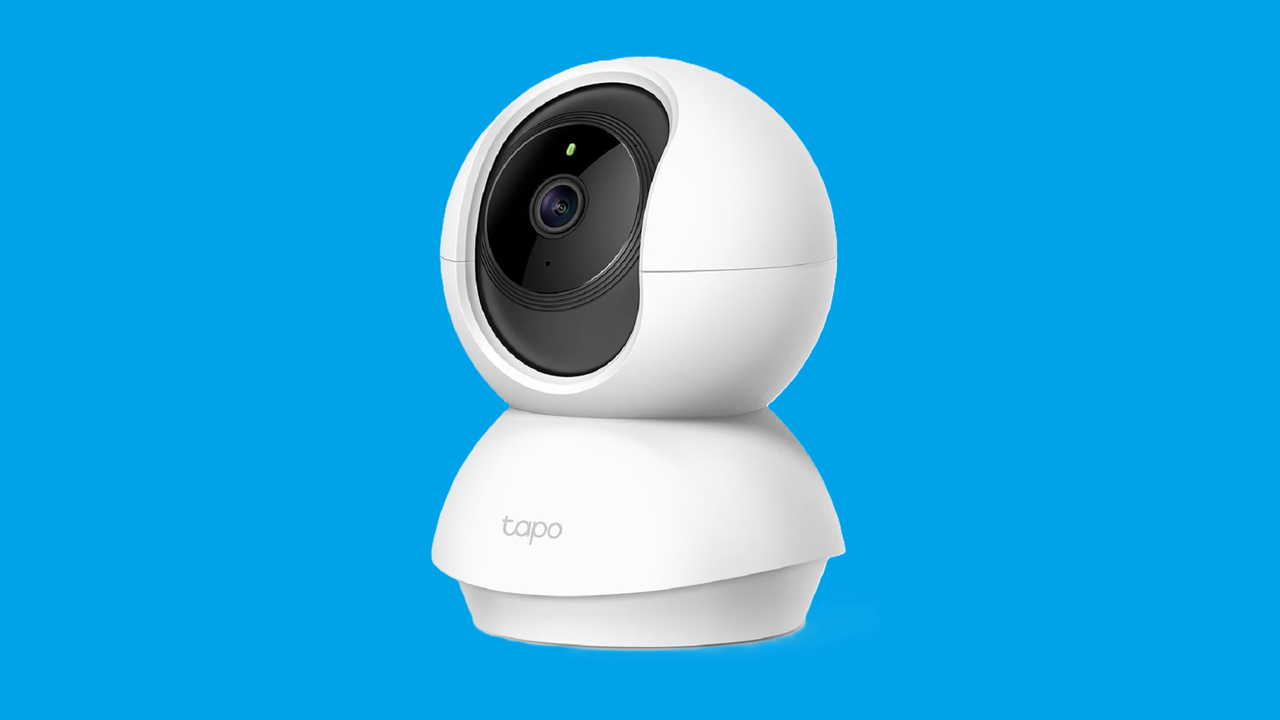
If you own a TP-Link Tapo C200 security camera, it is crucial to update its firmware immediately. Recently, security researchers OPSWAT discovered two critical zero-day vulnerabilities (CVE-2026-15315 and CVE-2026-15316) in these cameras that could enable hackers to eavesdrop on users. These flaws could allow an attacker with network access to gain administrative privileges, enabling them to modify device settings and access live video streams and stored recordings.
This vulnerability poses a serious risk, especially since these cameras are often used for sensitive purposes such as monitoring babies or homes. When notified about these vulnerabilities, TP-Link immediately took action to investigate and develop firmware updates. The company strongly encourages all Tapo C200 users to update their devices to the latest firmware version (V5-1.4.6 Build 260709), which was released on August 17.
The vulnerabilities have been remediated in this update. To update your camera, simply use the Tapo app available on the Tapo C200 Downloads page. If you require further assistance or support, you can access relevant information on the company's website.
Written by urgent.news from Tom's Guide's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.