Watch out — TP-Link Tapo Camera vulnerabilities could let hackers spy inside homes, so patch now
A firmware update is now available to fix the issues.
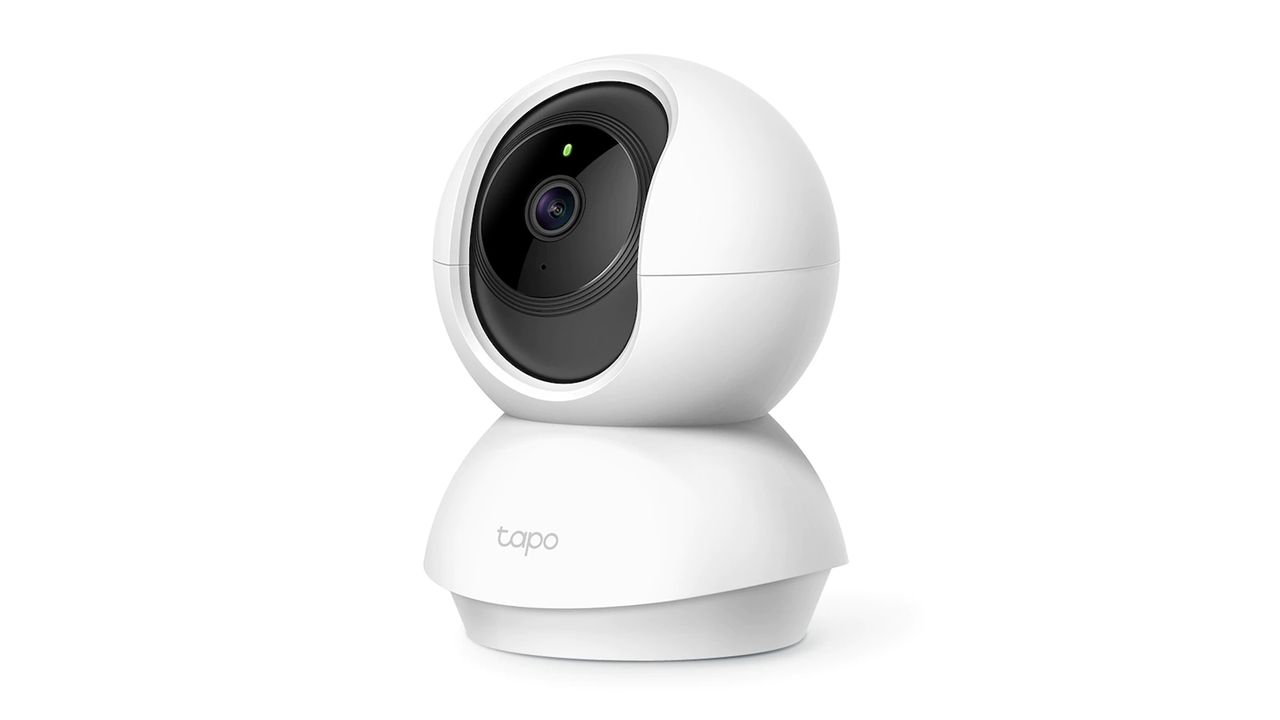
Two critical vulnerabilities have been discovered in TP-Link's Tapo C200 smart cameras, which could enable hackers to spy on users' homes and businesses. The security flaws, disclosed by Opswat, include an authentication bypass vulnerability (CVE-2026-15315) and a denial-of-service vulnerability (CVE-2026-15316). The authentication bypass flaw, rated 8.7/10 for severity, allows unauthenticated attackers to obtain valid admin sessions without a password, giving them control over the device and the ability to view the live stream.
The denial-of-service vulnerability, rated 7.1/10 for severity, can cause the camera to crash or restart when oversized crypted ciphertext values are sent. TP-Link released firmware version V5_1.4.6 on August 18, 2026, to patch both vulnerabilities. Users are strongly advised to update their devices immediately. While the potential for abuse exists, experts note that exploiting these vulnerabilities likely requires local network access, making them less of an immediate threat for most home users.
Written by urgent.news from TechRadar's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.