ITWebTV Biz: The architecture of AI-native cyber defence
How intelligent detection, digital twins and purpose-built models are reshaping what cyber defence looks like.
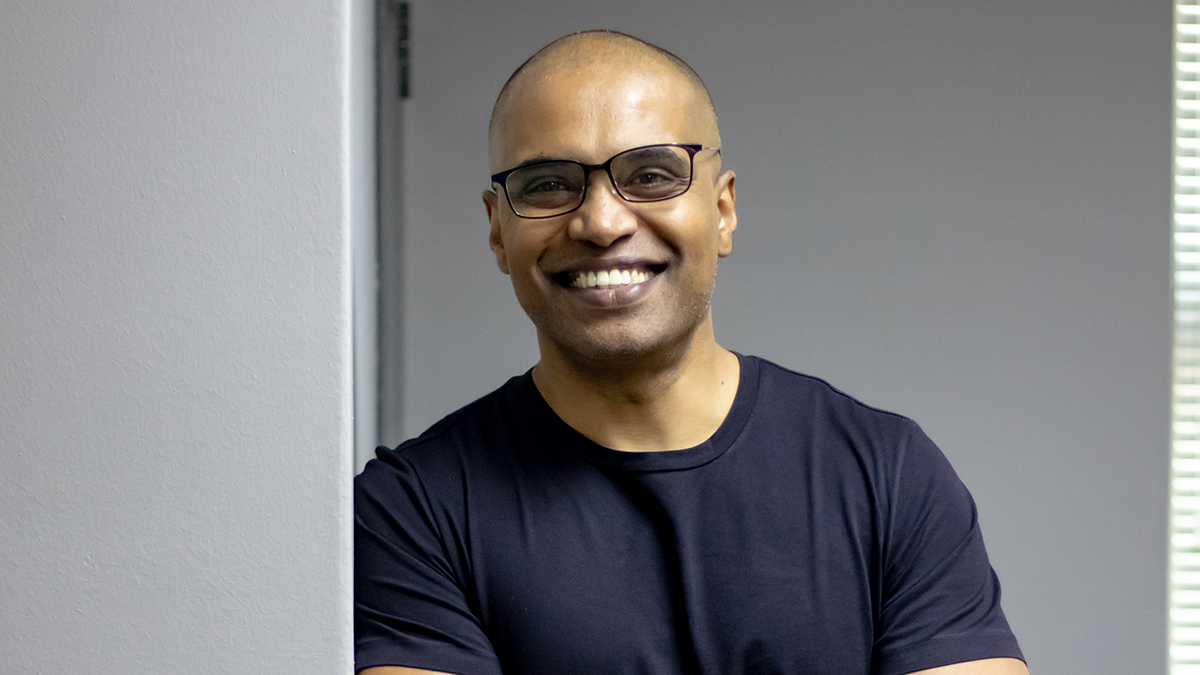
Snode Technologies, a cyber defence company based in Centurion, has been leveraging artificial intelligence (AI) for over a decade, even before it became a popular industry term. Founder and CEO Nithen Naidoo explains that the company was initially seeking a solution to keep pace with the rapid evolution of cyber threats, which signature-based detection methods were failing to address.
In 2017, Snode shifted its focus to machine learning and deep neural networks, integrating AI into both its product design and development process.
Naidoo emphasizes that AI is not intended to replace humans in the development cycle, but rather to enhance their capabilities, similar to the concept of intelligence amplification. He describes the synergy between humans and AI as a way to leverage the strengths of both, rather than relying on either exclusively. Snode's approach involves working with behaviors rather than isolated indicators like IP addresses and file hashes, enabling the company to correlate activity from various sources into a single, contextualized view of an attacker's kill chain.
The company's digital twin takes this further by simulating how active threat actors would move through an organization's real environment, providing security teams with a precise understanding of the most critical exposures and what to address first. Rather than relying on public large language models, Snode trains its own small language models using a decade's worth of analyst and client data, synthesized into hyper-specific, lightweight, and portable models that can run at the edge on IoT sensors, phones, and even satellites.
Naidoo stresses that these smaller models are easier to understand and trust, as they are not as opaque as black boxes. He believes that in a hyper-connected world, AI-native cyber defence must be fast enough to keep up with the speed of attacks, as knowing about an attack five minutes after it has happened is simply too late.
Written by urgent.news from ITWeb's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.