IRCTC to upgrade ticket booking system to reduce disruptions during peak hours
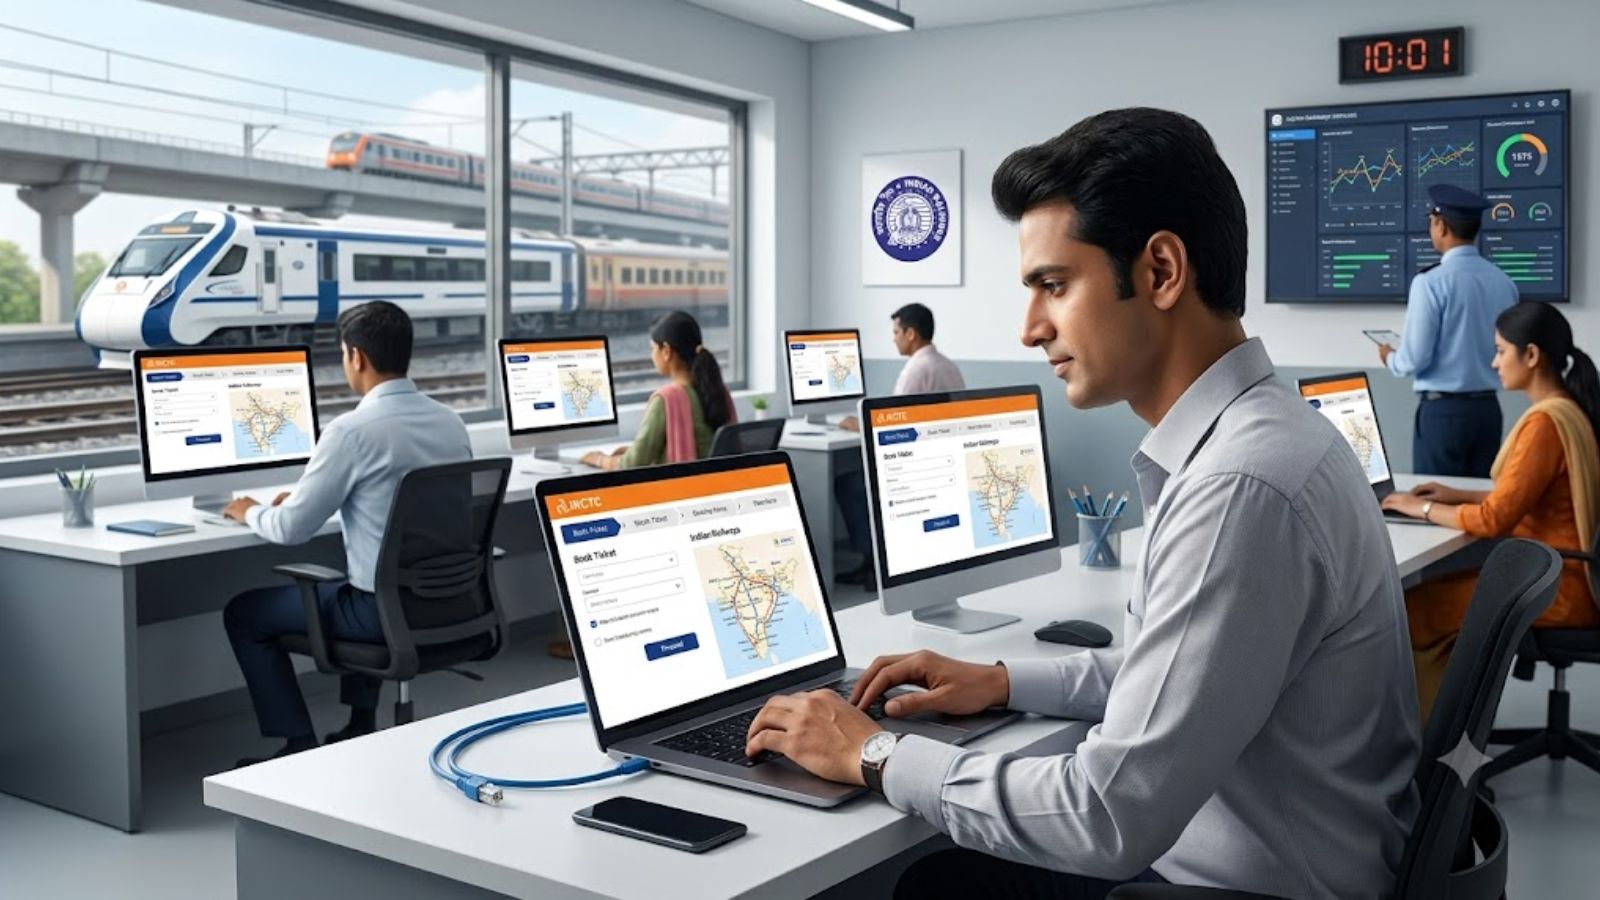
Indian Rail Catering and Tourism Corporation (IRCTC) is set to enhance its ticket booking platform to minimize disruptions during high-traffic periods and enhance the online booking experience. The corporation aims to bolster system reliability, accommodate heavy traffic, and facilitate seamless train ticket reservations. As of now, roughly 89% of all confirmed train tickets are purchased online.
Between June 2025 and June 2026, passengers booked 65.08 crore reserved tickets via the Public Reservation System (PRS), with 57.90 crore of those transactions occurring online. During peak booking times, such as the 8 am commencement of the Advance Reservation Period (ARP) and the 10 am launch for AC class reservations and 11 am for non-AC class bookings, heavy website traffic occasionally led to disruptions.
To mitigate these issues, IRCTC is implementing upgrades to its Next Generation e-Ticketing (NGET) system, which was initially launched in 2014 to augment online ticket booking capacity and passenger satisfaction. IRCTC disclosed plans for two primary upgrades: an NGET infrastructure enhancement, encompassing server, storage, networking, and software improvements, and the deployment of an active-active disaster recovery system to guarantee uninterrupted services in the event of a system failure.
This disaster recovery measure is particularly crucial during high-traffic booking periods, as even a brief outage could significantly impact passengers. IRCTC also emphasized its commitment to thwarting unauthorized and suspicious users from overwhelming the website during peak hours, particularly around 8 am, 10 am, and 11 am.
The corporation has bolstered its systems by incorporating Akamai for bot mitigation and content delivery, managing website traffic via offloading static content, and instituting a 30-minute maximum usage limit for agents.
Written by urgent.news from The Indian Express's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.